Framework Structure Of Online Security Vulnerability Remedy Software ...

Following slide highlights online security vulnerability remedy software framework structure for gaining competitive advantage. It further includes hunters, submit vulnerability reports, report to sync, customer, etc.

Following slide highlights online security vulnerability remedy software framework structure for gaining competitive advantage. It further includes hunters, submit vulnerability reports, report to sync, customer, etc.
Vulnerability Management Framework

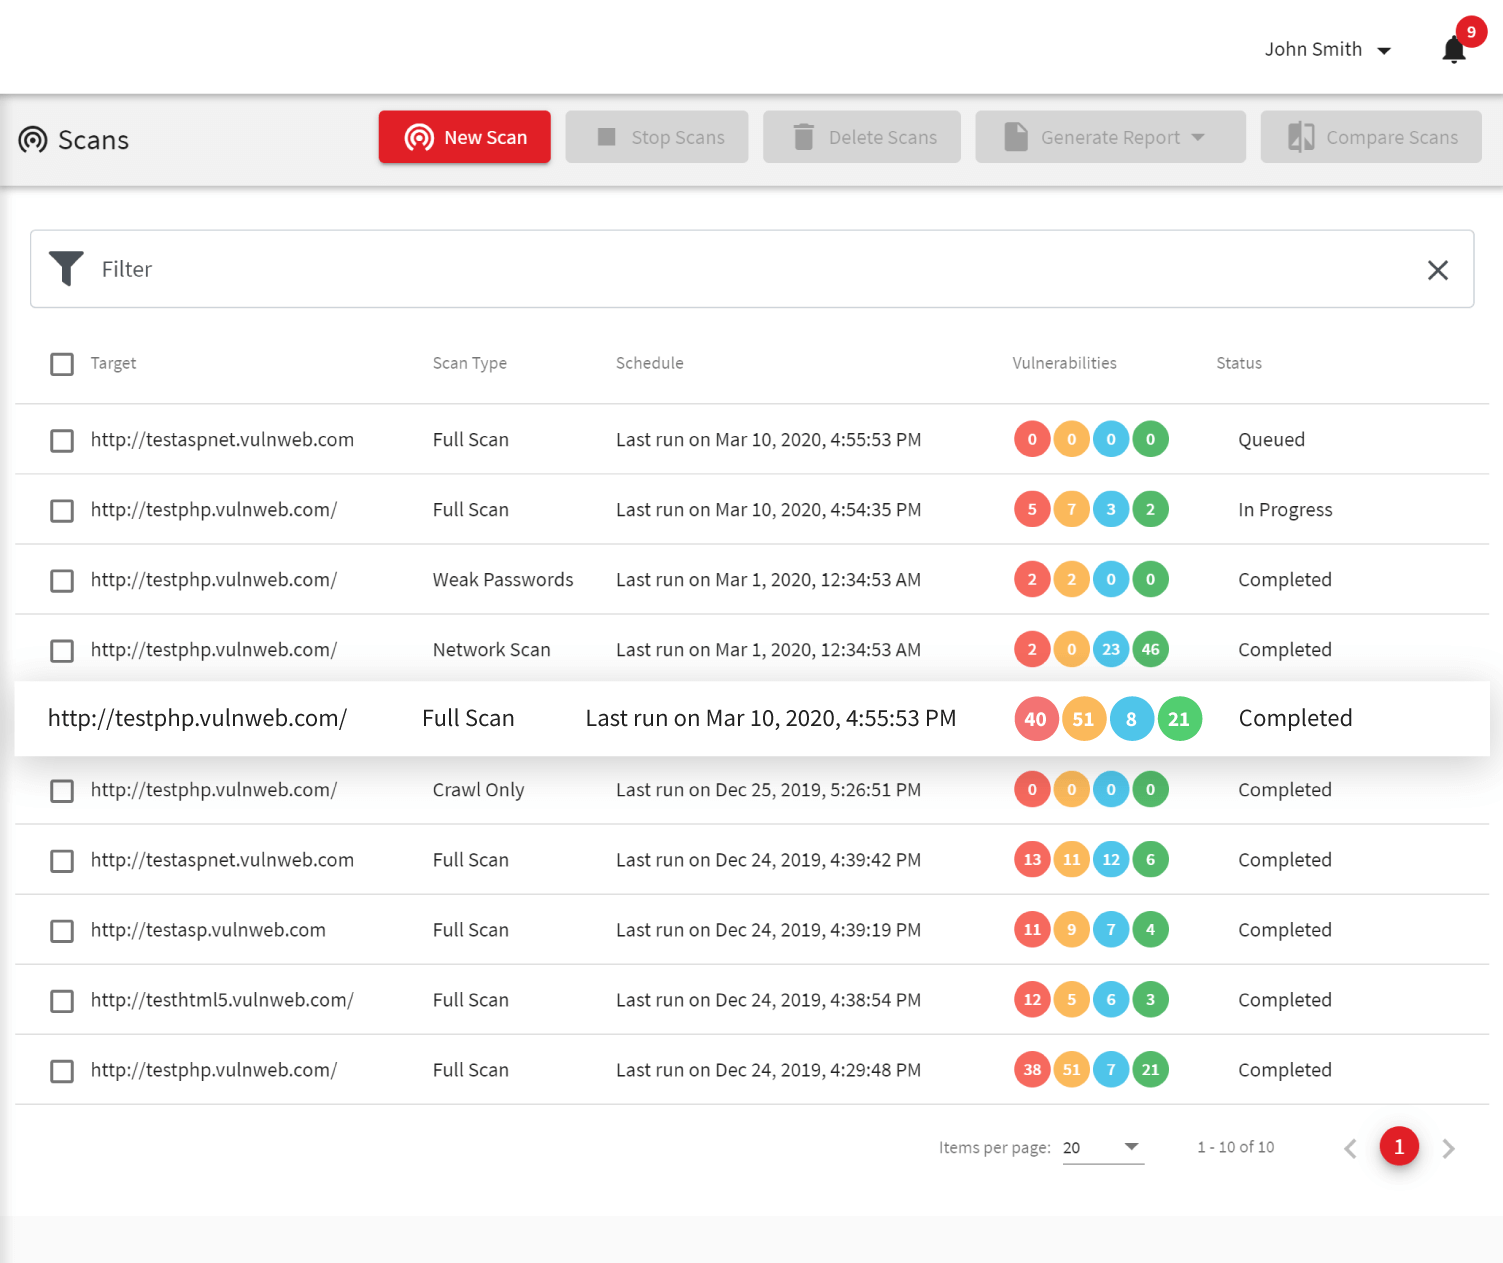
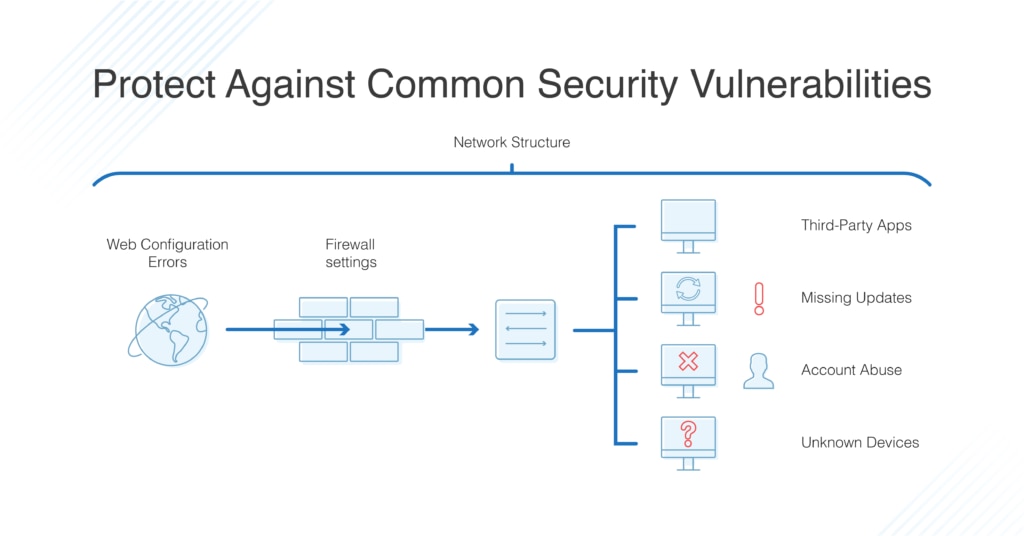
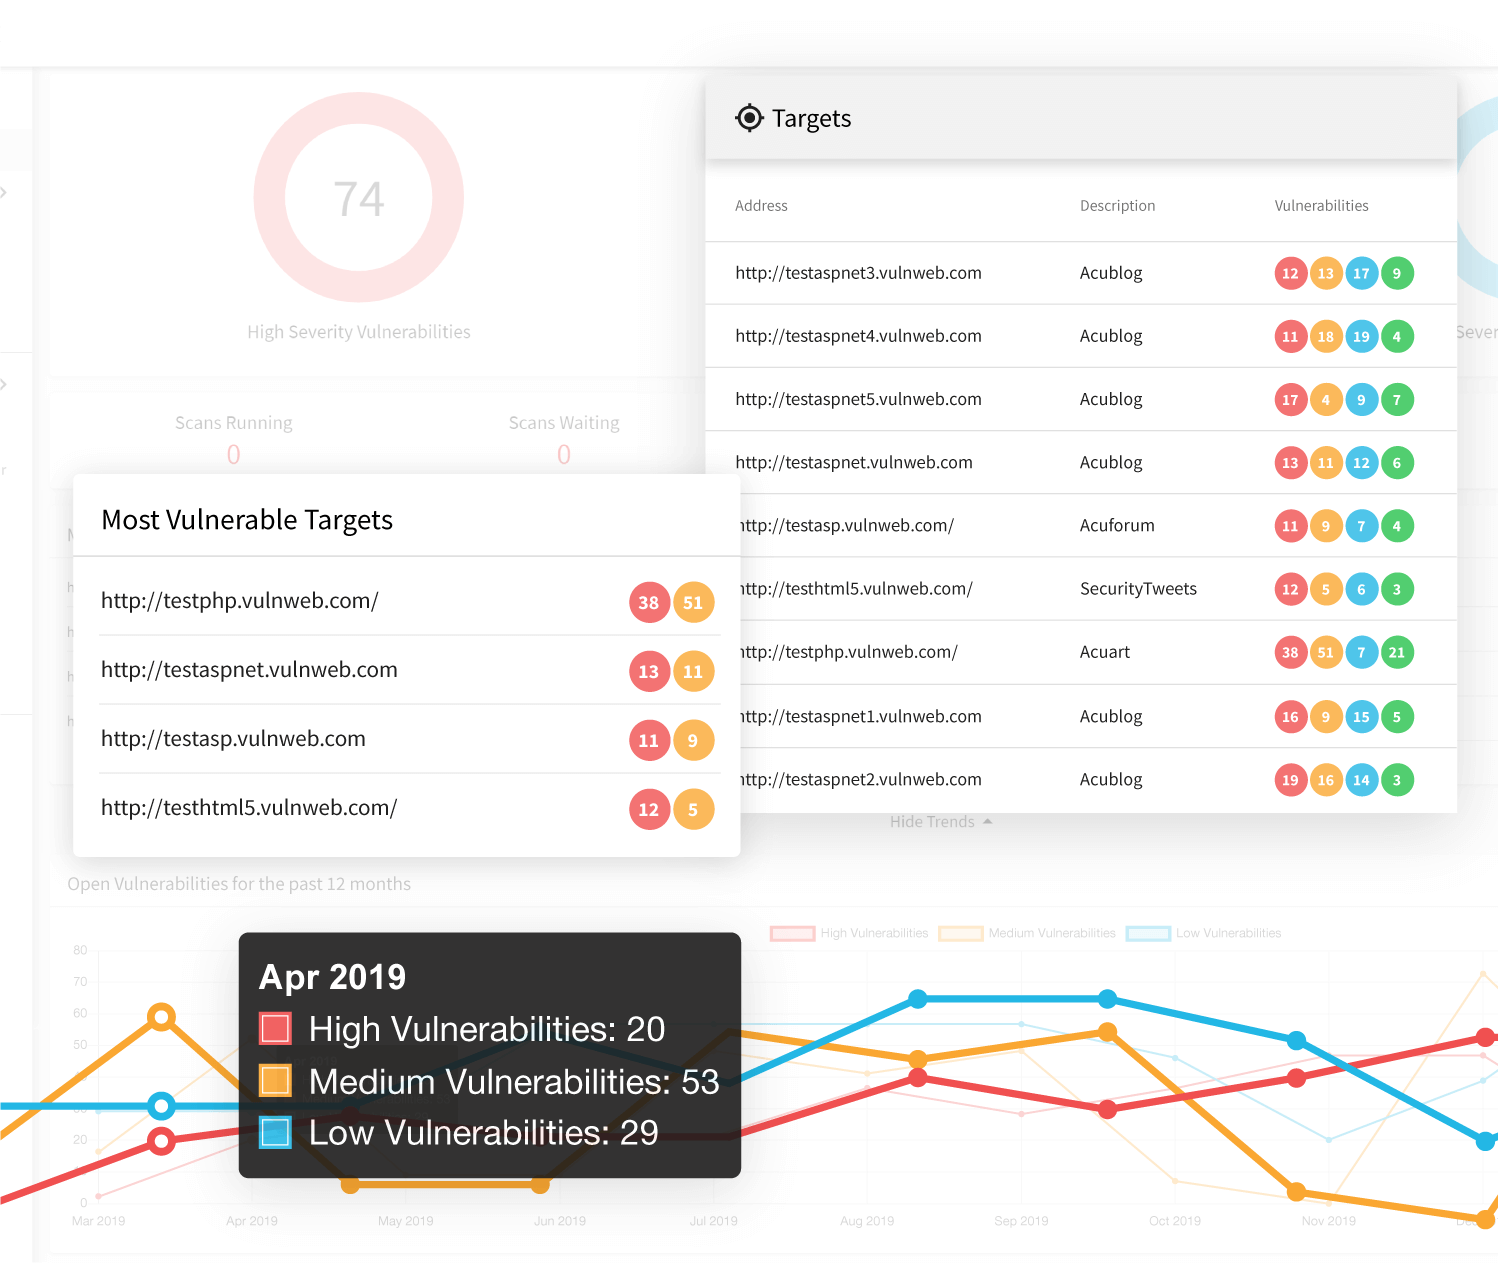
A vulnerability management framework provides a set of guidelines and best practices to help you quickly identify and patch security flaws and improve your cybersecurity posture. It facilitates the process of discovering, assessing, prioritizing and remediating software vulnerabilities.
At the heart of any vulnerability management framework lies a vulnerability assessment, which refers to the process of identifying weaknesses in software , hardware, and network components that could potentially be exploited. A vulnerability assessment framework includes a methodology, tools, and processes to evaluate security risks systematically.
What is Vulnerability Management Framework
Discover vulnerability management frameworks , their components, compliance alignment, key steps, and best practices for effective security .
A cloud vulnerability management program establishes the organizational framework that transforms vulnerability discovery into measurable risk reduction across your enterprise cloud infrastructure.

Vulnerability Assessment Framework
A vulnerability assessment framework offers that structure to facilitate scanning, risk assessment, and remediation activities in an organization. Companies that do not use these frameworks are vulnerable to gaps in cloud environments, networks, and containerized applications.
This draft explains how to find, filter, and apply informative references using NIST tools. Review and submit comments here. The final version of NIST Cybersecurity Framework 2.0: Cybersecurity, Enterprise Risk Management, and Workforce Management Quick-Start Guide

OWASP Vulnerability Management Guide
The vulnerability management guide should help to breakdown vulnerability management process into a manageable repeatable cycles tailored to your organizational needs. Target audience: information security practitioners of all levels, IT professionals, and business leaders.



The Cybersecurity Framework (CSF) 2.0 is designed to help organizations of all sizes and sectors — including industry, government, academia, and nonprofit — to manage and reduce their cybersecurity risks.