Using PSFTP with Private Key: Secure File Transfers Made Reliable
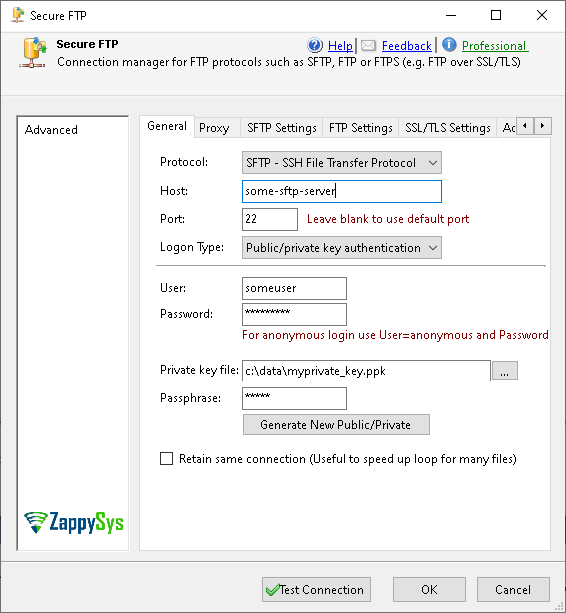
If you've ever needed to transfer files between machines over SSH, chances are you've bumped into PSFTP. It's a lean, no-nonsense SFTP client that ships as part of the PuTTY suite, and when paired with private key authentication, it becomes a seriously powerful tool for automating secure file transfers. No more punching in passwords every time—just point PSFTP at your target server, hand it your private key, and let it do the heavy lifting.
What Is PSFTP Exactly?
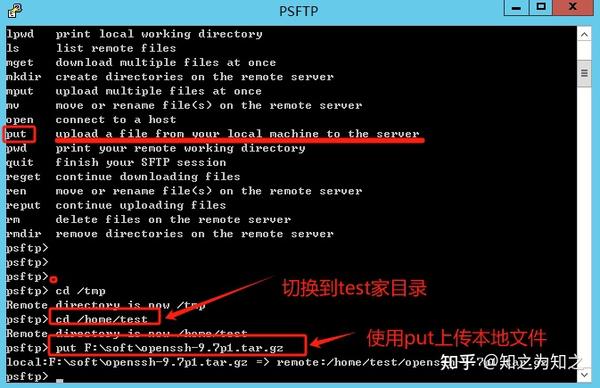
Psftp is the command-line SFTP client bundled with PuTTY, the venerable terminal emulator beloved by sysadmins and developers alike. While PuTTY handles interactive sessions, psftp drops you straight into an SFTP shell where you can list directories, upload and download files, and manage remote file systems—all over an encrypted SSH tunnel. Think of it as sftp from OpenSSH but with PuTTY's own flavor of key management.
Why Use a Private Key?
Passwords are fine for one-off logins, but they crumble under automation. A private key gives you:
- Non-interactive authentication – scripts don't need human intervention.
- Stronger crypto – RSA, ECDSA, or Ed25519 keys are orders of magnitude harder to brute-force than any password.
- Revocability – swap out a compromised key without changing the password for every user.
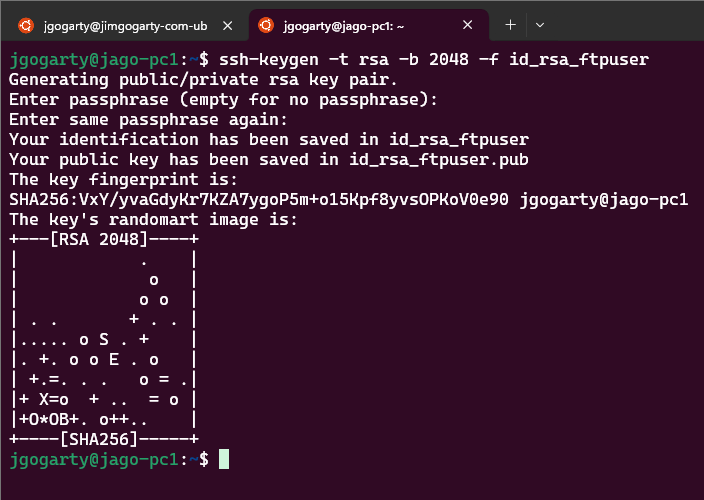
Generating and Converting Your Key
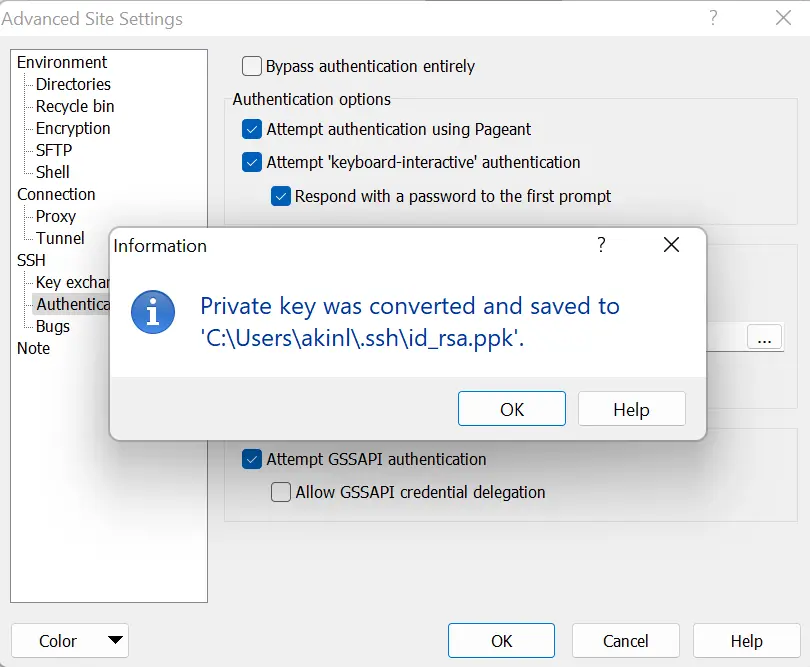
PuTTY uses its own key format (.ppk), but most SSH keys come as OpenSSH PEM files. Fire up puttygen.exe:
- Open Puttygen → Conversions → Import key → Select your OpenSSH private key.
- Optionally add a passphrase for an extra layer of protection.
- Save the private key as a
.ppkfile.
Keep that .ppk file safe—it's the golden ticket to your servers.
Basic PSFTP Command with Private Key
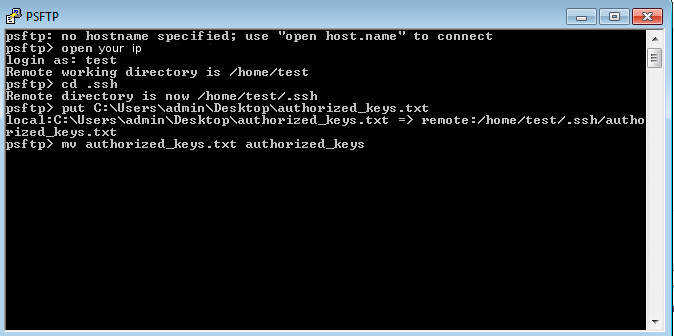
Launch PSFTP and connect:

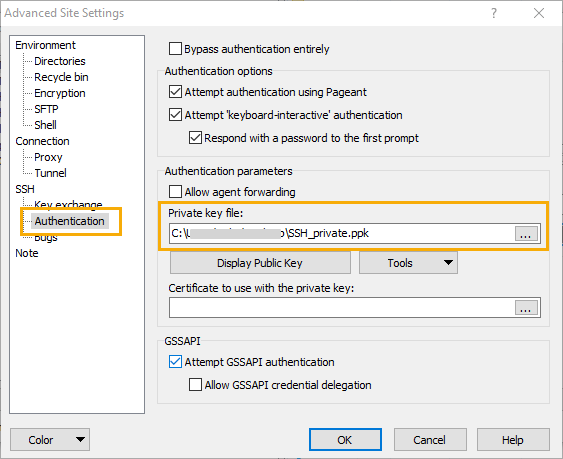
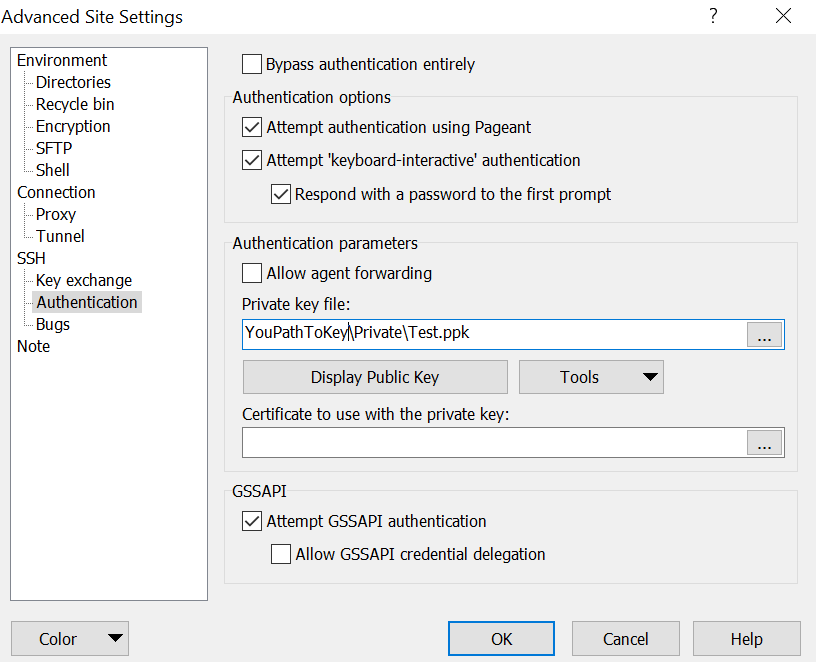
psftp user@yourserver.com -i C:\path\to\your\key.ppkThat single -i flag tells psftp to use your private key instead of prompting for a password.
Automating Transfers with a Script
Drop commands into a plain-text file—say, sftp_commands.txt:
put localfile.txt /remote/path/file.txt
chmod 644 /remote/path/file.txt
get /remote/path/file.txt local_backup.txt
quit
Then run:
psftp user@yourserver.com -i C:\path\to\key.ppk -b sftp_commands.txtEvery command executes in sequence, no human in the loop required.
Common Flags Worth Knowing
| Flag | What It Does |
|---|---|
-i <key> | Specify the private key file |
-b <file> | Batch mode: read commands from a file |
-P <port> | Use a non-default SSH port |
-v | Verbose output for troubleshooting |
Security Best Practices
Private keys are powerful, so treat them that way:
- Store keys with strict permissions—ideally
600on Linux, read-only for the owning user on Windows. - Never commit them to version control.
- Rotate keys annually or whenever team members leave.
- Use a hardware token (YubiKey, Nitrokey) for high-value servers.
Troubleshooting Connection Issues
Permission denied? Double-check that the public key is in ~/.ssh/authorized_keys on the remote side. Wrong key format? Make sure you converted it to .ppk. Timeout? Verify the SSH port and firewall rules. A quick psftp -v user@host -i key.ppk will spill the debug logs and usually point you right at the culprit.
Armed with a private key and a handful of commands, PSFTP turns repetitive file transfers into a set-and-forget operation. Automate early, automate often.