In an era dominated by the constant stream of audiovisual content, the sanctity of personal information within video streams has emerged as a critical concern for individuals and organizations alike. "Video private info" typically encompasses any identifiable or sensitive personal data that can be captured, shared, or inferred from video formats. This spans far beyond a simple likeness; it includes biometric data like facial geometry and gait patterns, location metadata embedded in video files, audio recordings that may contain confidential conversations, and even contextual details about one's private life inadvertently displayed in the background of a recording. The proliferation of video-sharing platforms, smart home devices, and video conferencing tools has exponentially increased the surfaces through which such data can be harvested, often without the explicit knowledge or consent of the individual. Understanding the scope of this data is the first step toward implementing robust protection strategies.
Understanding the Spectrum of Private Information in Video Data
Private information in video is not monolithic; it exists on a spectrum of identifiability. Direct identifiers are unambiguous, such as a clear facial image or a license plate visible in the frame. Indirect identifiers, however, can be equally revealing. The unique architectural style of your home, the view from a window, or even patterns of daily activity reconstructed from video footage can de-anonymize an individual. Furthermore, metadata—the data about the data—presents a significant risk vector. Exchangeable Image File Format (EXIF) data can reveal the exact time, date, and GPS coordinates of a recording, while platform-specific analytics might encode the device used and network information. This layered nature necessitates a layered approach to security.
The Evolving Threat Landscape: How Video Data is Compromised
Threats to video private info are dynamic and multifaceted. The primary risks stem from intentional malicious actors exploiting vulnerabilities in storage, transmission, and processing. Weak encryption during video calls or cloud storage can lead to interception. Advanced techniques, like deepfakes, present a dual threat: not only can a person's likeness be stolen for fraud, but the underlying biometric data can be reverse-engineered to create more convincing synthetic media. Moreover, the aggregation of seemingly harmless video clips, linked through metadata, can paint an invasive picture of an individual's life pattern, valuable for social engineering or targeted advertising. The case of smart home devices is particularly salient; a baby monitor camera, if compromised, can reveal not just a child's image but daily routines, times when the house is empty, and private family interactions.
Technical and Organizational Safeguards for Protection
Mitigating these risks requires a combination of proactive measures. At a technical level, end-to-end encryption for video streams is paramount, ensuring data is only decipherable by intended recipients. For stored video, robust access controls and encryption-at-rest are essential. Employing real-time anonymization techniques, such as blurring faces or license plates in surveillance feeds, can protect identities in public deployments. For organizations, the principles of data minimization and strict access control are key. The following table outlines core safeguards by threat type.
| Threat Vector | Primary Technical Safeguard | Organizational Policy |
|---|---|---|
| Unauthorized Access to Stored Video | Strong encryption, multi-factor authentication for access | Principle of least privilege for data access logs |
| Inference from Metadata | Stripping EXIF data before sharing, anonymization tools | Regular audits of stored metadata practices |
| Real-Time Interception of Streams | End-to-end encryption, secure protocols (e.g., SRTP) | Employee training on secure meeting protocols |
| Deepfake Threats | Digital watermarking, liveness detection in facial recognition | Clear deepfake response and verification protocols |
Navigating the Legal and Regulatory Framework
Legal landscapes have struggled to keep pace with technological capabilities. Regulations like the General Data Protection Regulation (GDPR) in the EU and the California Consumer Privacy Act (CCPA) provide frameworks for consent and data minimization, but enforcement and scope are often jurisdiction-specific. One persistent challenge is the cross-border nature of data flows. A video taken in one country may be stored on a server in another. This complexity demands that organizations stay abreast of evolving laws. Future regulations may increasingly focus on algorithmic transparency—requiring companies to disclose how they use and process video data beyond its intended purpose, putting the onus of responsible data use firmly on organizations.
The Human Element: Cultivating a Culture of Privacy Awareness
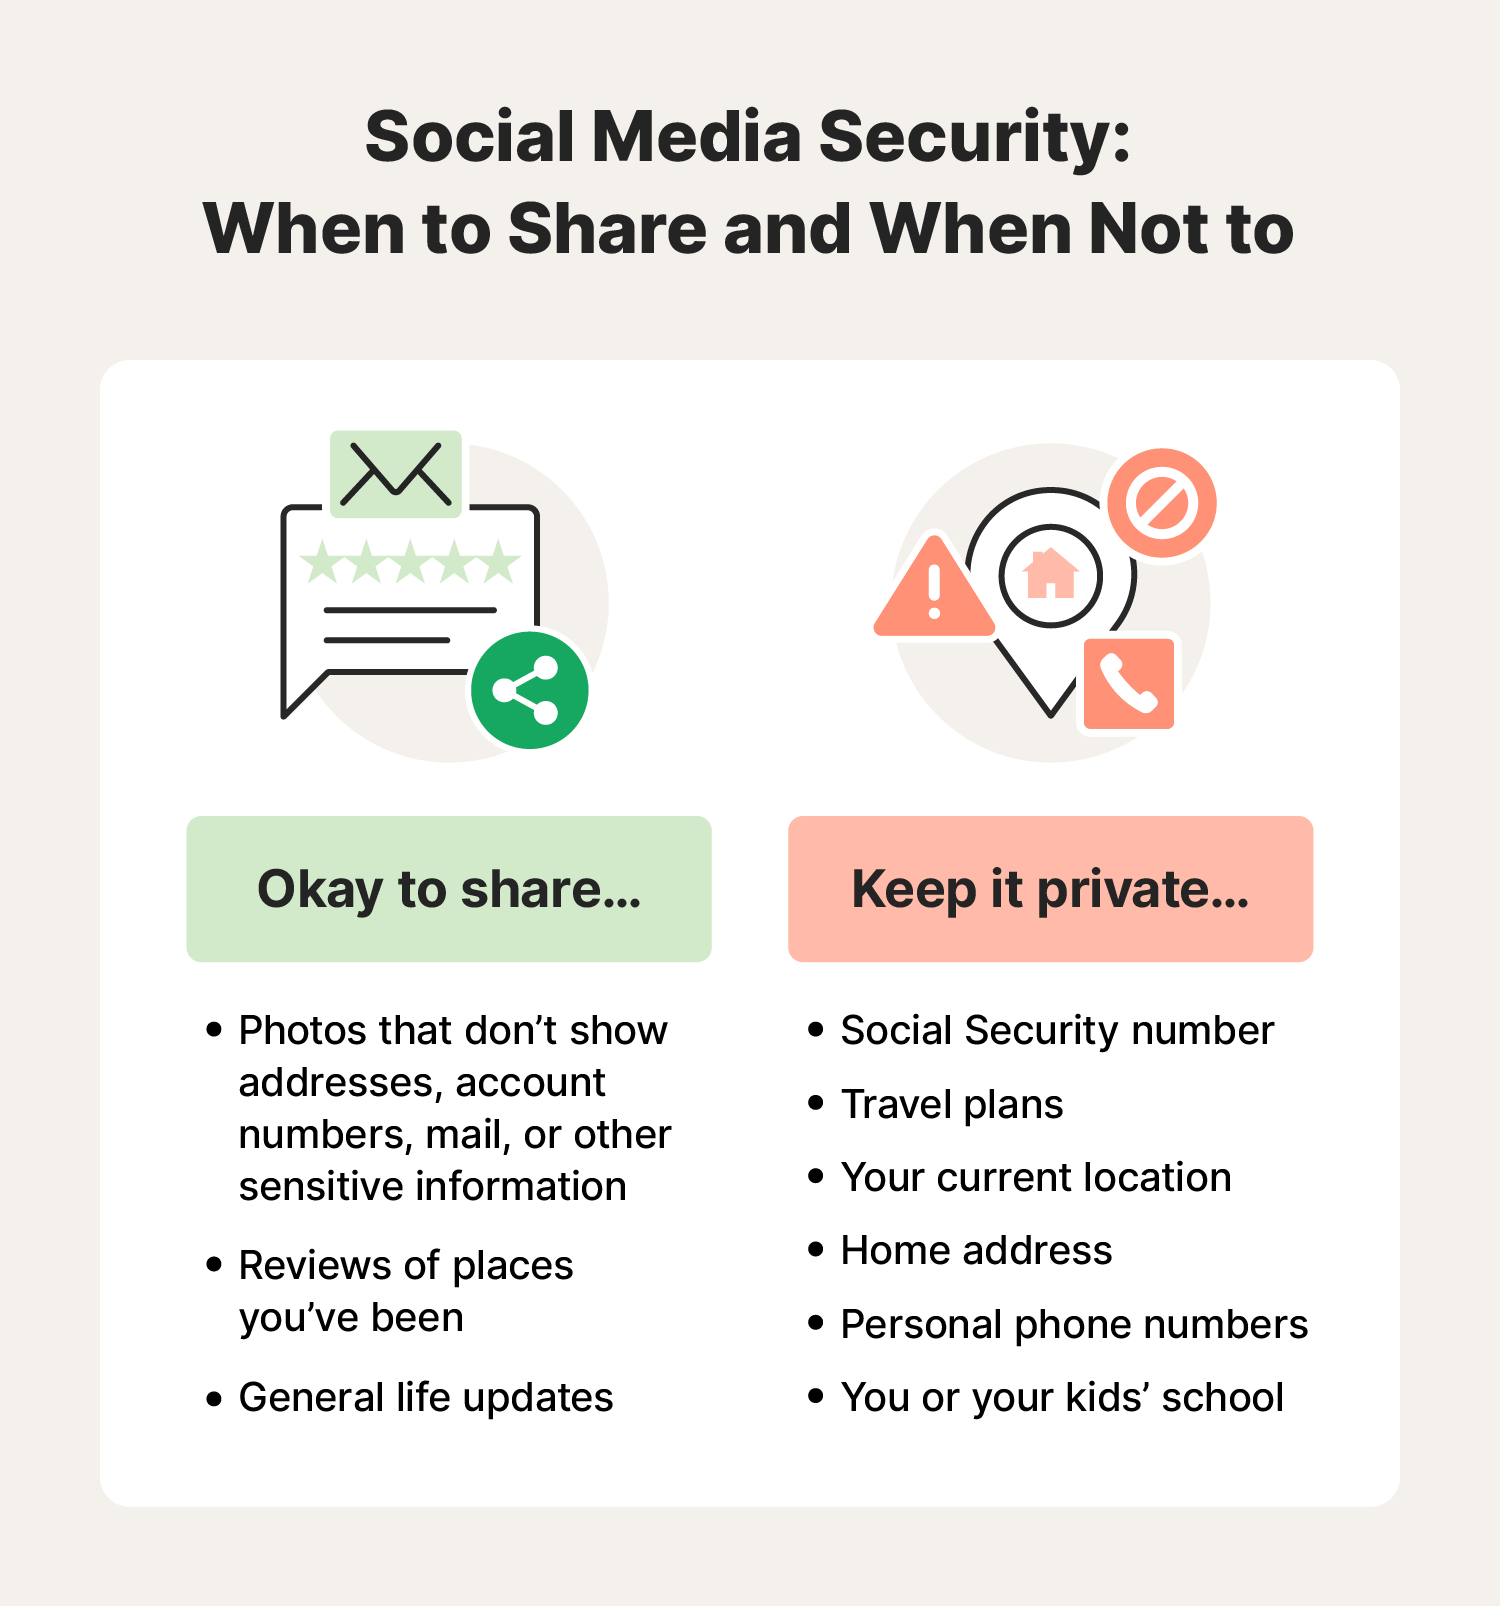
Technology and law are only as effective as the people operating them. Human error remains a significant vulnerability. Employees might inadvertently share a recording with sensitive background data or use unapproved conferencing tools. Therefore, cultivating a culture is paramount. This involves regular, engaging training that goes beyond check-the-box compliance. Training should simulate real-world scenarios, like identifying social engineering attempts during a video call. Empowering individuals with tools to audit and manage their digital footprint, including video shared on social media, can further extend protection. The human element is the last line of defense.

Practical Steps for Individuals and Enterprises
For individuals, practical steps include reviewing privacy settings on all devices and platforms that capture video, being mindful of backgrounds in live or recorded content, and understanding the permissions granted to video-centric applications. For enterprises, it requires a lifecycle approach: from initial collection with clear purpose limitation, through secure processing and storage, to eventual deletion. Implementing a Data Protection Impact Assessment (DPIA) for any new video processing activity is a best practice. The following list summarizes key actions.
- Conduct a Data Inventory: Know what video data you collect, where it is stored, and who has access.
- Implement Privacy by Design: Integrate data protection from the outset of any system or process involving video.
- Regularly Update and Patch: Keep all software, especially for IoT devices, updated to mitigate known vulnerabilities.
- Have a Breach Response Plan: Specifically address scenarios involving video data compromise, including notification procedures.
Looking Ahead: The Future of Video Privacy
The trajectory points toward more sophisticated threats and more nuanced protections. The integration of video data with other data streams will create richer profiles, increasing the stakes of any breach. Conversely, privacy-enhancing technologies like federated learning and homomorphic encryption may allow for valuable data analysis without exposing the raw video content itself. The concept of "privacy by design" will evolve from a best practice to a core engineering requirement. Ultimately, safeguarding video private info is not a static goal but a continuous process of adaptation, requiring vigilance from individuals, responsibility from corporations, and thoughtful governance from regulators. The balance between innovation and privacy will define the next chapter of our digital lives.