Web development relies heavily on structured HTML, and one of its most powerful features is the ability to embed diverse content directly within an HTML document. From interactive videos and dynamic charts to live data feeds and third-party applications, the modern web is built on elements that extend far beyond static text. Understanding how to correctly embed these components is essential for rich, interactive web experiences.
Common Elements Designed for HTML Embedding
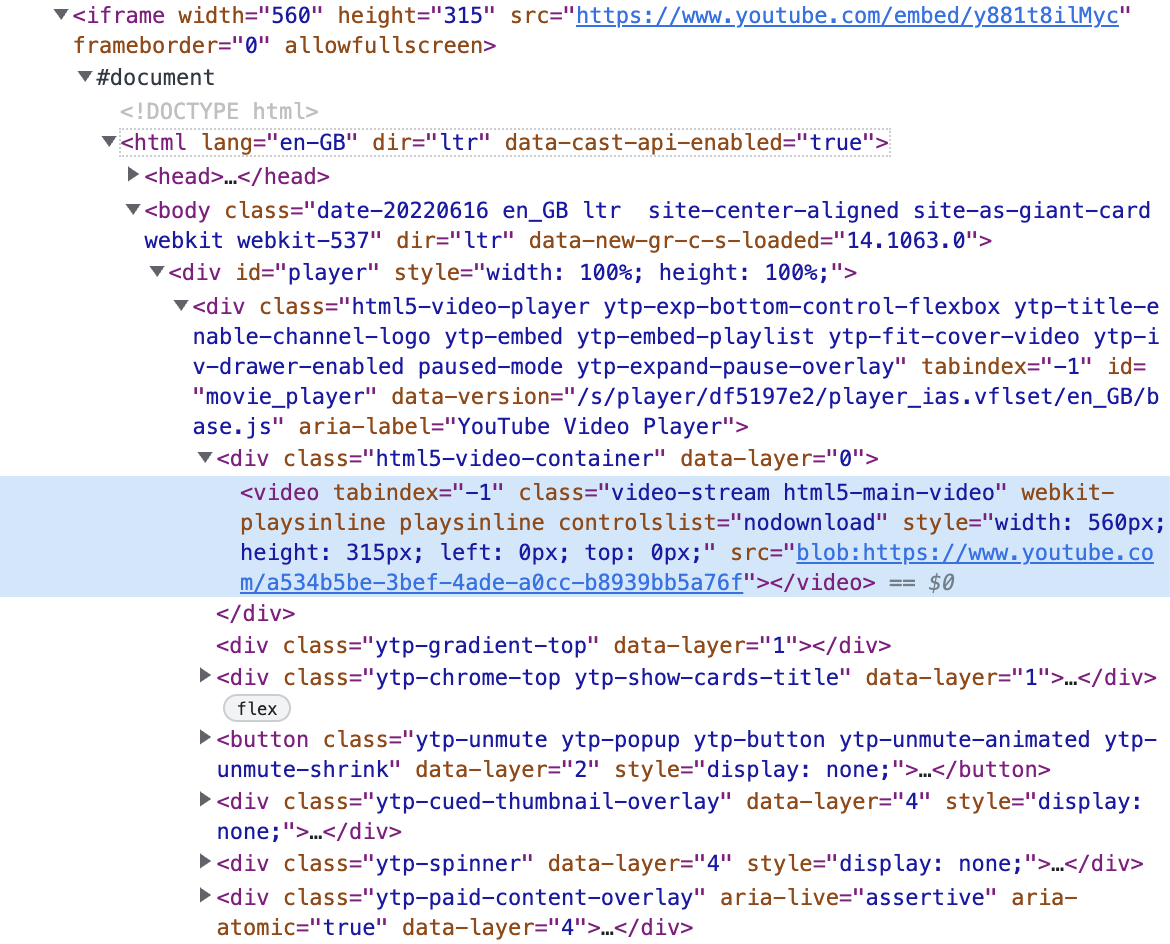
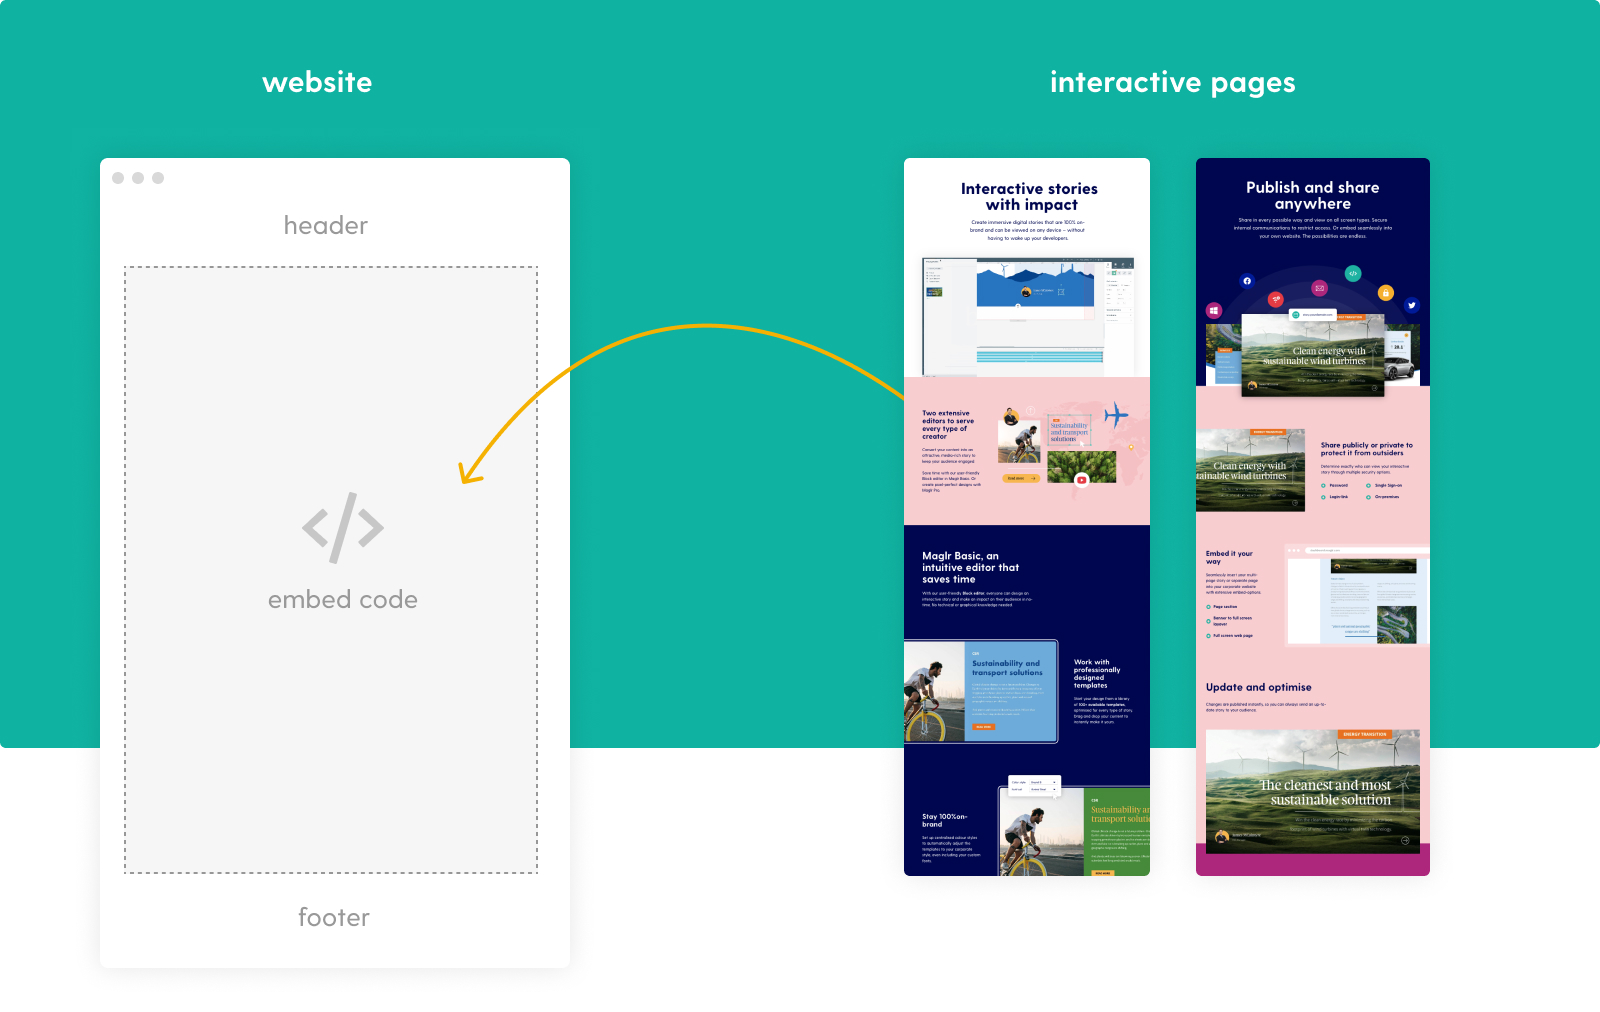
Several core technologies are specifically designed to be embedded within an HTML page, each serving a unique purpose. The <iframe> tag remains the cornerstone for embedding external web pages, maps, and video players. It acts as a window into another document, allowing for isolated content with its own scrollbars and separate CSS styling.
The Versatile <iframe>
An <iframe> (inline frame) is used to embed another HTML document within the current page. It is the standard method for embedding content from external sources like YouTube videos, Google Maps, or third-party widgets. Key attributes like src, width, height, and sandbox control its source, dimensions, and security restrictions.
Multimedia: <video> and <audio>
Native HTML5 multimedia elements provide direct embedding without plugins. The <video> and <audio> tags allow for embedding media files with built-in controls. They support multiple source formats (MP4, WebM, Ogg, MP3) and can be styled and controlled via JavaScript for custom players.
Interactive & Data-Driven Content
For more complex interactions, specific elements enable embedding dynamic content. The <canvas> element provides a drawing surface for JavaScript to render graphics, animations, and data visualizations. The <svg> tag allows for vector-based graphics that scale perfectly. Both are fundamental for modern interactive applications.
| Element | Primary Use |
|---|---|
| <iframe> | Embedding external web pages or documents |
| <video> / <audio> | Native multimedia playback |
| <canvas> / <svg> | Dynamic graphics and data visualization |
Embedding Scripts and Data
The <script> tag is designed to embed or reference executable code, typically JavaScript, directly within HTML. This enables dynamic behavior, form validation, and API calls. Similarly, the <object> and <embed> tags provide legacy methods for embedding external resources like PDFs or Flash content, though their use has declined with HTML5.
Best Practices for Secure Embedding
When embedding external content, security is paramount. Always use the sandbox attribute in <iframe> to restrict embedded content capabilities. For scripts, implement Content Security Policy (CSP) headers to prevent cross-site scripting (XSS). Validate and sanitize any user-generated content before embedding it to maintain site integrity.
Embedding content correctly enhances user experience while maintaining performance and security. By leveraging the appropriate HTML elements—from <iframe> for external pages to <canvas> for custom graphics—developers can create rich, interactive web applications. Mastering these embedded elements is key to modern web development.