"Mastering Direct Access with Wireshark: A Comprehensive Guide"
Network professionals, security analysts, and IT troubleshooters live by one thing: data. Specifically, the data traveling through their networks. While many tools offer a glimpse into this traffic, Wireshark stands out for its depth. However, running it in its default mode isn’t always efficient. This is where Wireshark Direct Access becomes critical, offering a dedicated pathway to system-level networking data for superior performance.
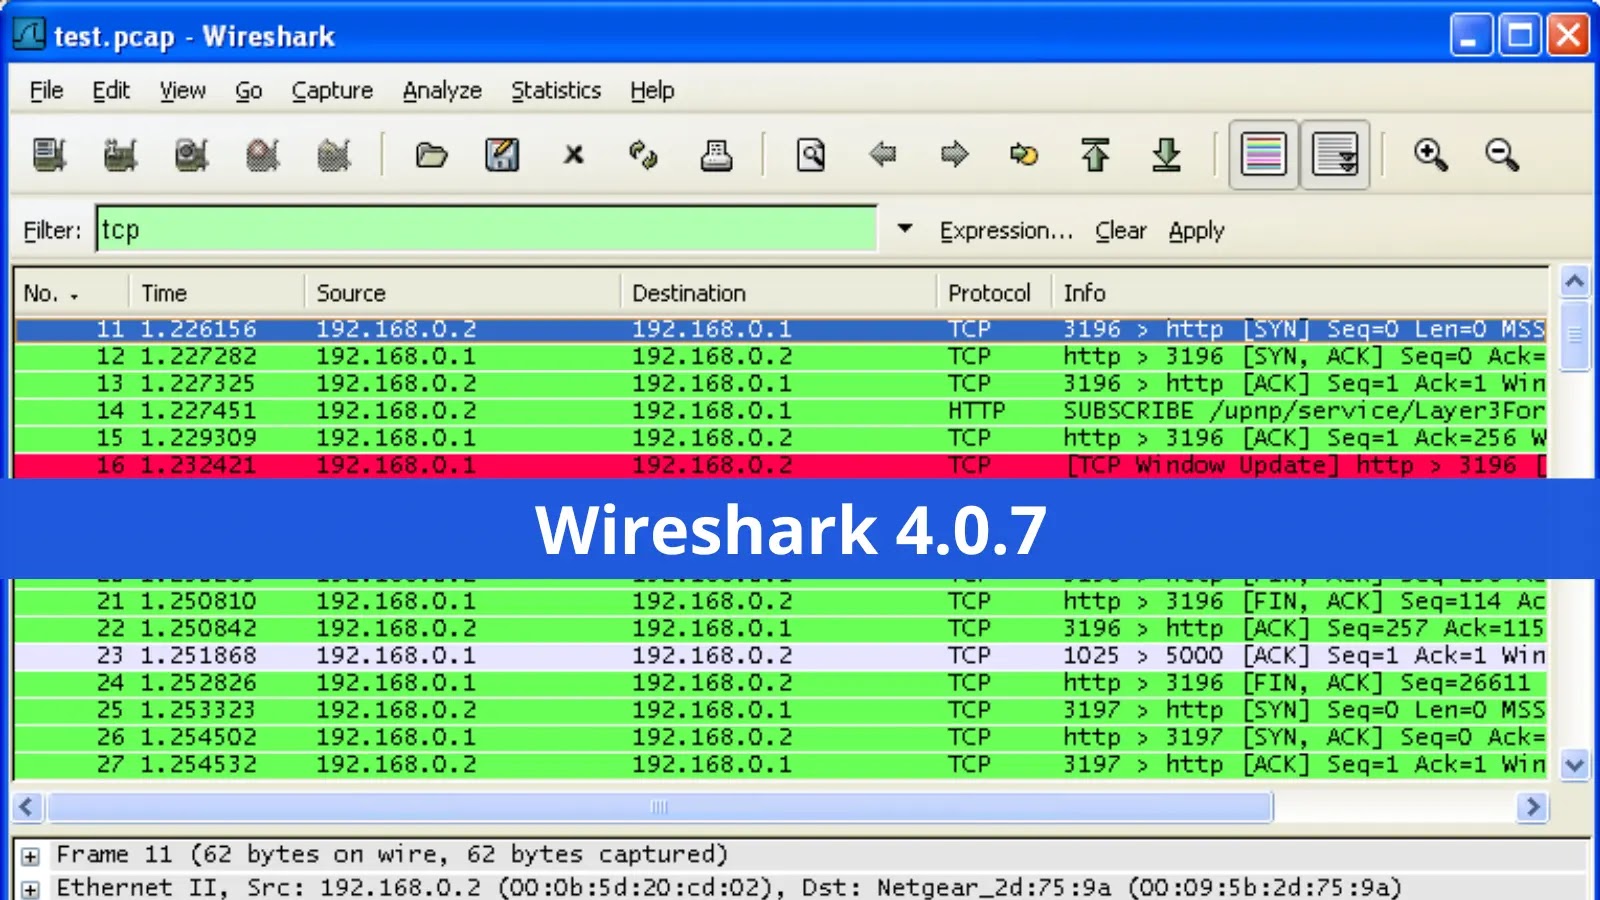
What is Wireshark Direct Access?

Wireshark Direct Access refers to bypassing the standard operating system’s network stack drivers. Traditionally, Wireshark uses a library like Npcap or Libpcap to capture packets via standard OS APIs. While effective for general analysis, this approach subjects the captured data to OS-level filtering and processing, which can lead to packet loss or performance bottlenecks during high-traffic scenarios. Direct Access, often leveraging the AirPcap interface or raw device access, creates a high-performance bridge between the wireless or wired hardware and the Wireshark application.
This technique is most commonly associated with wireless analysis using legacy AirPcap devices, but the principles apply to advanced capture setups. It eliminates unnecessary overhead by providing raw packet data directly to the dissection engine, allowing Wireshark to operate at lower network layers without interference.

Why Direct Access Matters for Analysis
High-speed networks demand speed. In industries where millisecond-latency matters, or when monitoring a 10 Gigabit Ethernet link, any layer of abstraction can be a liability. Using Wireshark in Direct Access mode allows the capture driver to manage memory and reception more efficiently, ensuring that even heavy throughput doesn’t overwhelm the CPU or result in dropped frames.
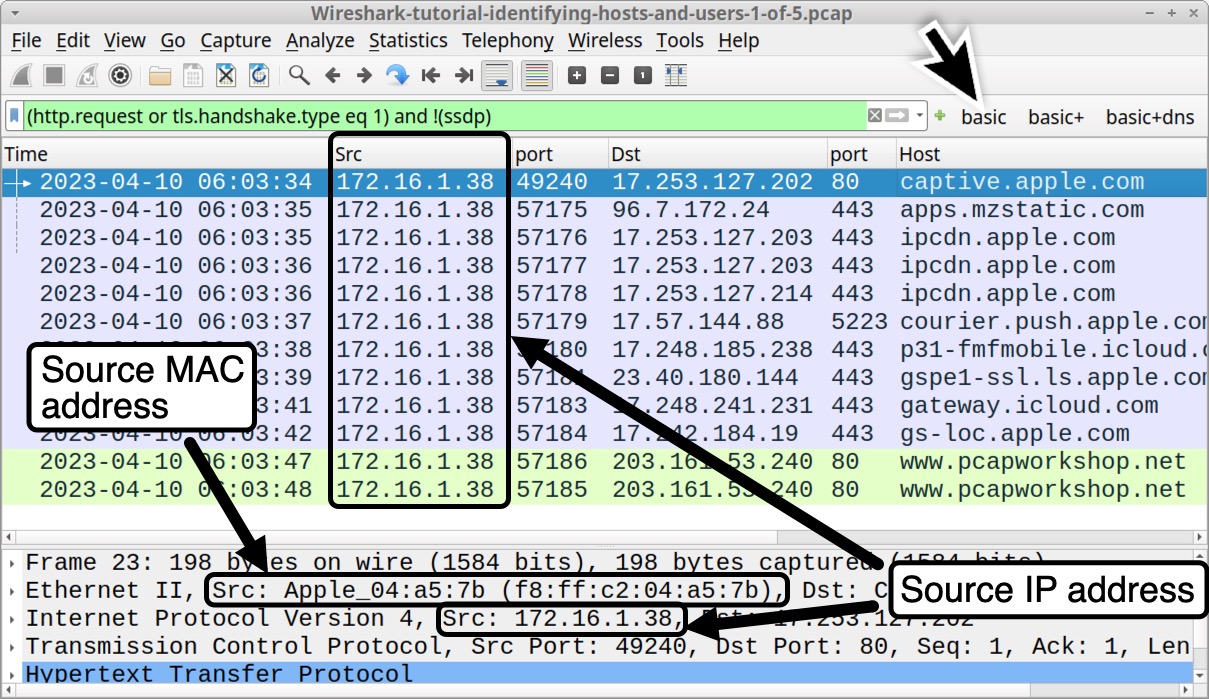
Beyond throughput, accuracy is often compromised in standard modes. OS-level capture libraries might strip 802.11 headers from wireless frames or restructure loopback traffic, making a direct analysis of Layer 2 protocols difficult. Direct Access preserves the integrity of captured frames, analyst’s tool of choice for malformation, handshakes, and wireless hop-by-hop forwarding.
Setting Up Wireshark Direct Access
To configure Direct Access, hardware compatibility is the primary constraint. Most commonly, AirPcap NX devices utilize a dedicated AirPcap API. You must install the AirPcap driver, which bypasses Windows limitations to allow direct reading of raw PHY/MAC data.

- Download and install the original AirPcap device drivers.
- Next, run Wireshark. On the toolbar, select the AirPcap interface rather than a standard “Wi-Fi” capture source at the device list.
- Once attached to the AirPcap source, you will see options for Wireshark Direct Access mode for that device.
For wired networks, Direct Access concepts mirror high-performance capture cards (like specialized FPGA-based NICs) or standards like DPDK. These bypass the Windows Kernel to move packet buffers from the NIC directly to the user-space application.
Direct Access Wireshark vs. Npcap Standard Captures
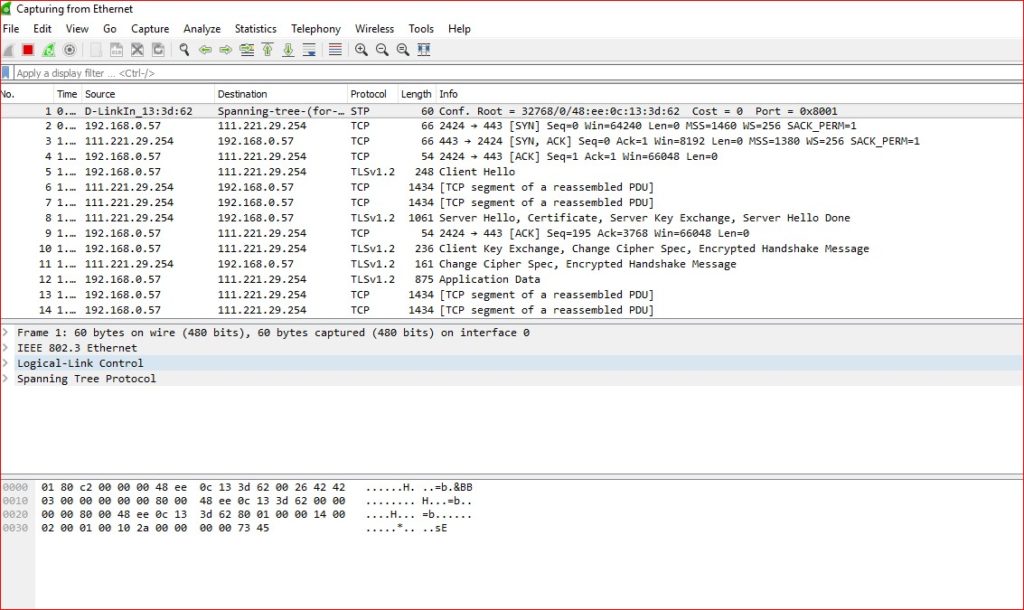
Wireshark users frequently rely on Npcap, which is the library that replaced WinPcap. Npcap is excellent for general purposes but acts as a filter on top of the network traffic after the OS has processed it. One crucial difference is in the OS’s default behavior regarding traffic that is directed to other machines.
Standard Npcap captures traffic arriving at the OS network interface controller (NIC). In contrast, optimized Direct Access approaches monitor the physical layer, ensuring that malformed packets—which the NIC’s hardware might typically discard—are actually captured and analyzed by Wireshark. This makes Direct Access invaluable for identifying driver-level issues or physical medium errors.



Is Direct Access Right for You?
Direct Access isn’t for everyone. If standard Wireshark traces using Npcap or Libpcap provide the data you need for daily protocol analysis, switching to Direct Access adds hardware cost without daily analytical necessity. Its value appears in edge cases and high-performance environments: wireless penetration testing, forensic investigation of malformed frames, or stress-testing network devices.
For most corporate environments, a robust installation of Wireshark paired with Npcap will provide 95% of necessary insights. However, understanding where Direct Access fits in the toolkit empowers the analyst to choose the right tool for specific capture-intensive scenarios. Consider it the preferred solution for specialized wireless troubleshooting using AirPcap hardware.
| Capture Mode | Overhead | Frame Integrity | Performance |
|---|---|---|---|
| OS Stack / Npcap | Higher | Modified by OS | Moderate |
| Wireshark Direct Access | Minimal | Original/Raw | Superior |