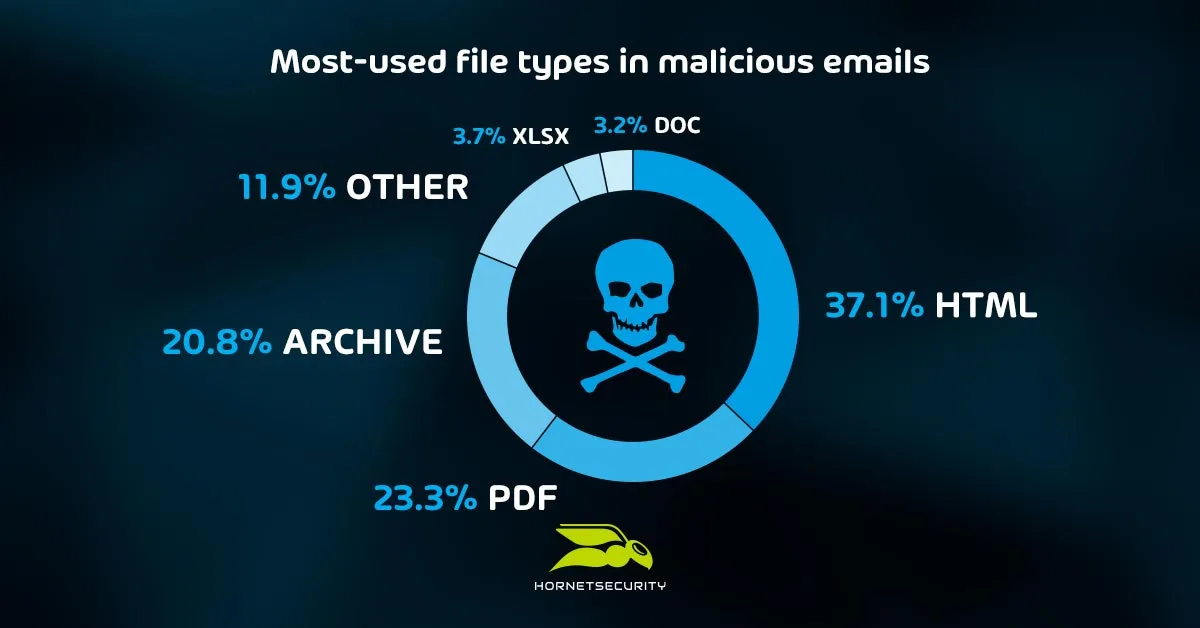
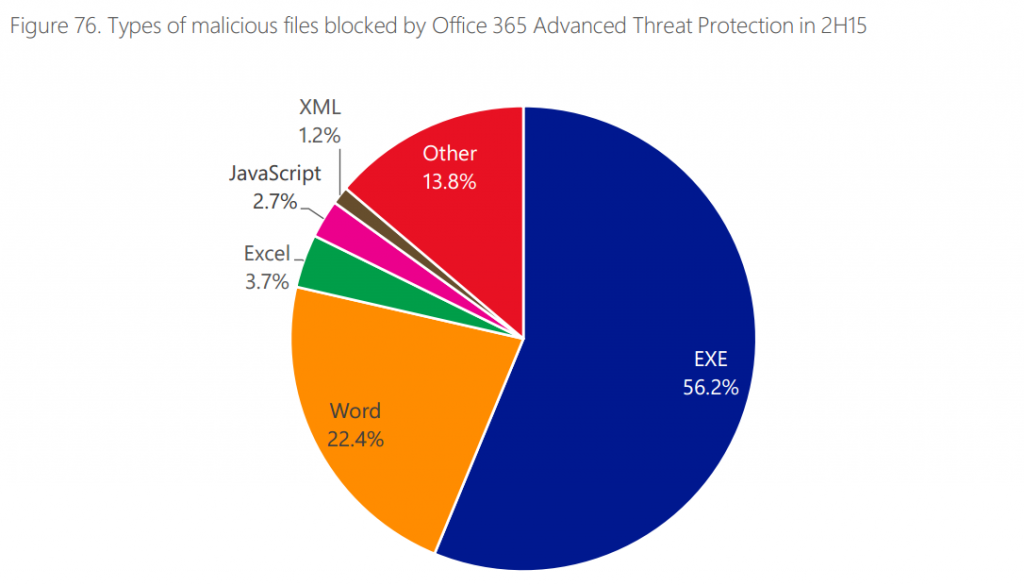
When it comes to cybersecurity, understanding which file types pose the greatest threat is essential for both individuals and organizations. While virtually any file can be weaponized, certain extensions are far more likely to carry malicious code due to their ability to execute commands, run scripts, or exploit software vulnerabilities. Knowing these high-risk formats helps users make smarter decisions about what they download, open, or share.
Why Some File Extensions Are More Dangerous Than Others
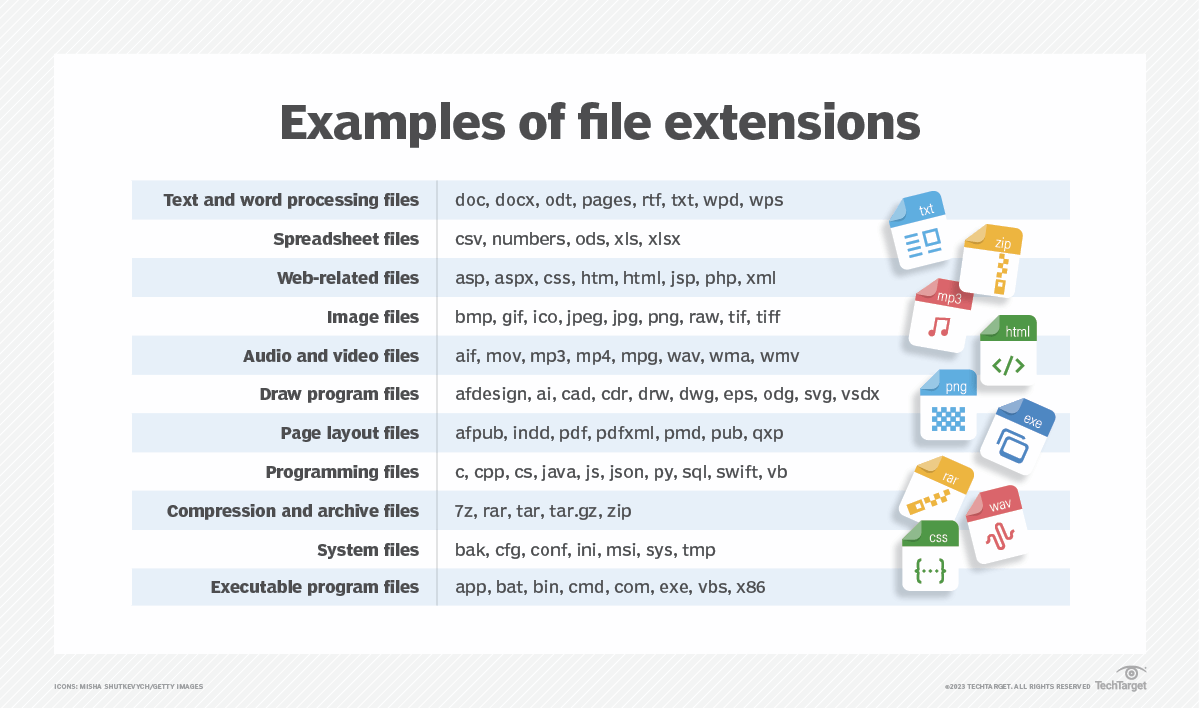
Not all files are created equal in the eyes of an attacker. The real danger lies in files that can execute code—whether through direct execution, embedded macros, or exploitation of software flaws. Attackers often disguise harmful payloads as everyday documents or media files, banking on user trust and lack of awareness. This is why file extensions matter: they signal what the file is supposed to do, and malicious actors exploit that expectation.
Top File Extensions Most Likely to Contain Malicious Code
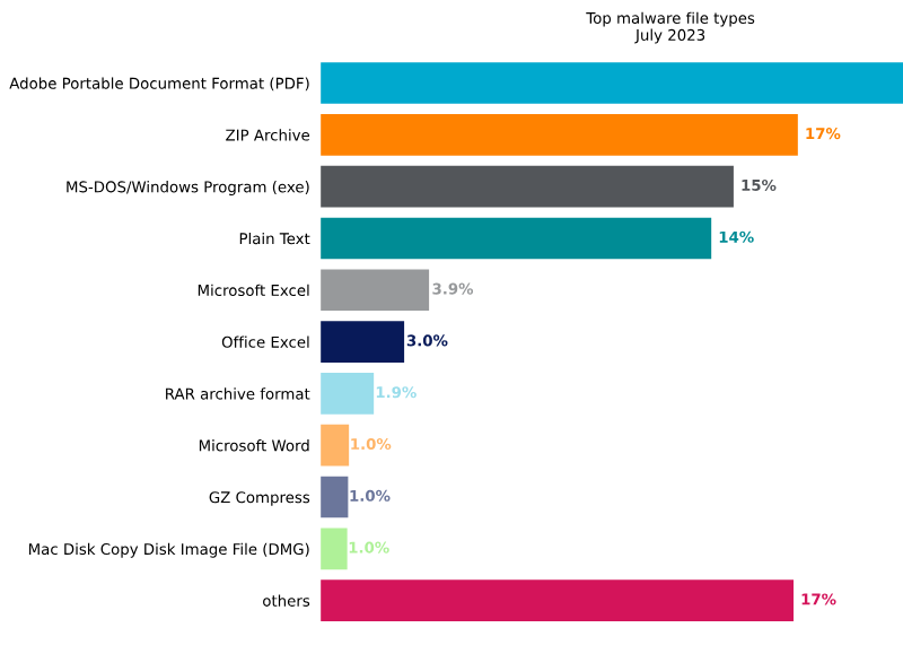
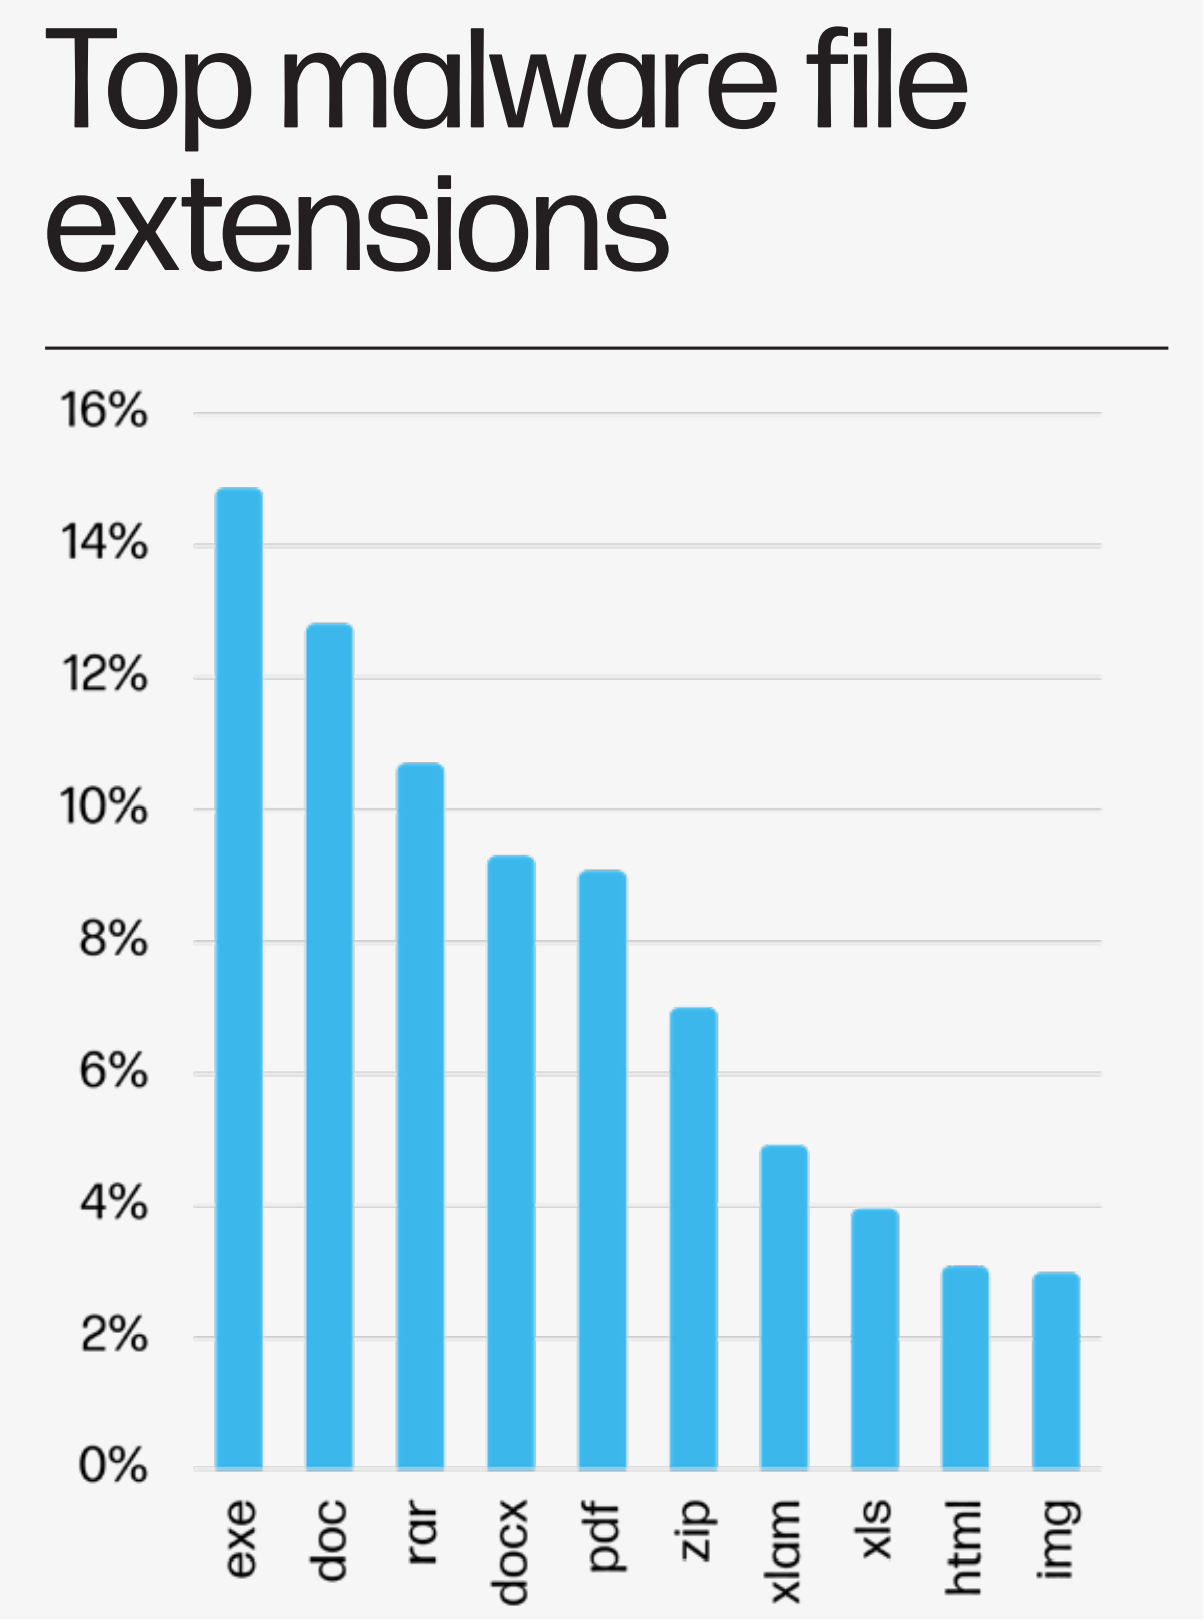
Below is a breakdown of the most commonly abused file types in cyberattacks, along with why they’re favored by threat actors:
| File Extension | Common Use | Why It’s Risky |
|---|---|---|
| .exe | Windows executable | Directly runs code; often disguised as legitimate software |
| .bat / .cmd | Batch scripts | Executes system commands silently |
| .js / .vbs | JavaScript / VBScript | Can run malicious scripts via Windows Script Host |
| .doc / .xls (with macros) | Office documents | Macros can auto-execute harmful code |
| Portable Document Format | Can embed JavaScript or exploit reader vulnerabilities | |
| .scr | Screensaver files | Treated as executables; often used in phishing |
| .dll | Dynamic Link Library | Loaded by other programs; can be hijacked or replaced |
How Attackers Exploit These File Types
Cybercriminals use social engineering to trick users into opening dangerous files. For example, a file named “invoice.pdf.exe” may appear as “invoice.pdf” if Windows hides known extensions—a default setting on many systems. Similarly, macro-laden Word documents prompt users to “Enable Content,” which triggers hidden scripts. Even seemingly harmless PDFs can contain embedded JavaScript that redirects to phishing sites or downloads malware silently.
Less Obvious Threats: Double Extensions and Archive Files
Attackers also rely on double extensions (like “report.doc.js”) or compressed archives (.zip, .rar, .7z) to bypass email filters and user suspicion. Once extracted, these archives may contain executables or scripts. While .zip files themselves aren’t executable, they’re frequently used as delivery mechanisms for more dangerous payloads hidden inside.
Best Practices to Stay Protected
Reducing risk starts with vigilance and configuration:

- Always show file extensions in Windows Explorer to spot disguised executables.
- Never enable macros in Office files from untrusted sources.
- Use updated antivirus software that scans archives and script files.
- Avoid downloading files from unknown senders, even if they appear to be common formats like .pdf or .docx.
- Keep your operating system and applications patched to close known vulnerabilities.
Final Thoughts on File Safety
No file extension is inherently evil—but some provide far more opportunity for abuse than others. The key is context: who sent it, why you received it, and whether it behaves unexpectedly. By staying informed about high-risk file types and adopting cautious habits, you significantly reduce your exposure to malware. In cybersecurity, awareness isn’t just power—it’s protection.