Understanding WinDumps: A Comprehensive Guide
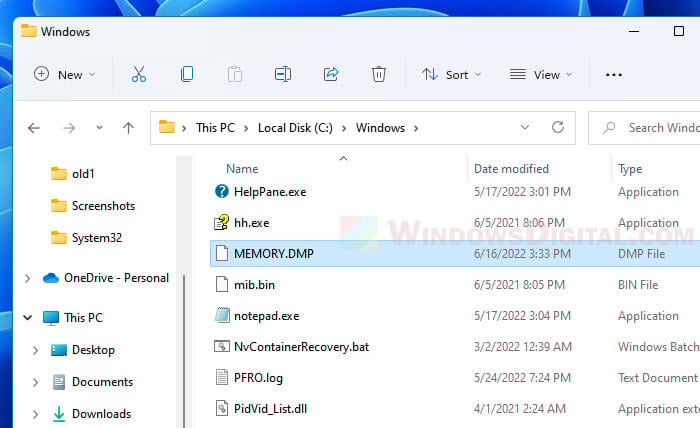
Have you ever encountered an unexpected system crash on your Windows machine, only to find a mysterious file named 'memory.dmp' or 'winmem.dmp' in your system directory? These files are known as WinDumps, and they play a crucial role in Windows' error reporting and debugging process. Let's delve into the world of WinDumps, understanding what they are, their purpose, and how they can help you troubleshoot Windows issues.
What are WinDumps?
WinDumps, short for Windows Dump Files, are binary files created by the Windows operating system when a system crash or bluescreen of death (BSOD) occurs. They contain a snapshot of the system's memory at the time of the crash, including the state of all processes, threads, and kernel data structures. These files are essential for debugging and troubleshooting Windows issues, as they provide valuable insights into what might have caused the system to crash.
Types of WinDumps
Windows creates two types of dump files, each serving a different purpose:
- Complete Memory Dump (Full): This type of dump file captures the entire physical memory of the system. It's the most comprehensive but also the largest in size. It's typically used by advanced users and developers for in-depth debugging.
- Minidump (Small): Mini dumps are smaller in size as they only capture a portion of the system's memory. They are more manageable and are usually sufficient for most users to troubleshoot common issues. Windows creates mini dumps by default.
Where are WinDumps Located?
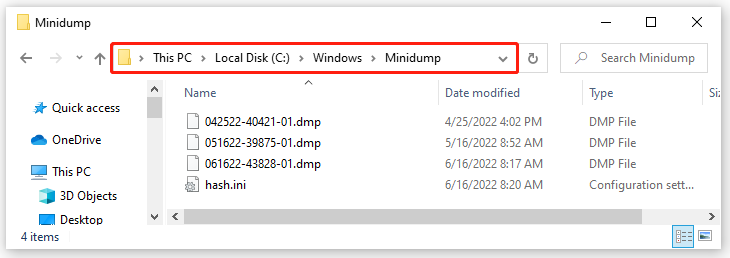
By default, Windows stores dump files in the following locations:
| Windows Version | Dump File Location |
|---|---|
| Windows 10, 8, and 7 | C:\Windows\Minidump |
| Windows Vista and older | C:\Windows\System32\Memory.dmp |
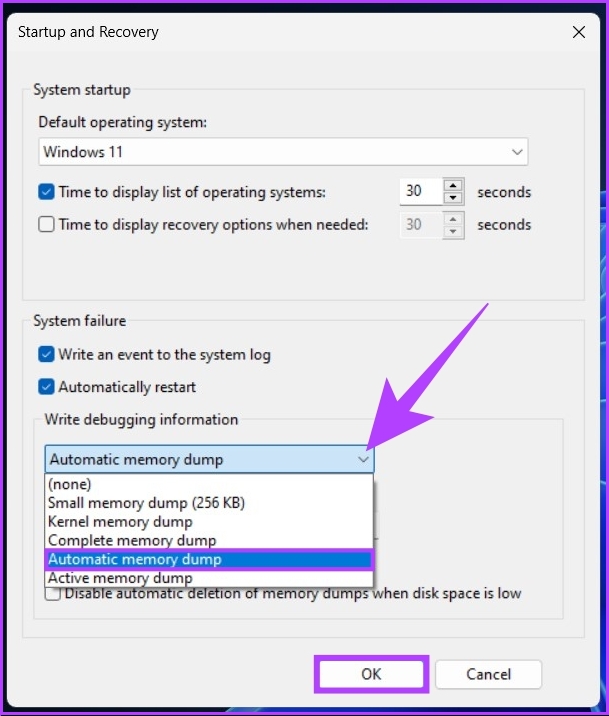
You can also change the dump file location or type using the sysdm.cpl tool in the System Properties or by modifying the registry.
How to Analyze WinDumps
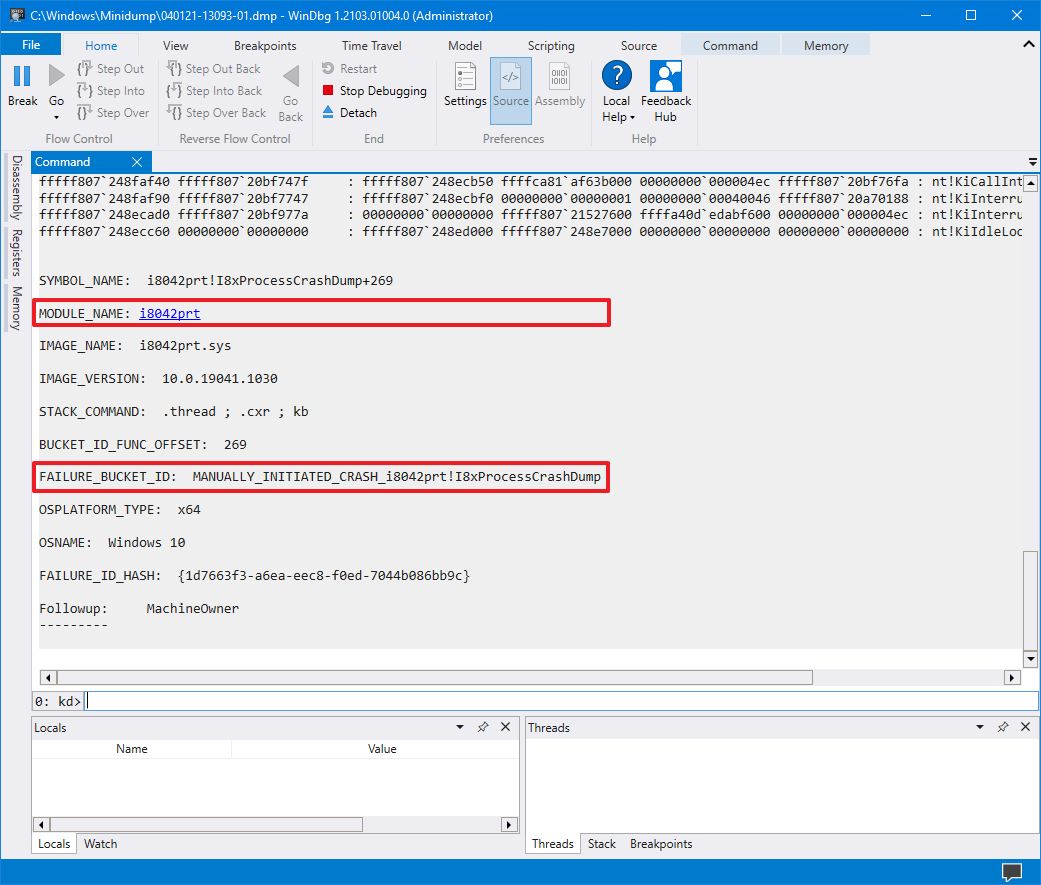
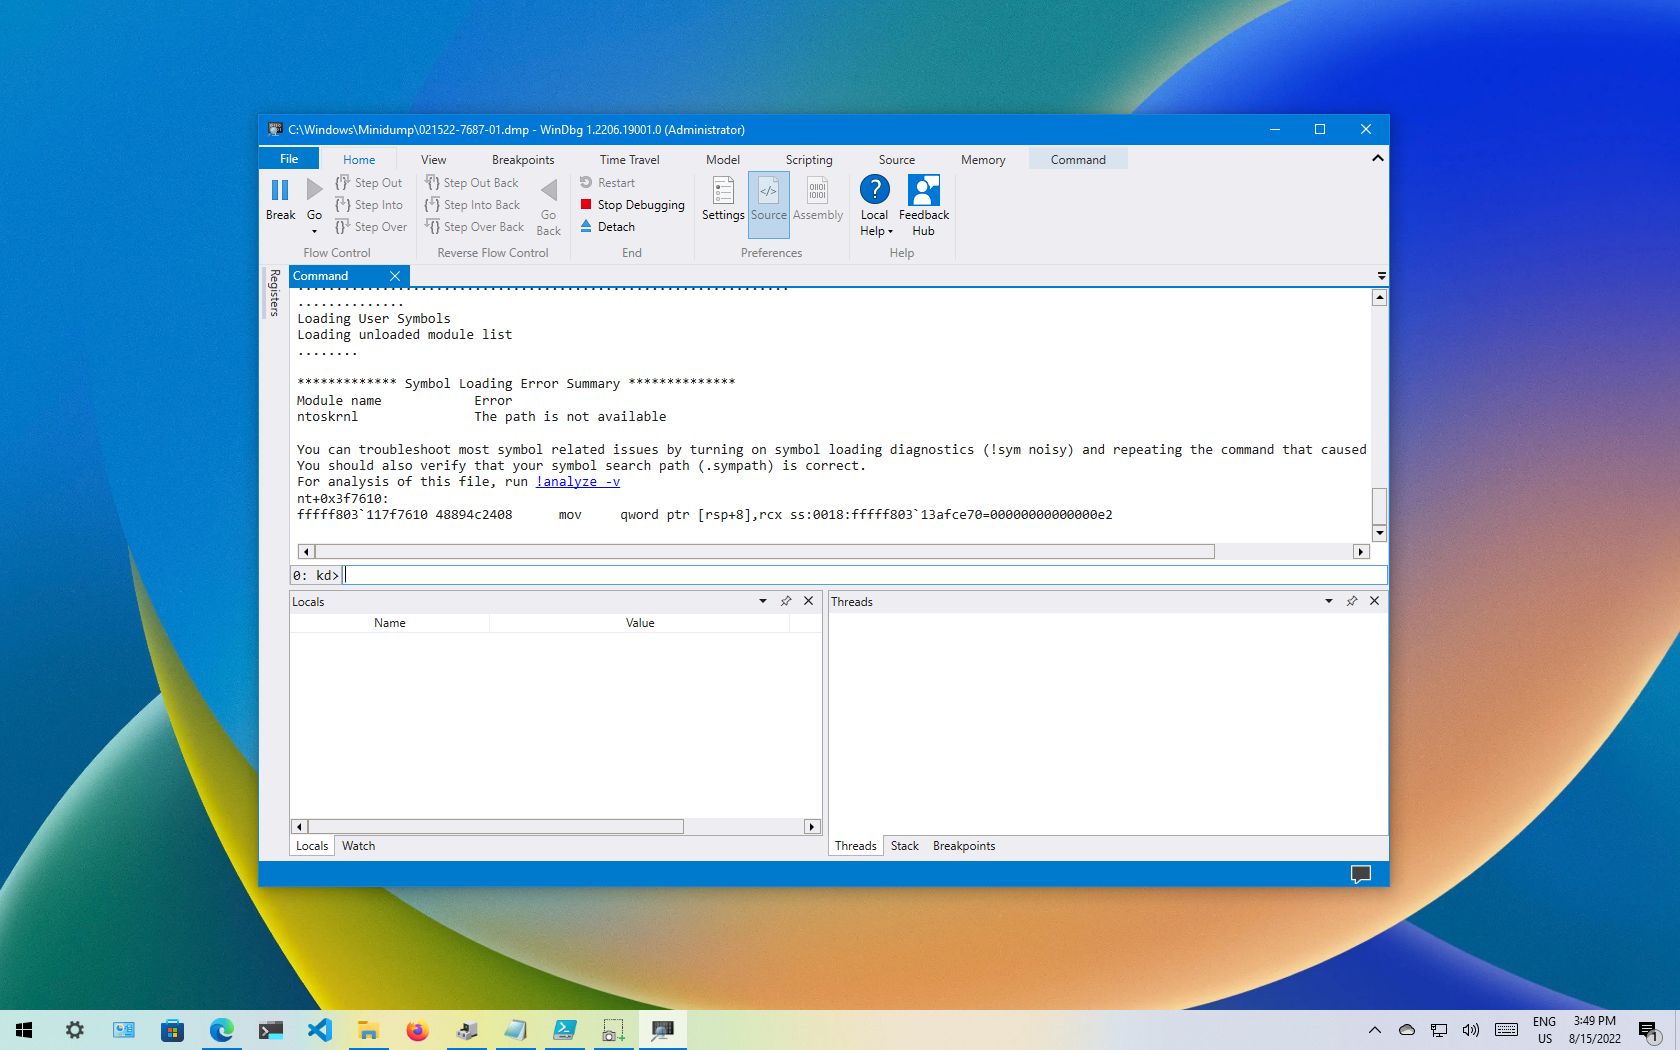
Analyzing WinDumps requires specialized tools, as they are binary files and cannot be opened with standard text editors. Microsoft provides the Windows Debugger (WinDbg), a powerful tool for analyzing dump files. It's available as part of the Windows SDK or the Windows Driver Kit. Here's a simple step-by-step guide to analyzing a dump file with WinDbg:
- Launch WinDbg as an administrator.
- Go to File > Open Crash Dump and select the dump file you want to analyze.
- WinDbg will load the dump file and display its contents. You can use various commands to analyze the dump file, such as
!analyze -vto display a verbose analysis of the crash.
Enabling and Configuring WinDumps
WinDumps are enabled by default in Windows, but you can configure their settings to suit your needs. To do this, follow these steps:
- Press Win + Pause/Break to open System Properties.
- Click on Advanced system settings.
- In the System Properties window, click on Settings... under the Startup and Recovery section.
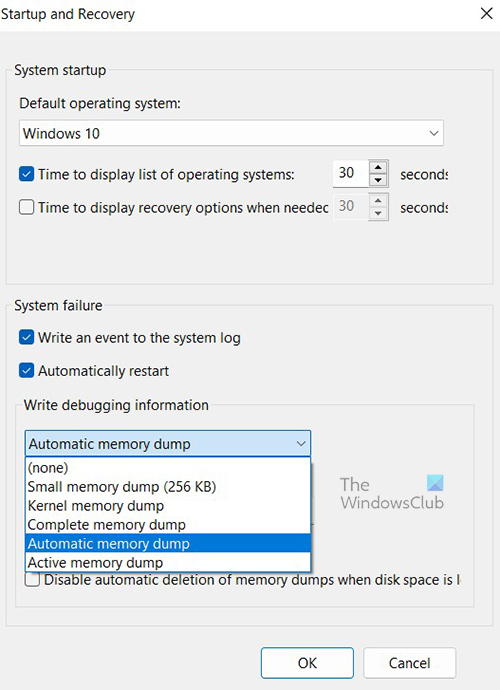
- In the Startup and Recovery window, under the System failure section, you can configure the following settings:
- Write debugging information: Choose the type of dump file you want to create.
- Dump file: Specify the location where you want to save the dump file.
Remember to click OK to save your changes.
Conclusion
WinDumps are a vital component of Windows' error reporting and debugging process. Understanding what they are, their types, locations, and how to analyze them can significantly enhance your troubleshooting capabilities. Whether you're a seasoned Windows user or a developer, having a solid grasp of WinDumps can help you diagnose and resolve issues more effectively. So the next time you encounter a mysterious dump file, you'll know exactly what to do with it.