"Track User Activity: Splunk User Login History"
Understanding user login activity is essential for maintaining security, ensuring compliance, and auditing access controls in any enterprise environment. Splunk transforms raw authentication logs into actionable insights, enabling security teams to track user behavior, detect anomalies, and respond swiftly to potential threats.
Why Monitoring User Login History Matters
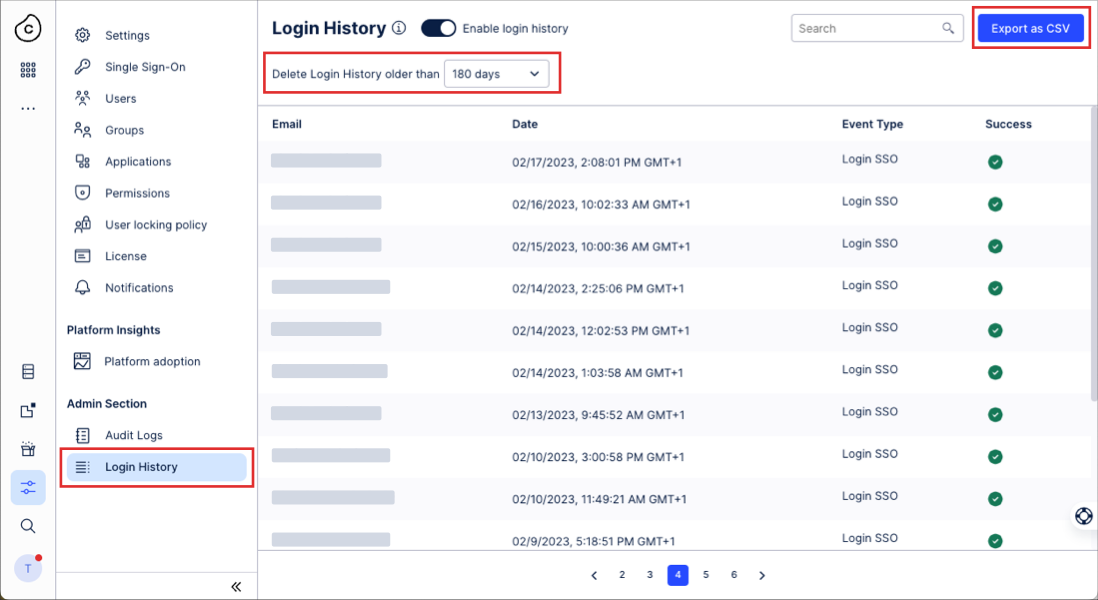
Every login event carries critical metadata: source IP address, timestamp, authentication method, success or failure status, and user identity. By collecting this data in Splunk, organizations can establish baselines for normal activity. Sudden login attempts from unusual geographic locations or repeated failed authentication attempts become immediately visible, allowing security teams to pivot before a minor anomaly escalates into a breach.
Collecting Login Data in Splunk

Splunk ingests login logs from virtually any source: Active Directory event logs, LDAP services, cloud identity providers like Okta or Azure AD, and custom application logs. Universal Forwarders or HTTP Event Collectors push this data into Splunk indexes, where it becomes searchable within minutes.
Common Data Sources

- Windows Security Event Logs (Event ID 4624 for successful logins, Event ID 4625 for failed attempts)
- Azure AD sign-in logs
- Cisco ASA or firewall authentication logs
- SSH or SFTP server logs
- SAML or OAuth token issuance events
Writing Effective SPL Queries
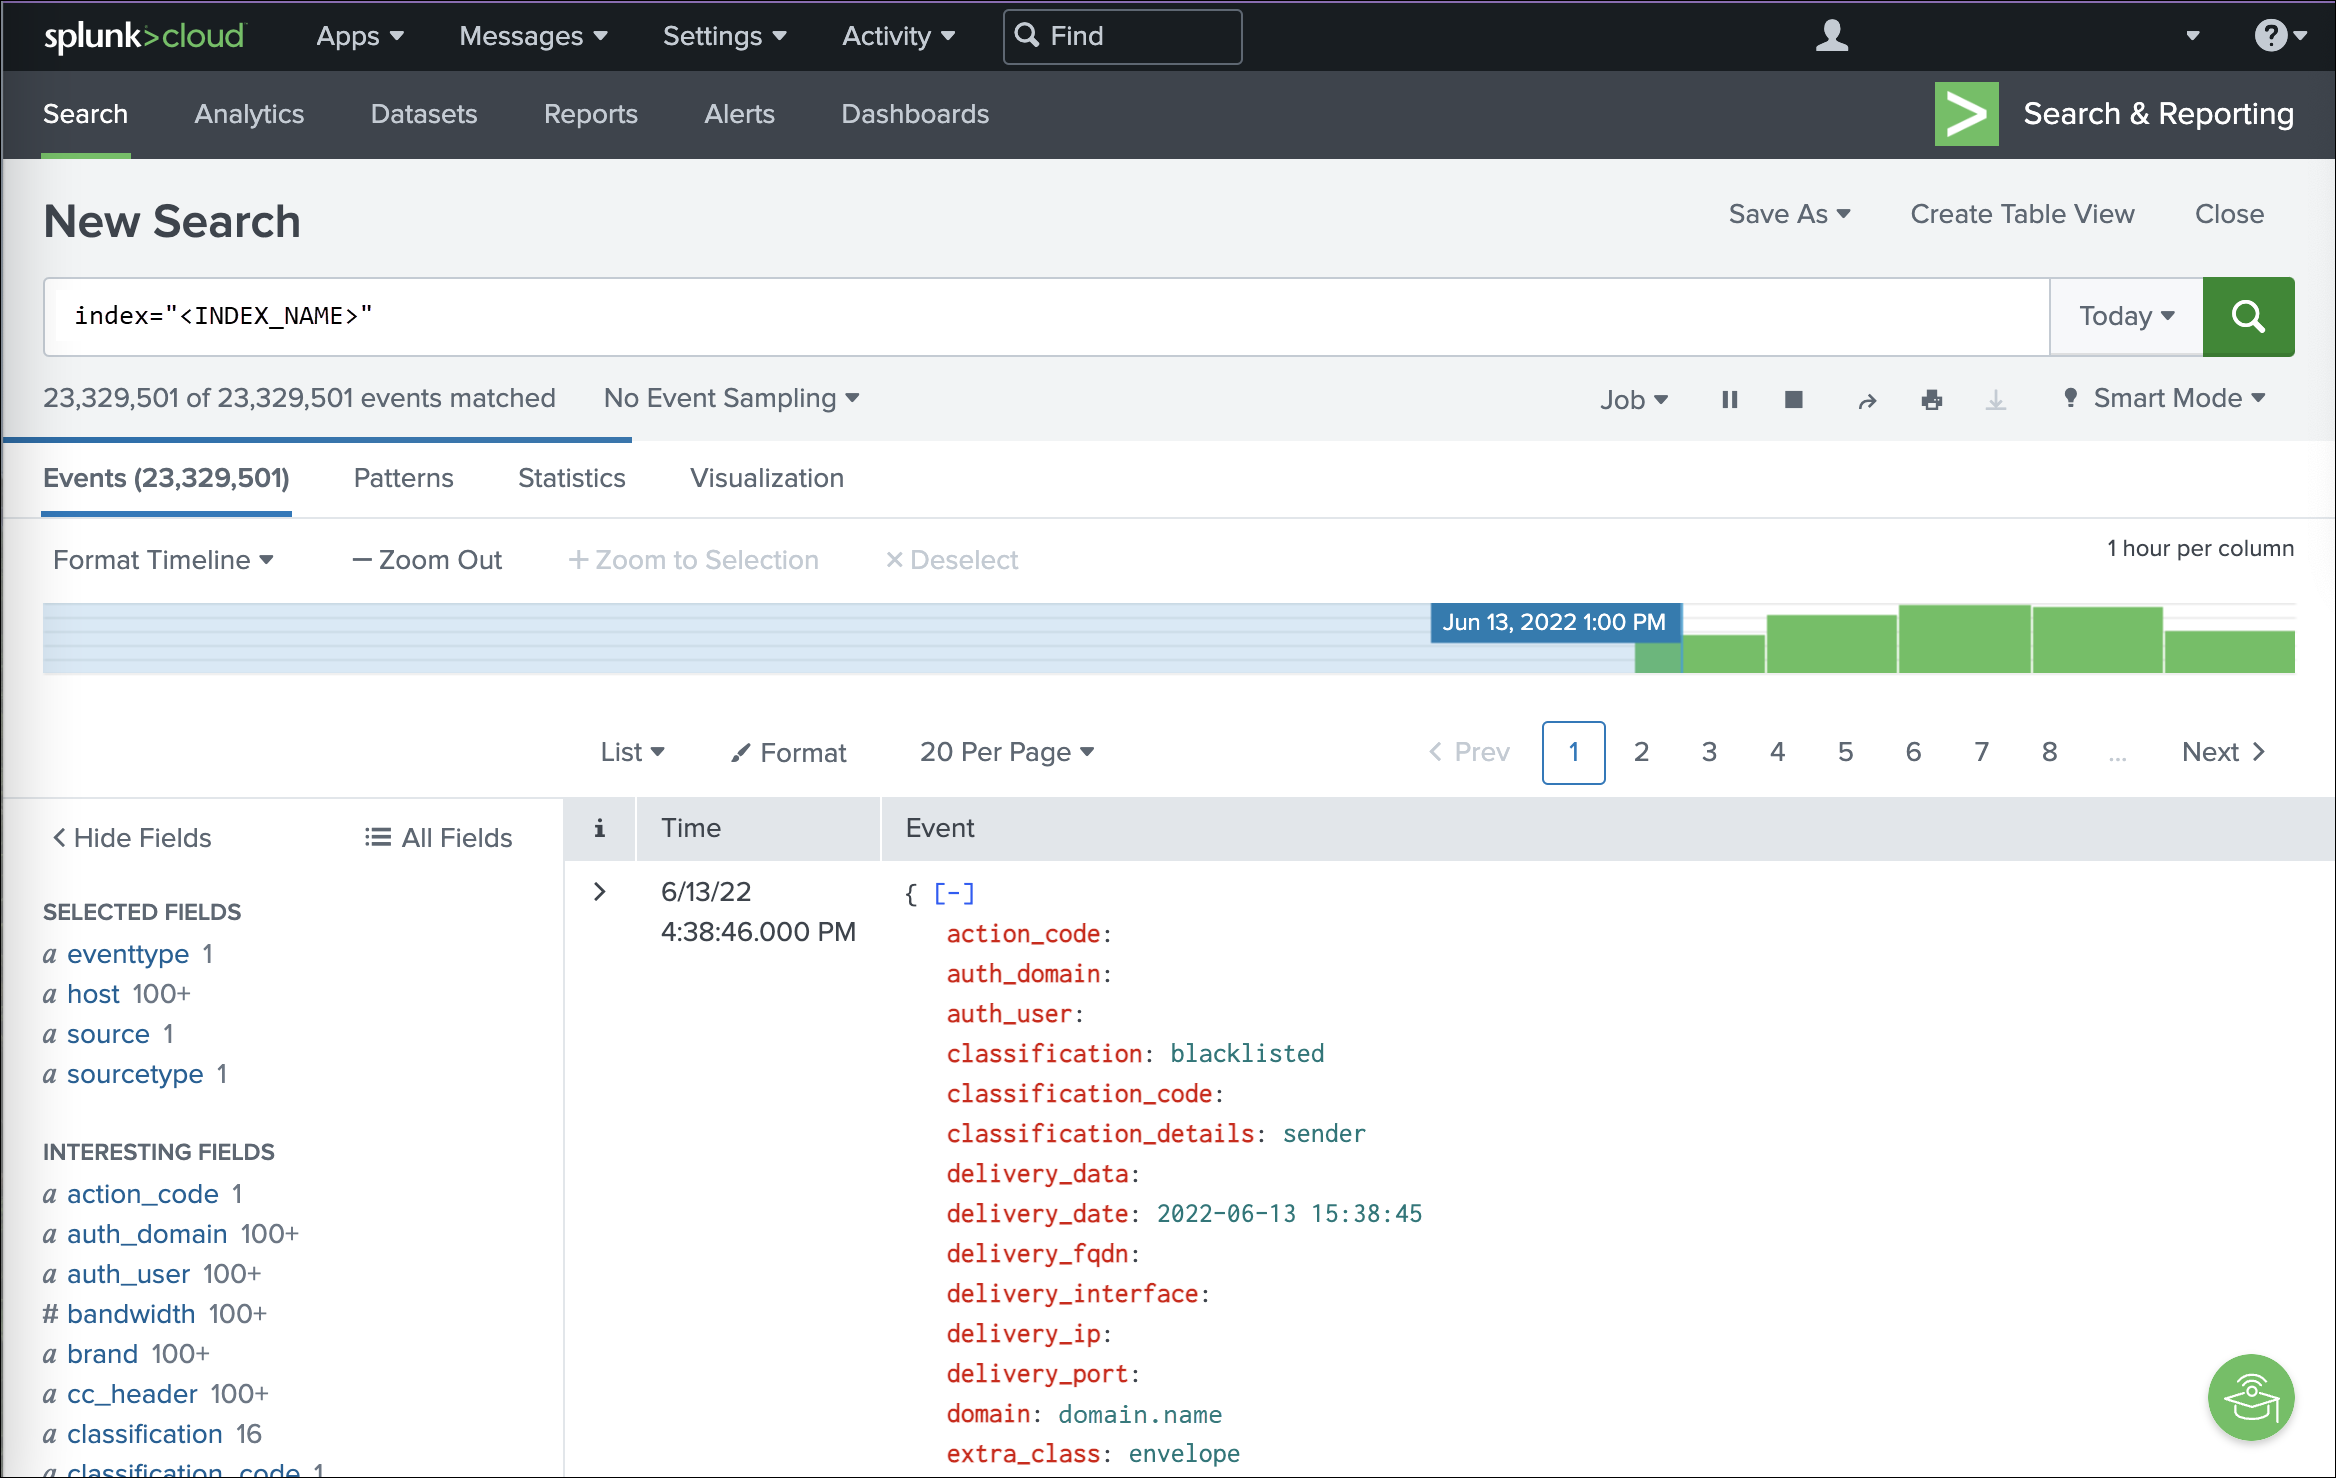
The Splunk Processing Language (SPL) is where raw data becomes insight. A straightforward query for all successful logins in the last 24 hours:
index=windows sourcetype="WinEventLog:Security" EventCode=4624 | table _time, user, src_ip, LogonType
This returns a clean table showing who logged in, from where, and what type of session was created. Filtering on LogonType values helps differentiate interactive logins (Type 2, 10) from service-level or network logins (Type 3), which often surface lateral movement attempts.
Detecting Suspicious Activity

Queries that flag unusual patterns are the backbone of proactive security. For instance:
- Failed logins exceeding five attempts from one source IP in ten minutes Successful logins outside business hours for privileged accounts
- Concurrent sessions from geographically distant locations for the same user




Visualizing Login Trends
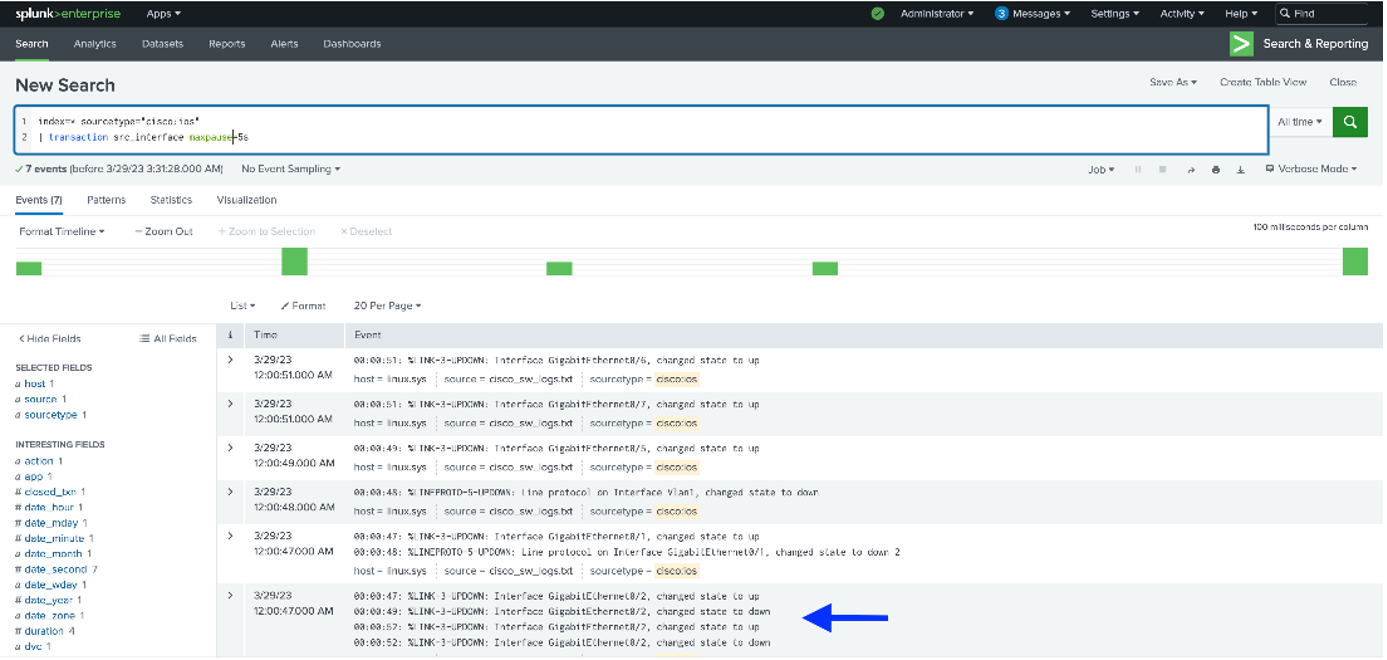
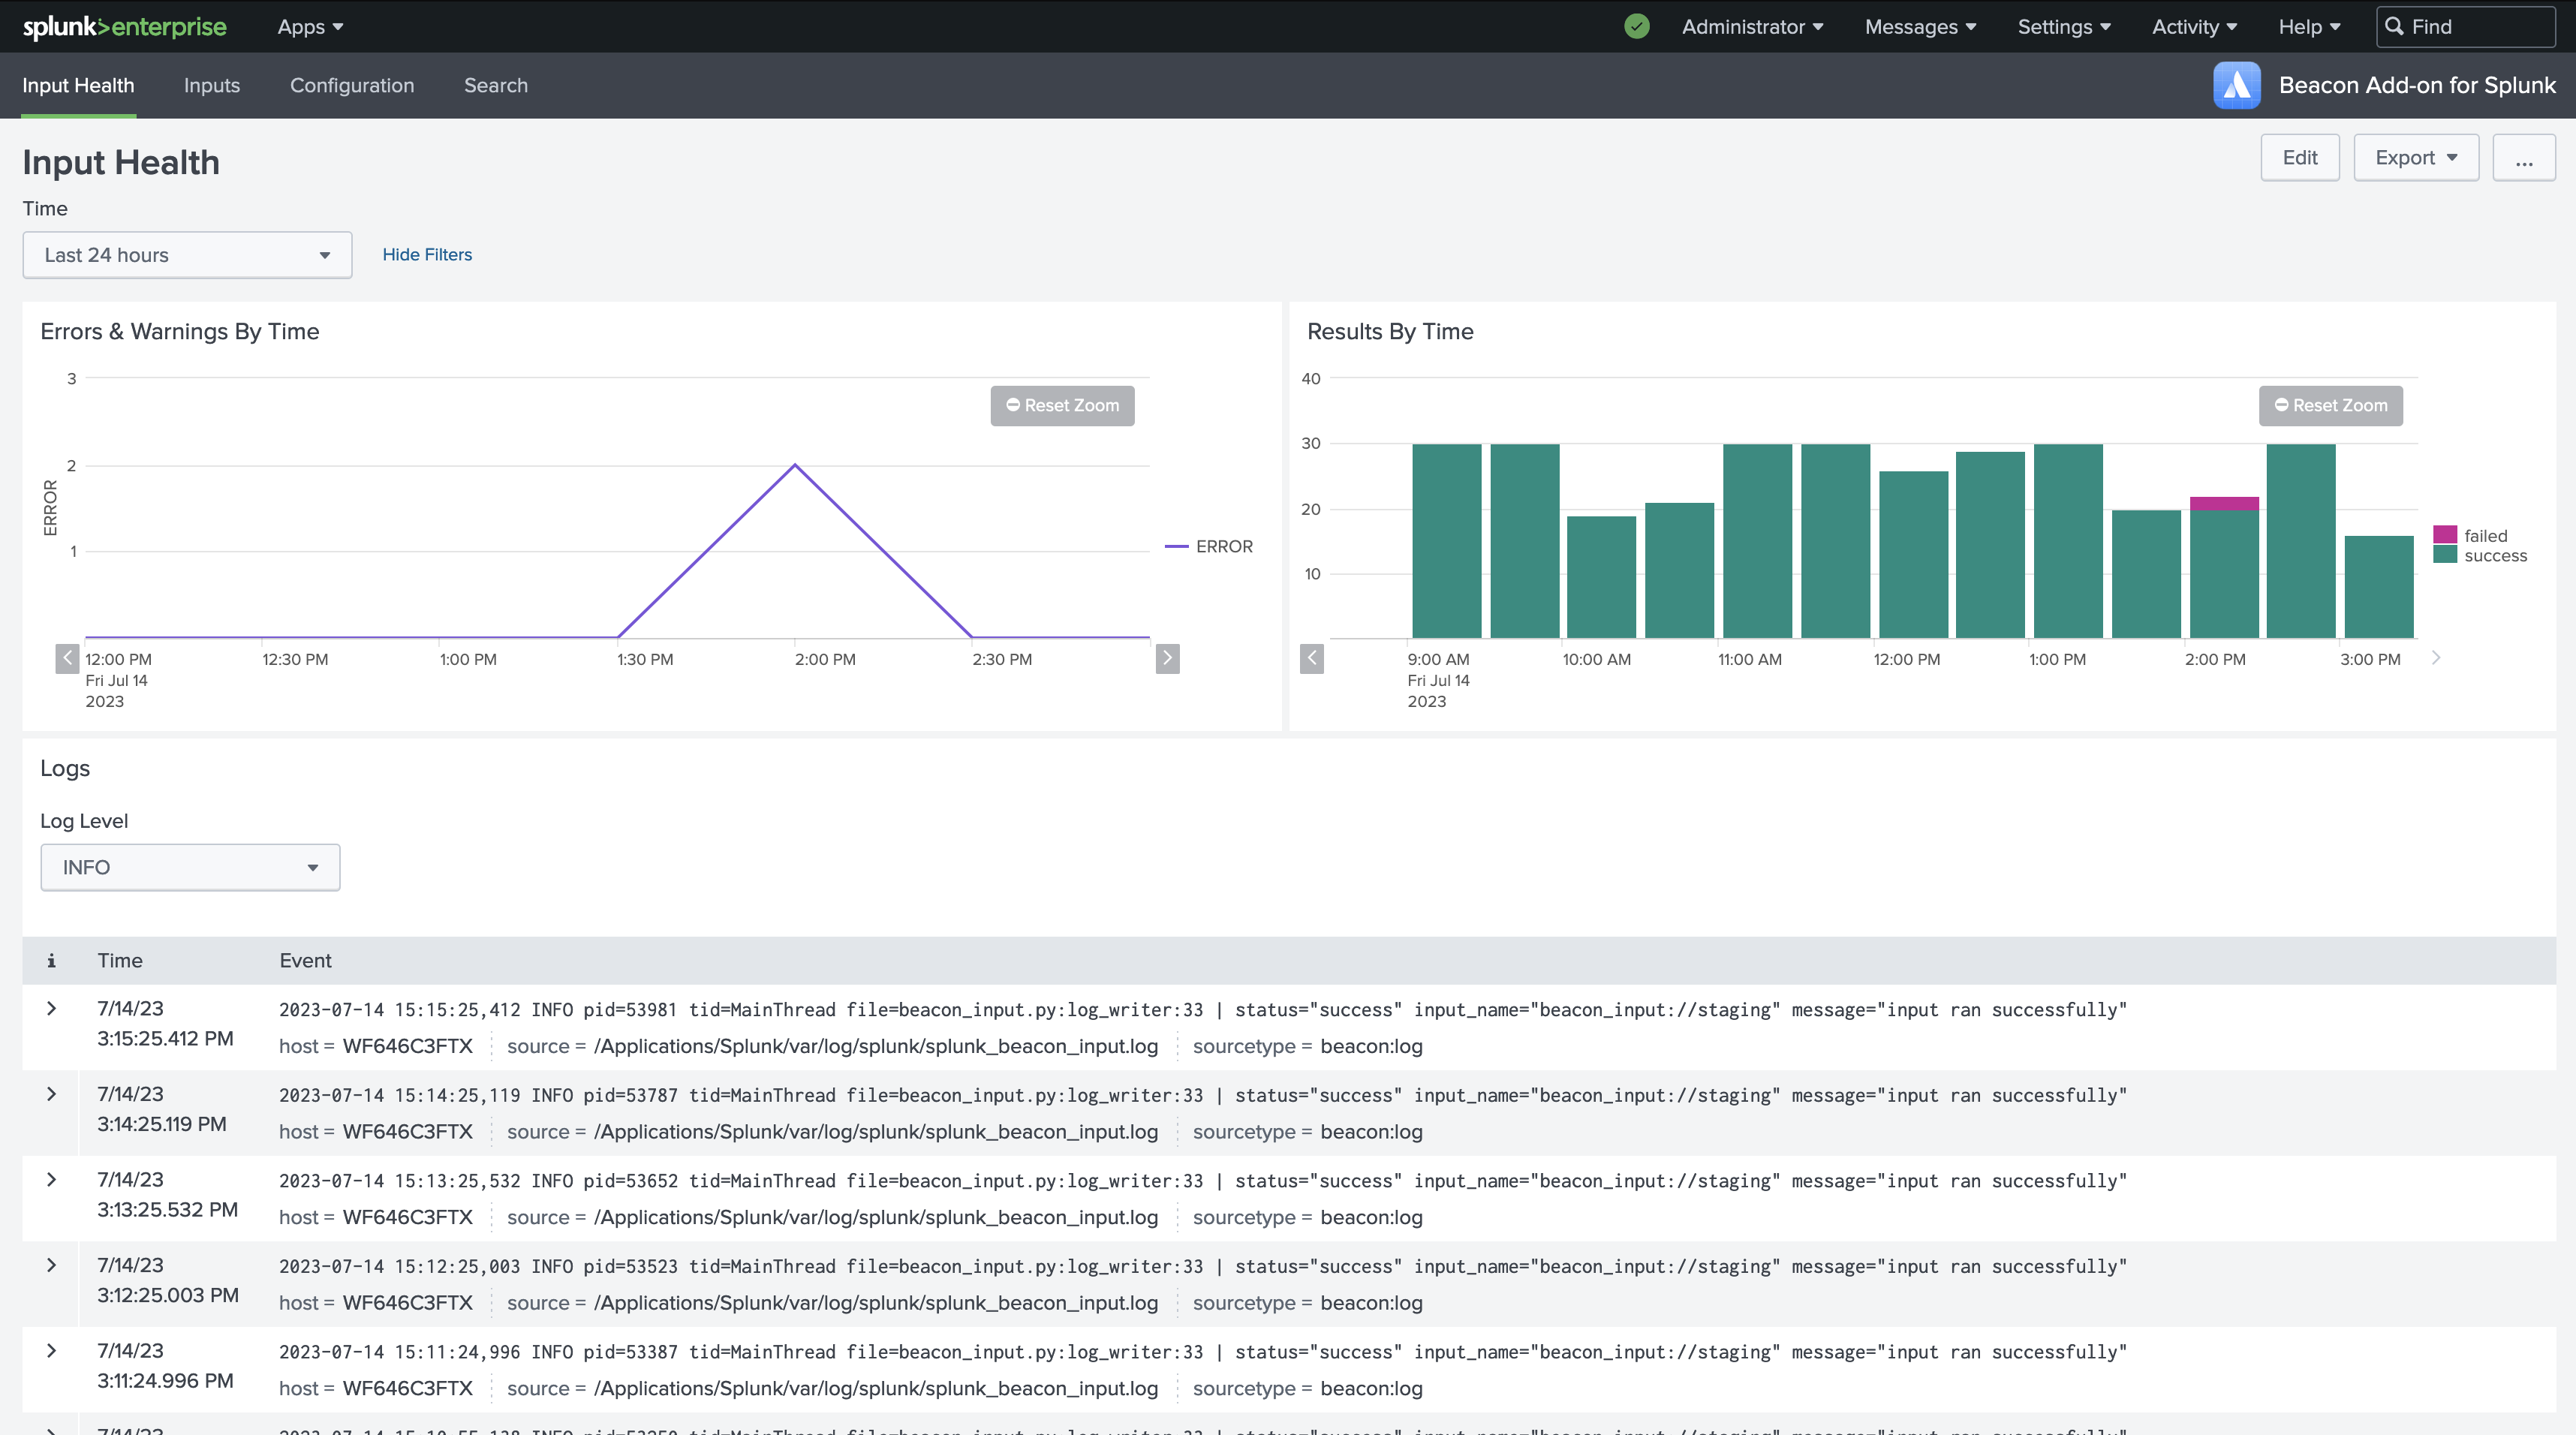
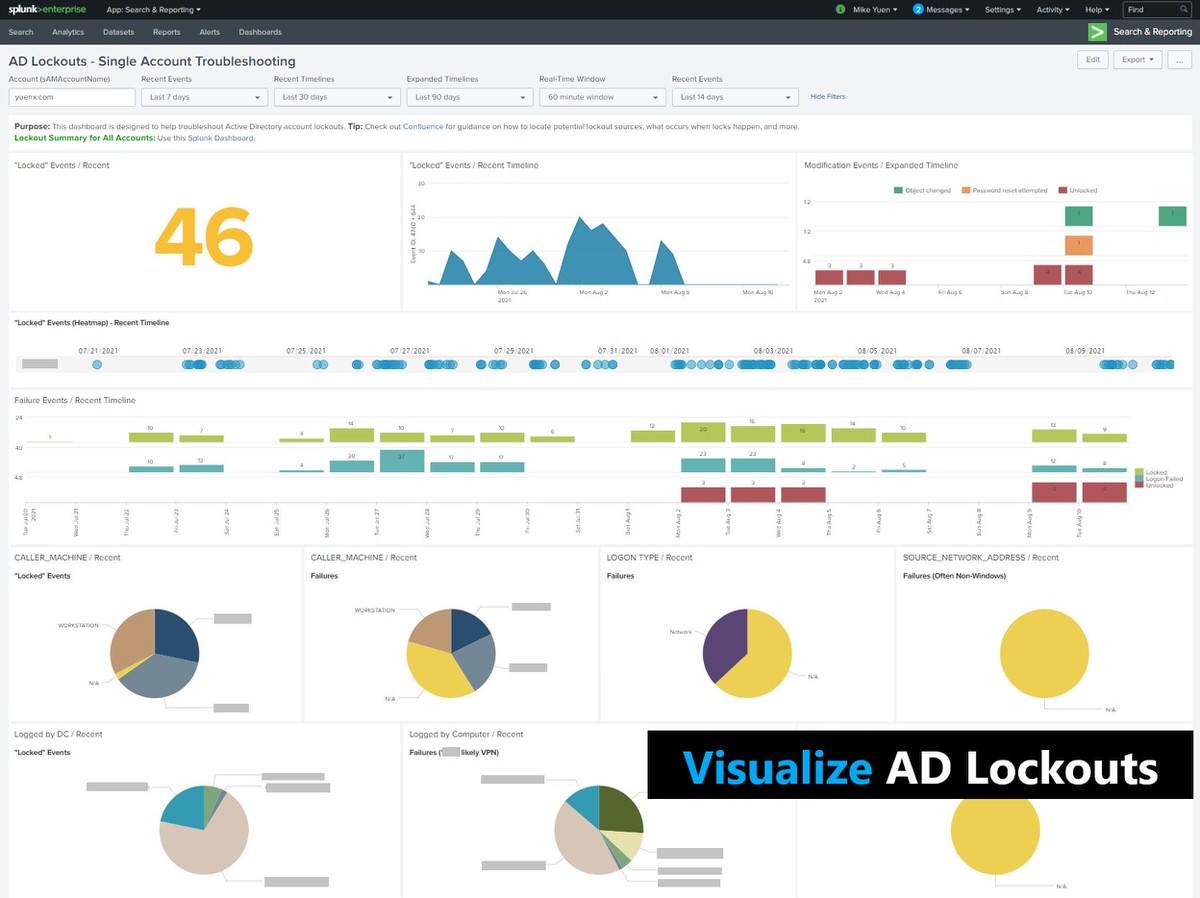
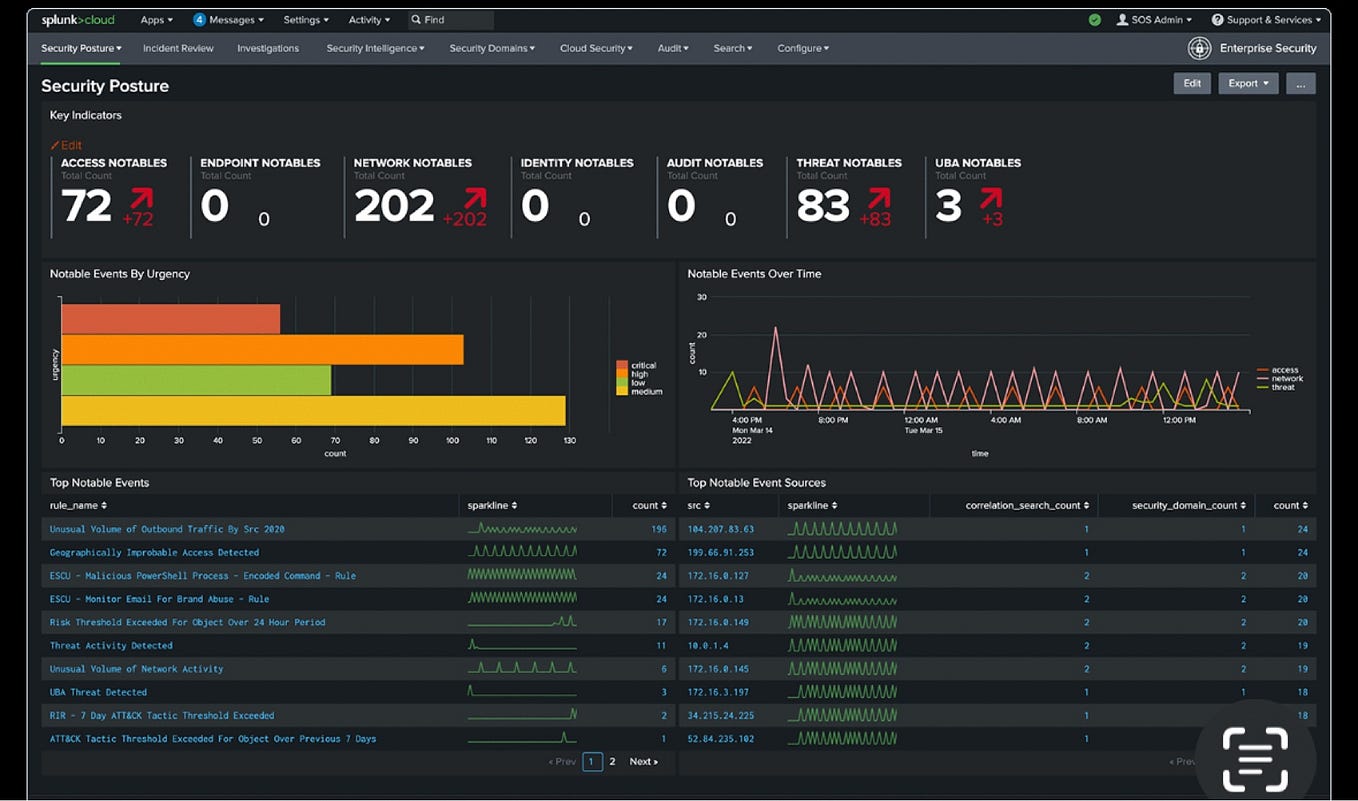
Dashboards turn repetitive queries into real-time visual stories. A single-panel dashboard showing login success versus failure rates over time immediately reveals brute-force campaigns or credential stuffing attacks. Timechart visualizations highlight usage patterns, heatmaps expose peak login hours, and pie charts break down login types—giving stakeholders instant clarity without running a single query.
Compliance and Auditing
Regulatory frameworks require proof of access control oversight. Splunk's scheduled reports deliver periodic summaries of who accessed which systems and when. Audit trails stored with immutable data retention policies satisfy auditors by demonstrating consistent monitoring and rapid incident response capabilities.
Best Practices
Start small with focused queries, then expand. Regularly update correlation searches to reflect evolving threats, and ensure log sources remain consistently onboarded as infrastructure changes. The goal is continuous visibility—turning login history from a passive log into an active security asset.