"Master Wireshark: Advanced Tutorial for Network Pros"
If you've already mastered the basics of Wireshark—capturing packets, applying simple filters, and following TCP streams—it's time to dive into its more powerful capabilities. This advanced Wireshark tutorial explores techniques and features that separate casual users from network analysis professionals, helping you uncover hidden issues, optimize performance, and strengthen security postures.
Advanced Display Filters That Save Hours

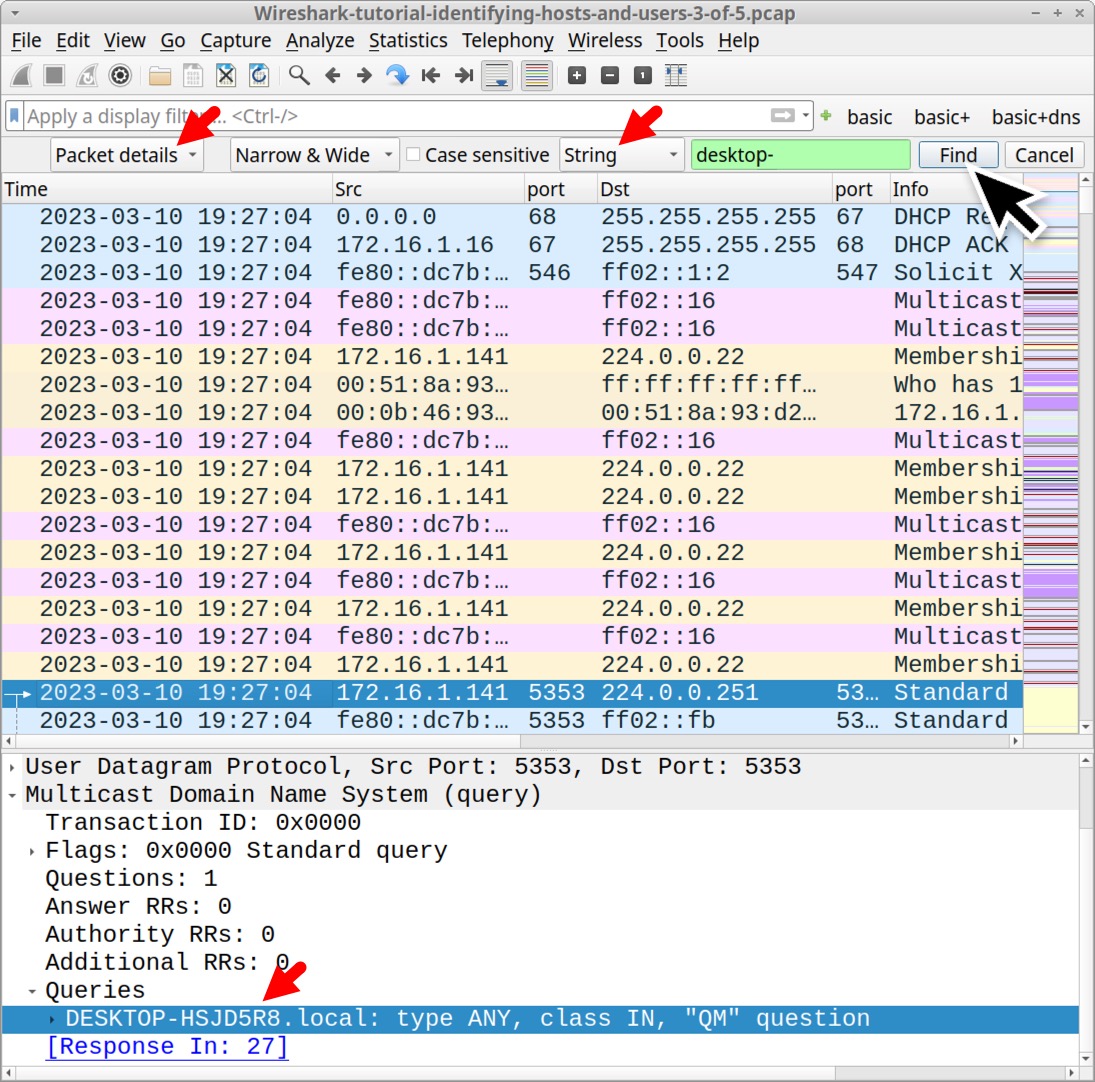
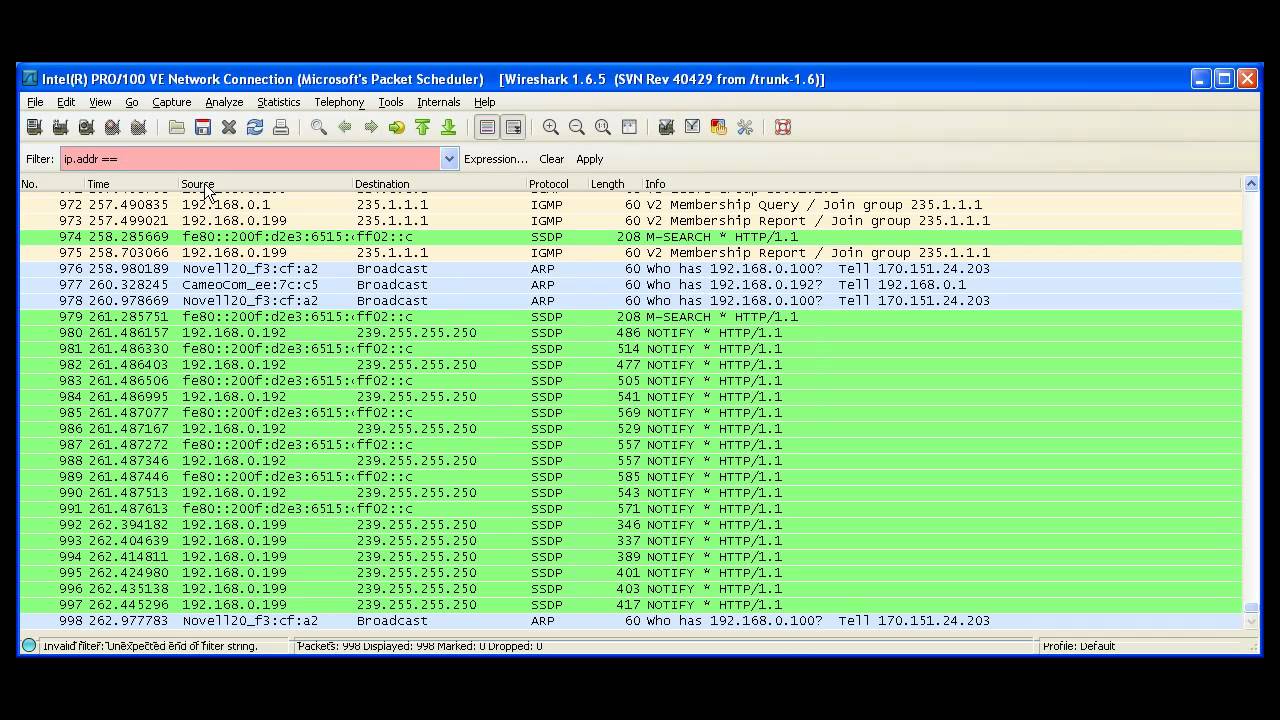
Beyond simple protocol filters like tcp or http, Wireshark supports complex boolean expressions and protocol-specific field matching. For instance, tcp.analysis.retransmission && ip.src == 192.168.1.10 isolates retransmissions from a specific host, pinpointing unreliable connections instantly. You can also filter by TCP flags using expressions like tcp.flags.syn == 1 && tcp.flags.ack == 0 to spot unsolicited SYN requests—often indicators of port scans.
| Filter Expression | Purpose |
|---|---|
tcp.analysis.duplicate_ack |
Detects duplicate ACK events signaling packet loss |
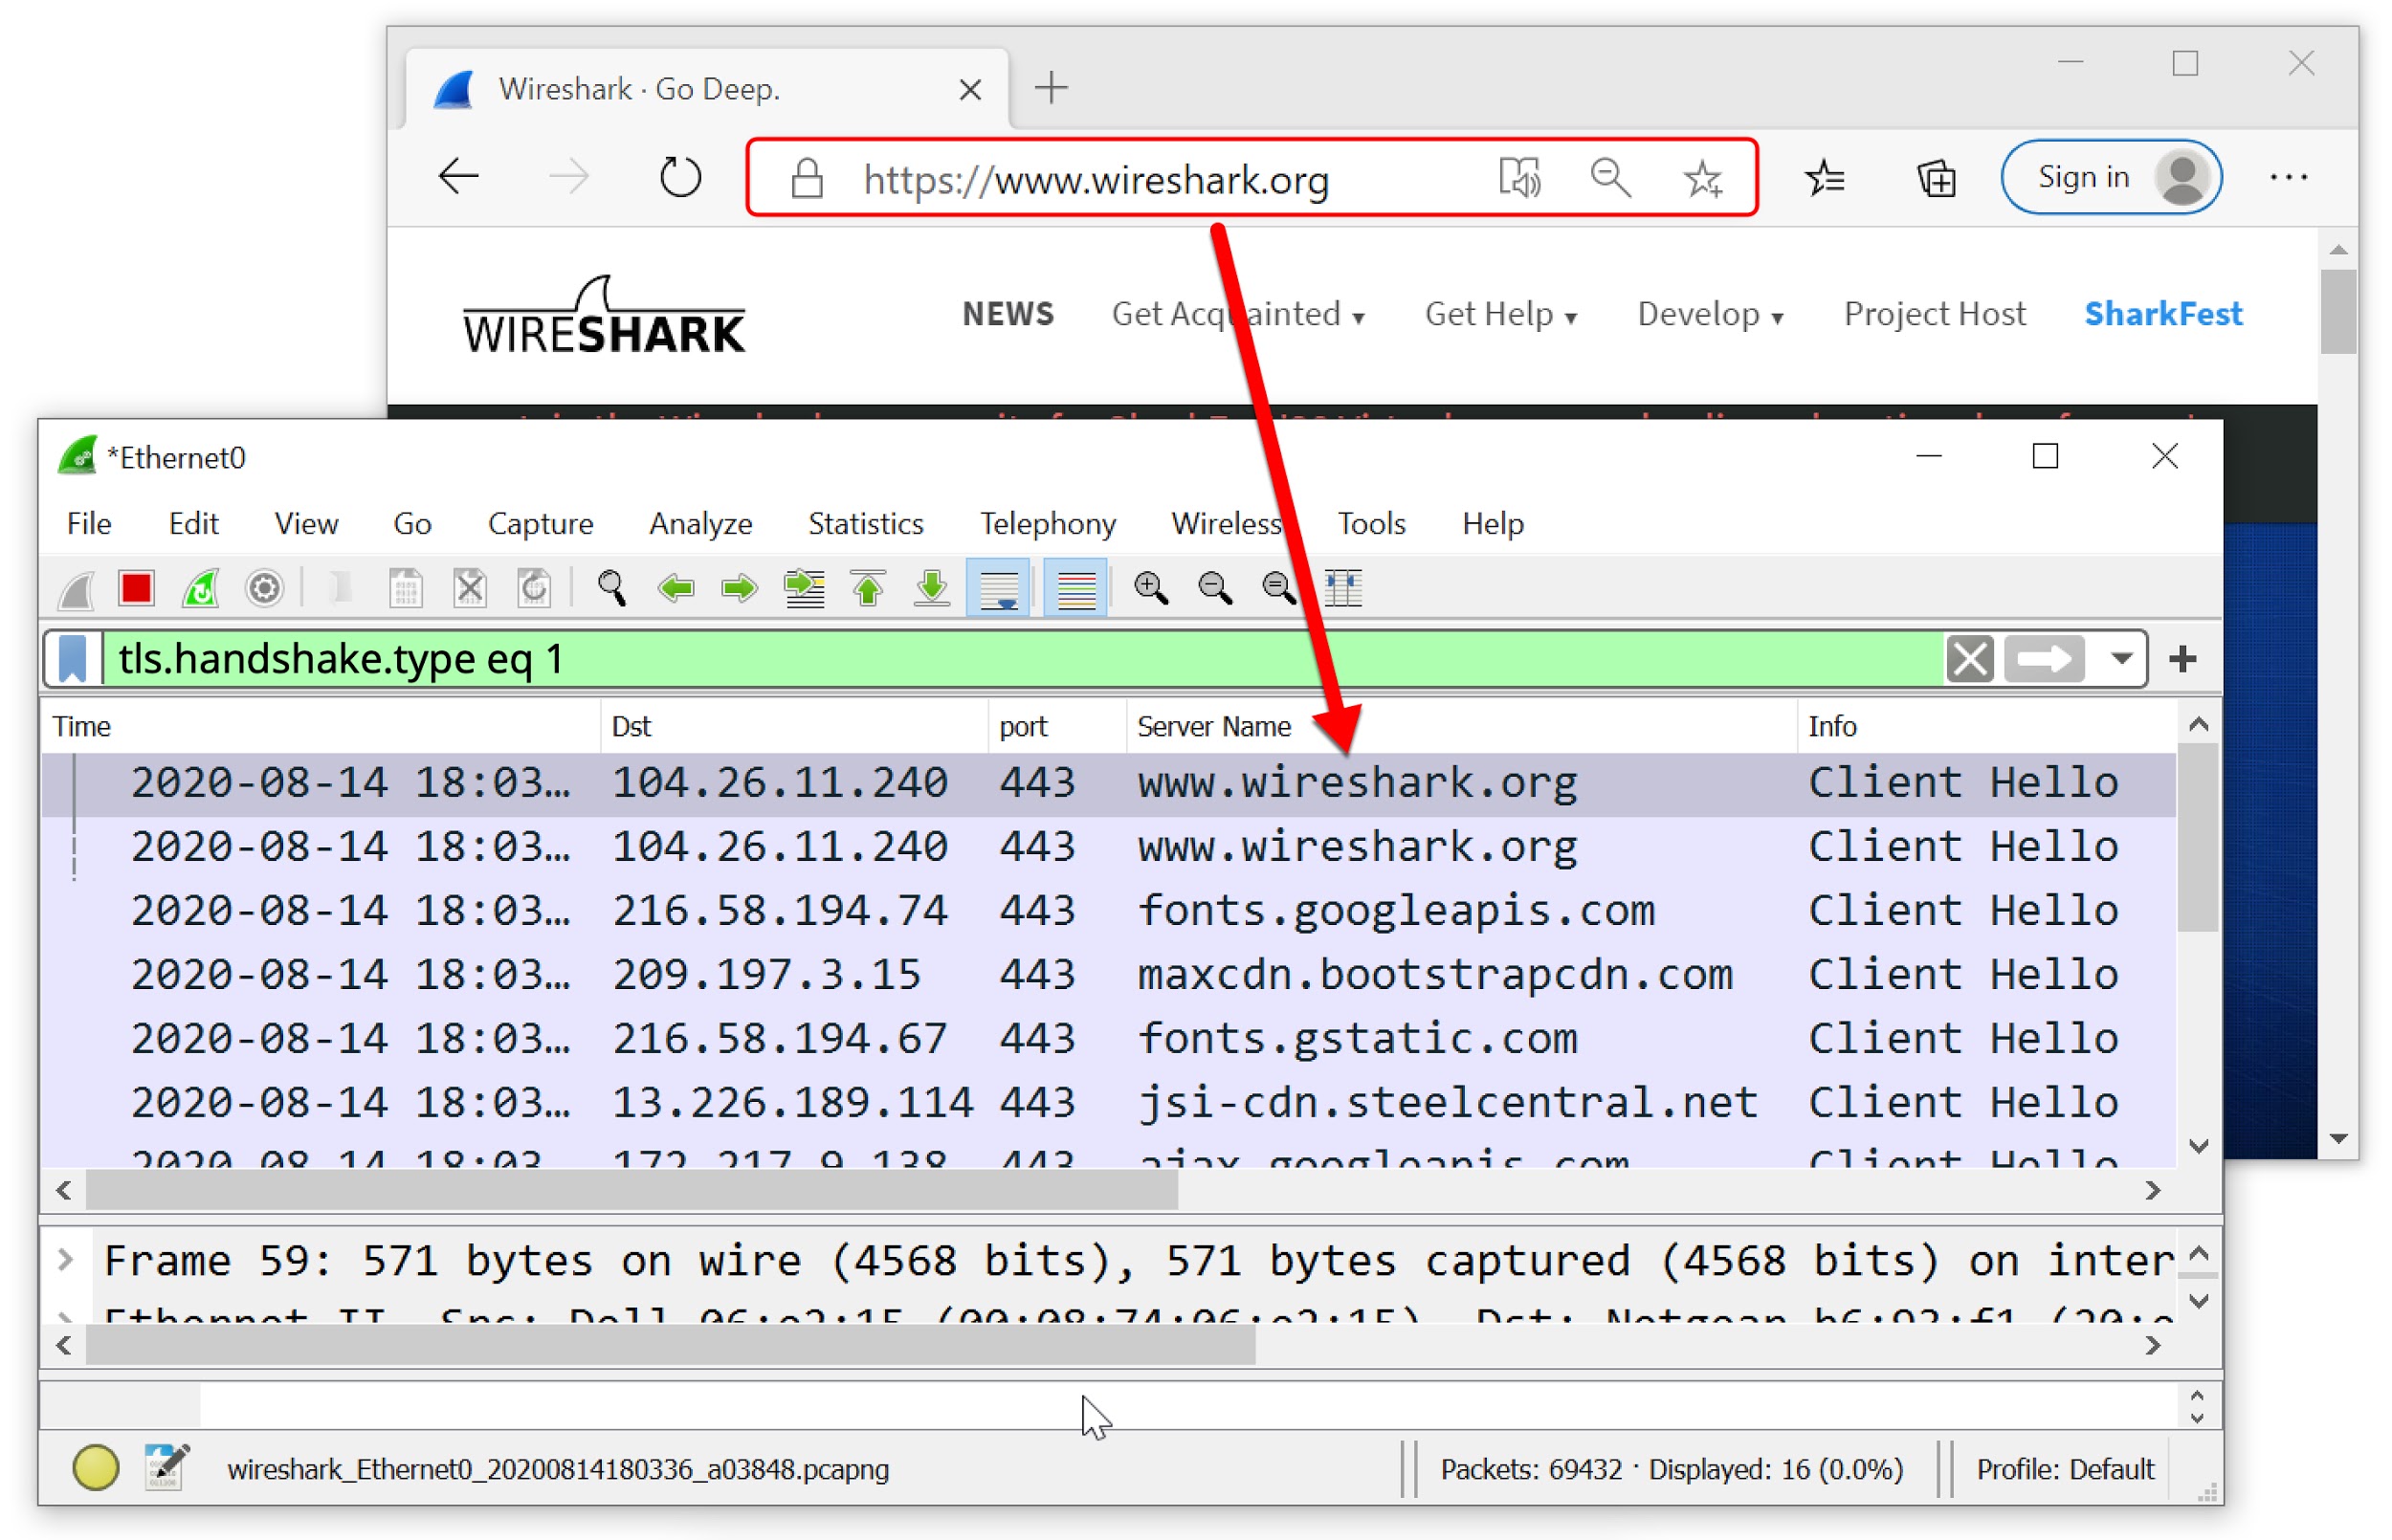
tls.handshake.type == 1 |
Captures Client Hello packets for TLS analysis |
icmp.type == 3 |
Shows "Destination Unreachable" messages |

Custom Profiles and Coloring Rules for Clarity
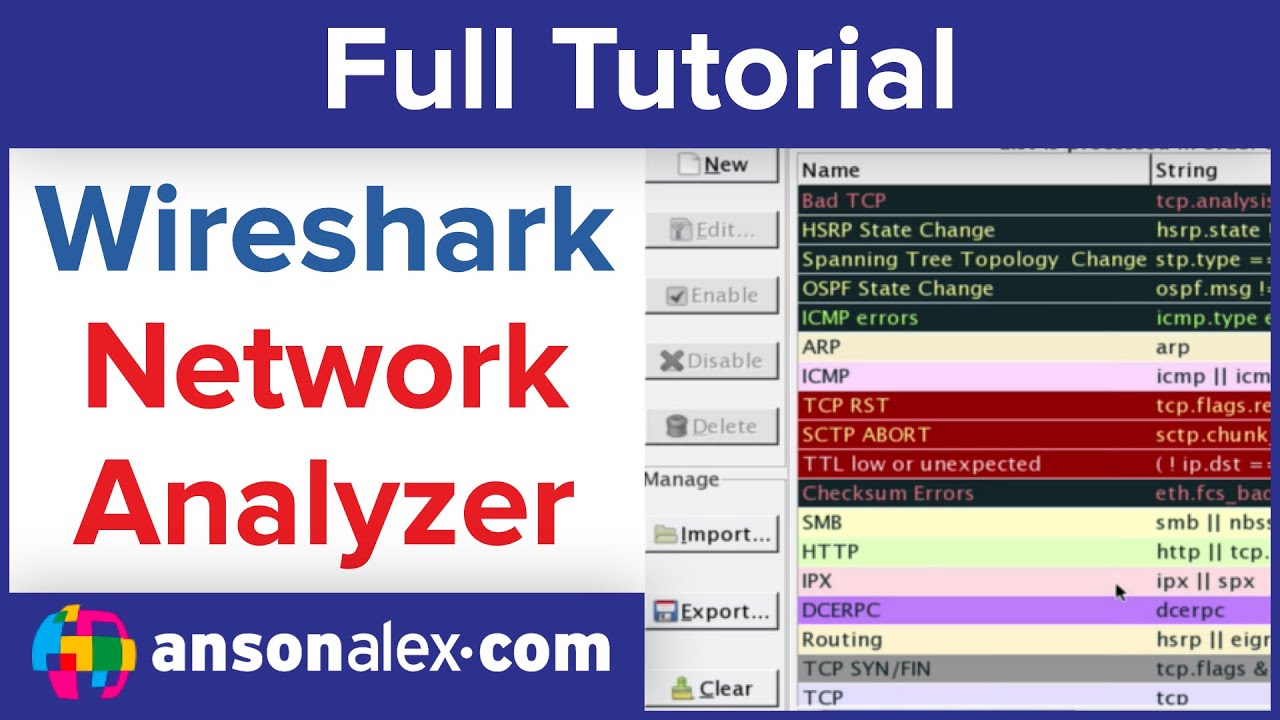
When analyzing large captures, visual noise becomes a serious problem. Wireshark's profile system lets you create custom configurations tailored to specific tasks. Set up a "VoIP Troubleshooting" profile with coloring rules that highlight SIP (green), RTP (blue), and error packets (red). Another profile might focus on HTTP/2, with rules that color different streams distinctly. To create a custom color rule, navigate to View > Coloring Rules, then add a new rule with a descriptive name and precise filter expression.

Expert Information and Anomaly Detection
The Analyze > Expert Information panel aggregates warnings, errors, and notes across your entire capture. Instead of manually scrolling through thousands of packets, this tool surfaces critical anomalies like window zero, out-of-order segments, and malformed packets. Each entry includes packet numbers for immediate navigation. For security analysts, the "Errors" category often reveals crafted packets attempting protocol violations.
Decryption of Encrypted Traffic
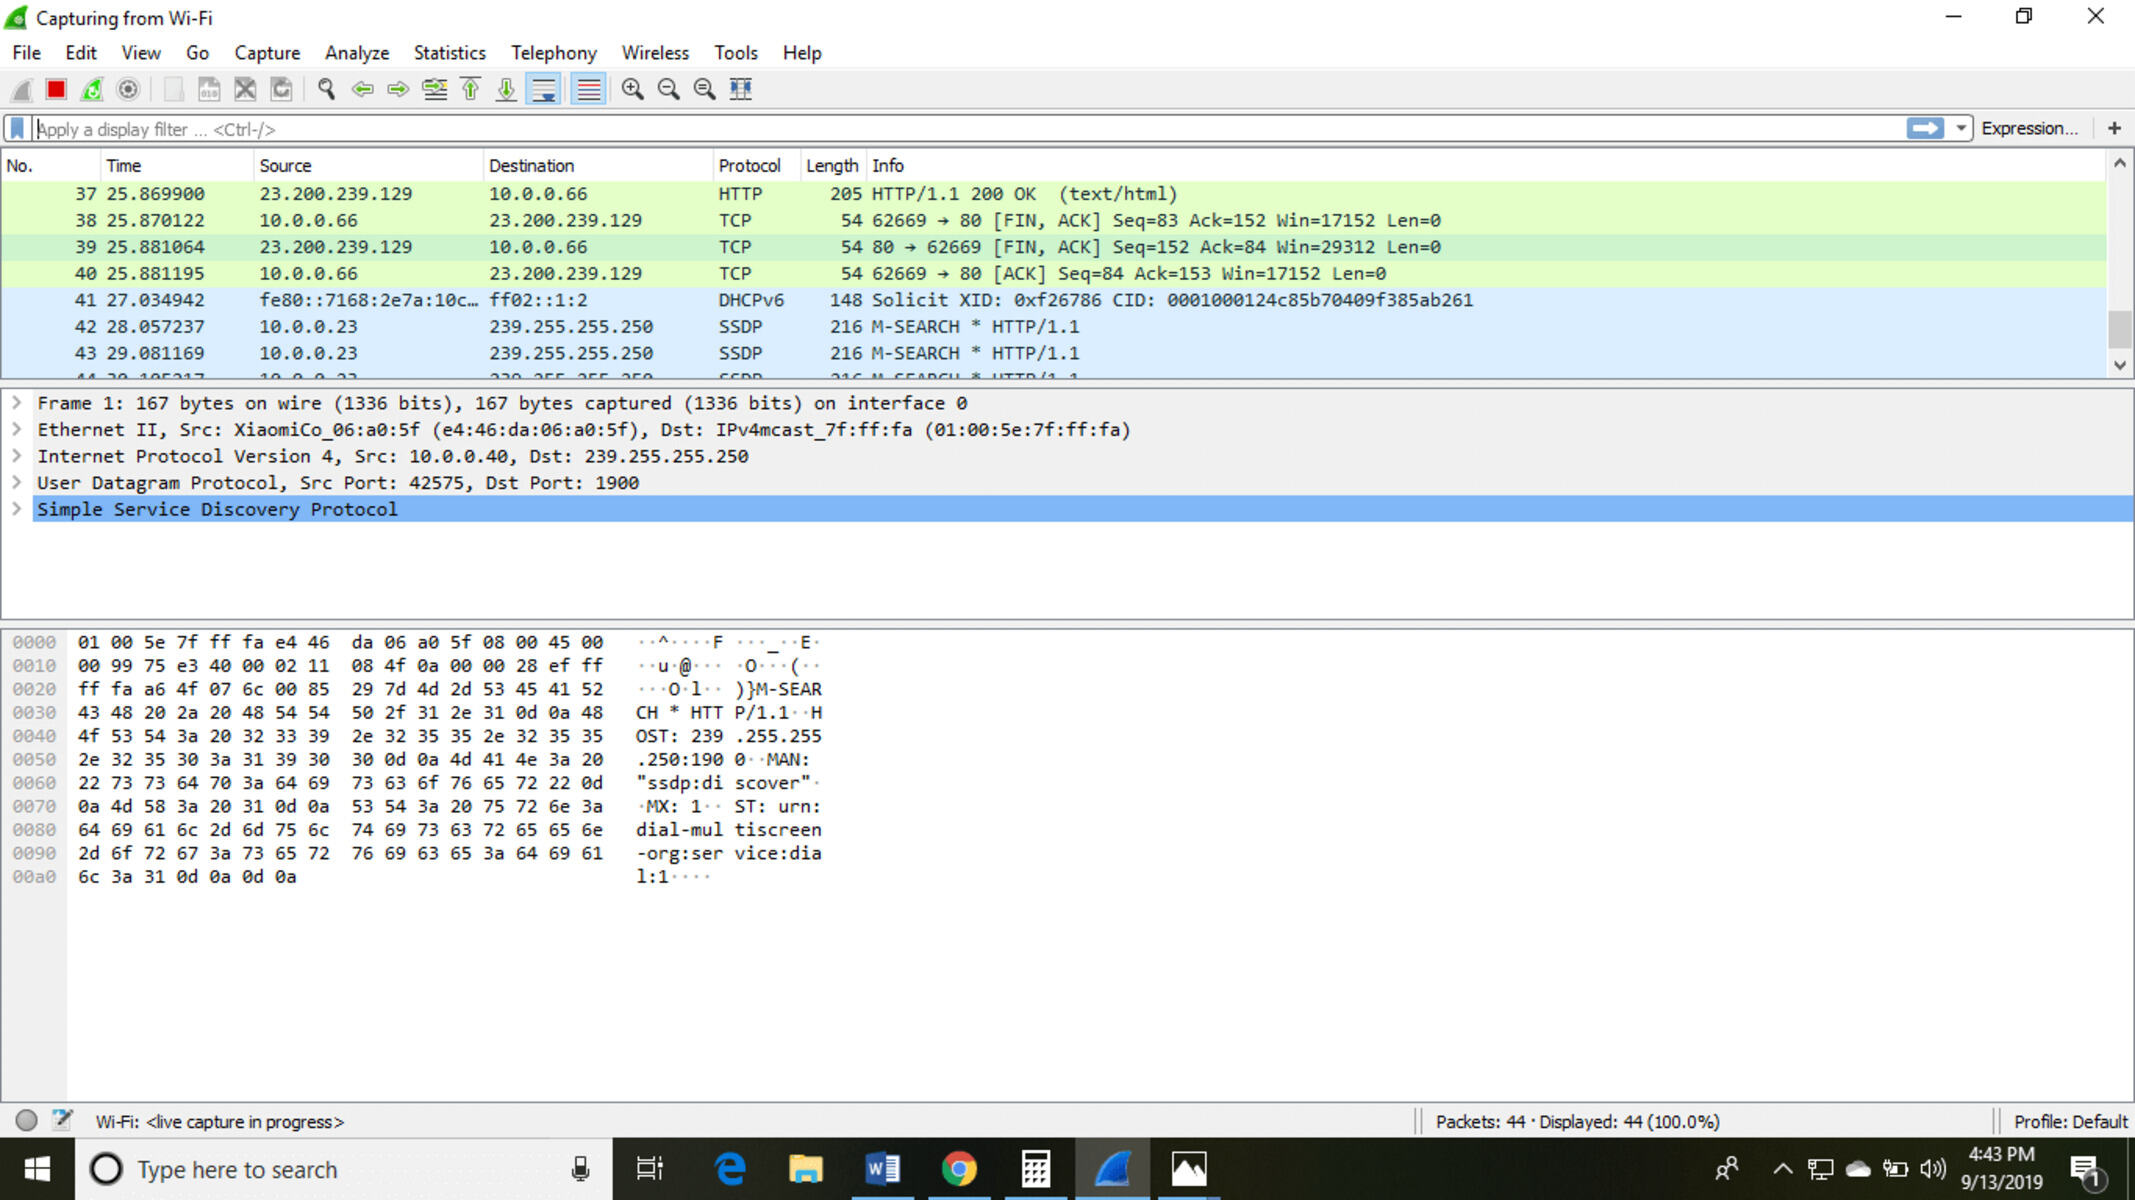
Wireshark can decrypt TLS traffic when provided with the pre-master secret. Configure it via Edit > Preferences > Protocols > TLS, then add the (Pre)-Master-Secret log filename. When your browser or application writes this log file during the session, Wireshark automatically decrypts the captured packets. For older protocols like WEP or WPA, Wireshark handles decryption differently—WEP keys go in Edit > Preferences > Protocols > IEEE 802.11, while WPA decryption requires the network's PSK added to the same settings.
Command-Line Power with tshark
For automated analysis or server environments without GUIs, tshark delivers Wireshark's filtering power in a terminal. A command like tshark -r capture.pcap -Y "dns.qry.name contains malware" -T fields -e dns.qry.name extracts suspicious DNS queries from a file without launching the full interface. When scripting incident response workflows, pair tshark with tools like awk or jq for structured JSON output using -T json.

I/O Graphs and Throughput Analysis
The Statistics > I/O Graph feature transforms packet data into visual throughput trends over time. Graph multiple metrics simultaneously—one line for TCP retransmissions (filter: tcp.analysis.retransmission) alongside total bandwidth usage (filter: tcp.len > 0). When these graphs spike together, you have quantitative proof that network degradation causes performance problems. Export these graphs as images for reports that demand visual evidence alongside raw packet data.






Mastering these advanced Wireshark techniques transforms routine packet captures into actionable intelligence. Whether diagnosing microsecond TLS handshake failures or correlating application slowness with TCP window size issues, these methods provide the depth required for professional network analysis. Practice with sample captures from Wireshark's Sample Captures wiki, applying these advanced filters and analysis methods to real-world scenarios.