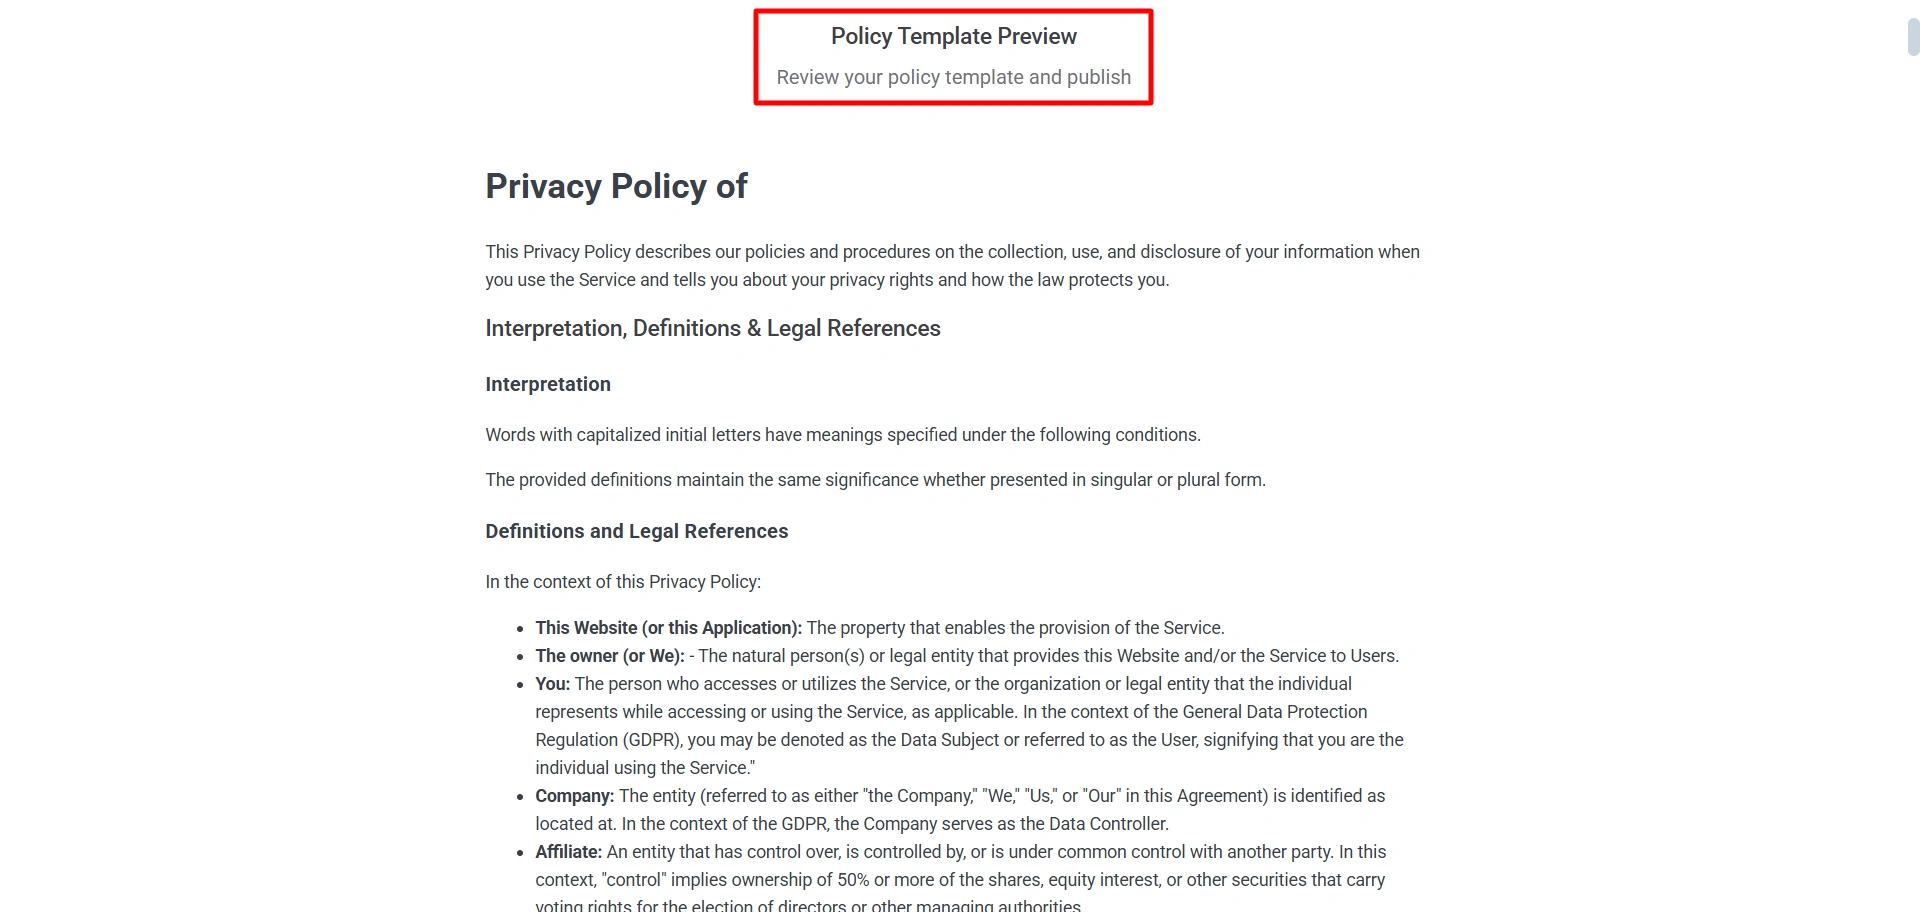
If you are wondering how do I create a privacy policy for my website, the answer is more straightforward than most people think, but getting it right is what separates a legally compliant site from a lawsuit waiting to happen. A privacy policy isn't just a box to check for your legal page—it’s a binding contract between you and your users. Whether you run a solo blog or a massive e-commerce store, your visitors deserve to know exactly how their data is handled, and the law increasingly demands you tell them.
Why a Privacy Policy is Non-Negotiable
Before you write a single word, understand that a privacy policy is a legal requirement in many jurisdictions. Regulations like GDPR in Europe and CCPA in California aren't optional guidelines; they carry heavy fines for non-compliance. Beyond the legal necessity, a clear, transparent policy builds trust. Users are more likely to share information and convert when they feel their data is safe. To start, you need to identify which laws apply to your specific audience. If you have users in the EU, GDPR is your baseline. If you operate in California, CCPA is non-negotiable. This foundational step dictates the language and depth of your policy.
Key Components Every Privacy Policy Must Contain
Your policy needs to be comprehensive. When you sit down to create a privacy policy for your website, there are core elements you cannot leave out. It must clearly state what data you collect, how you use it, and how you store and protect it. Vague language is your enemy here. Users and regulators alike prefer specifics: name, email, IP address, and device information.
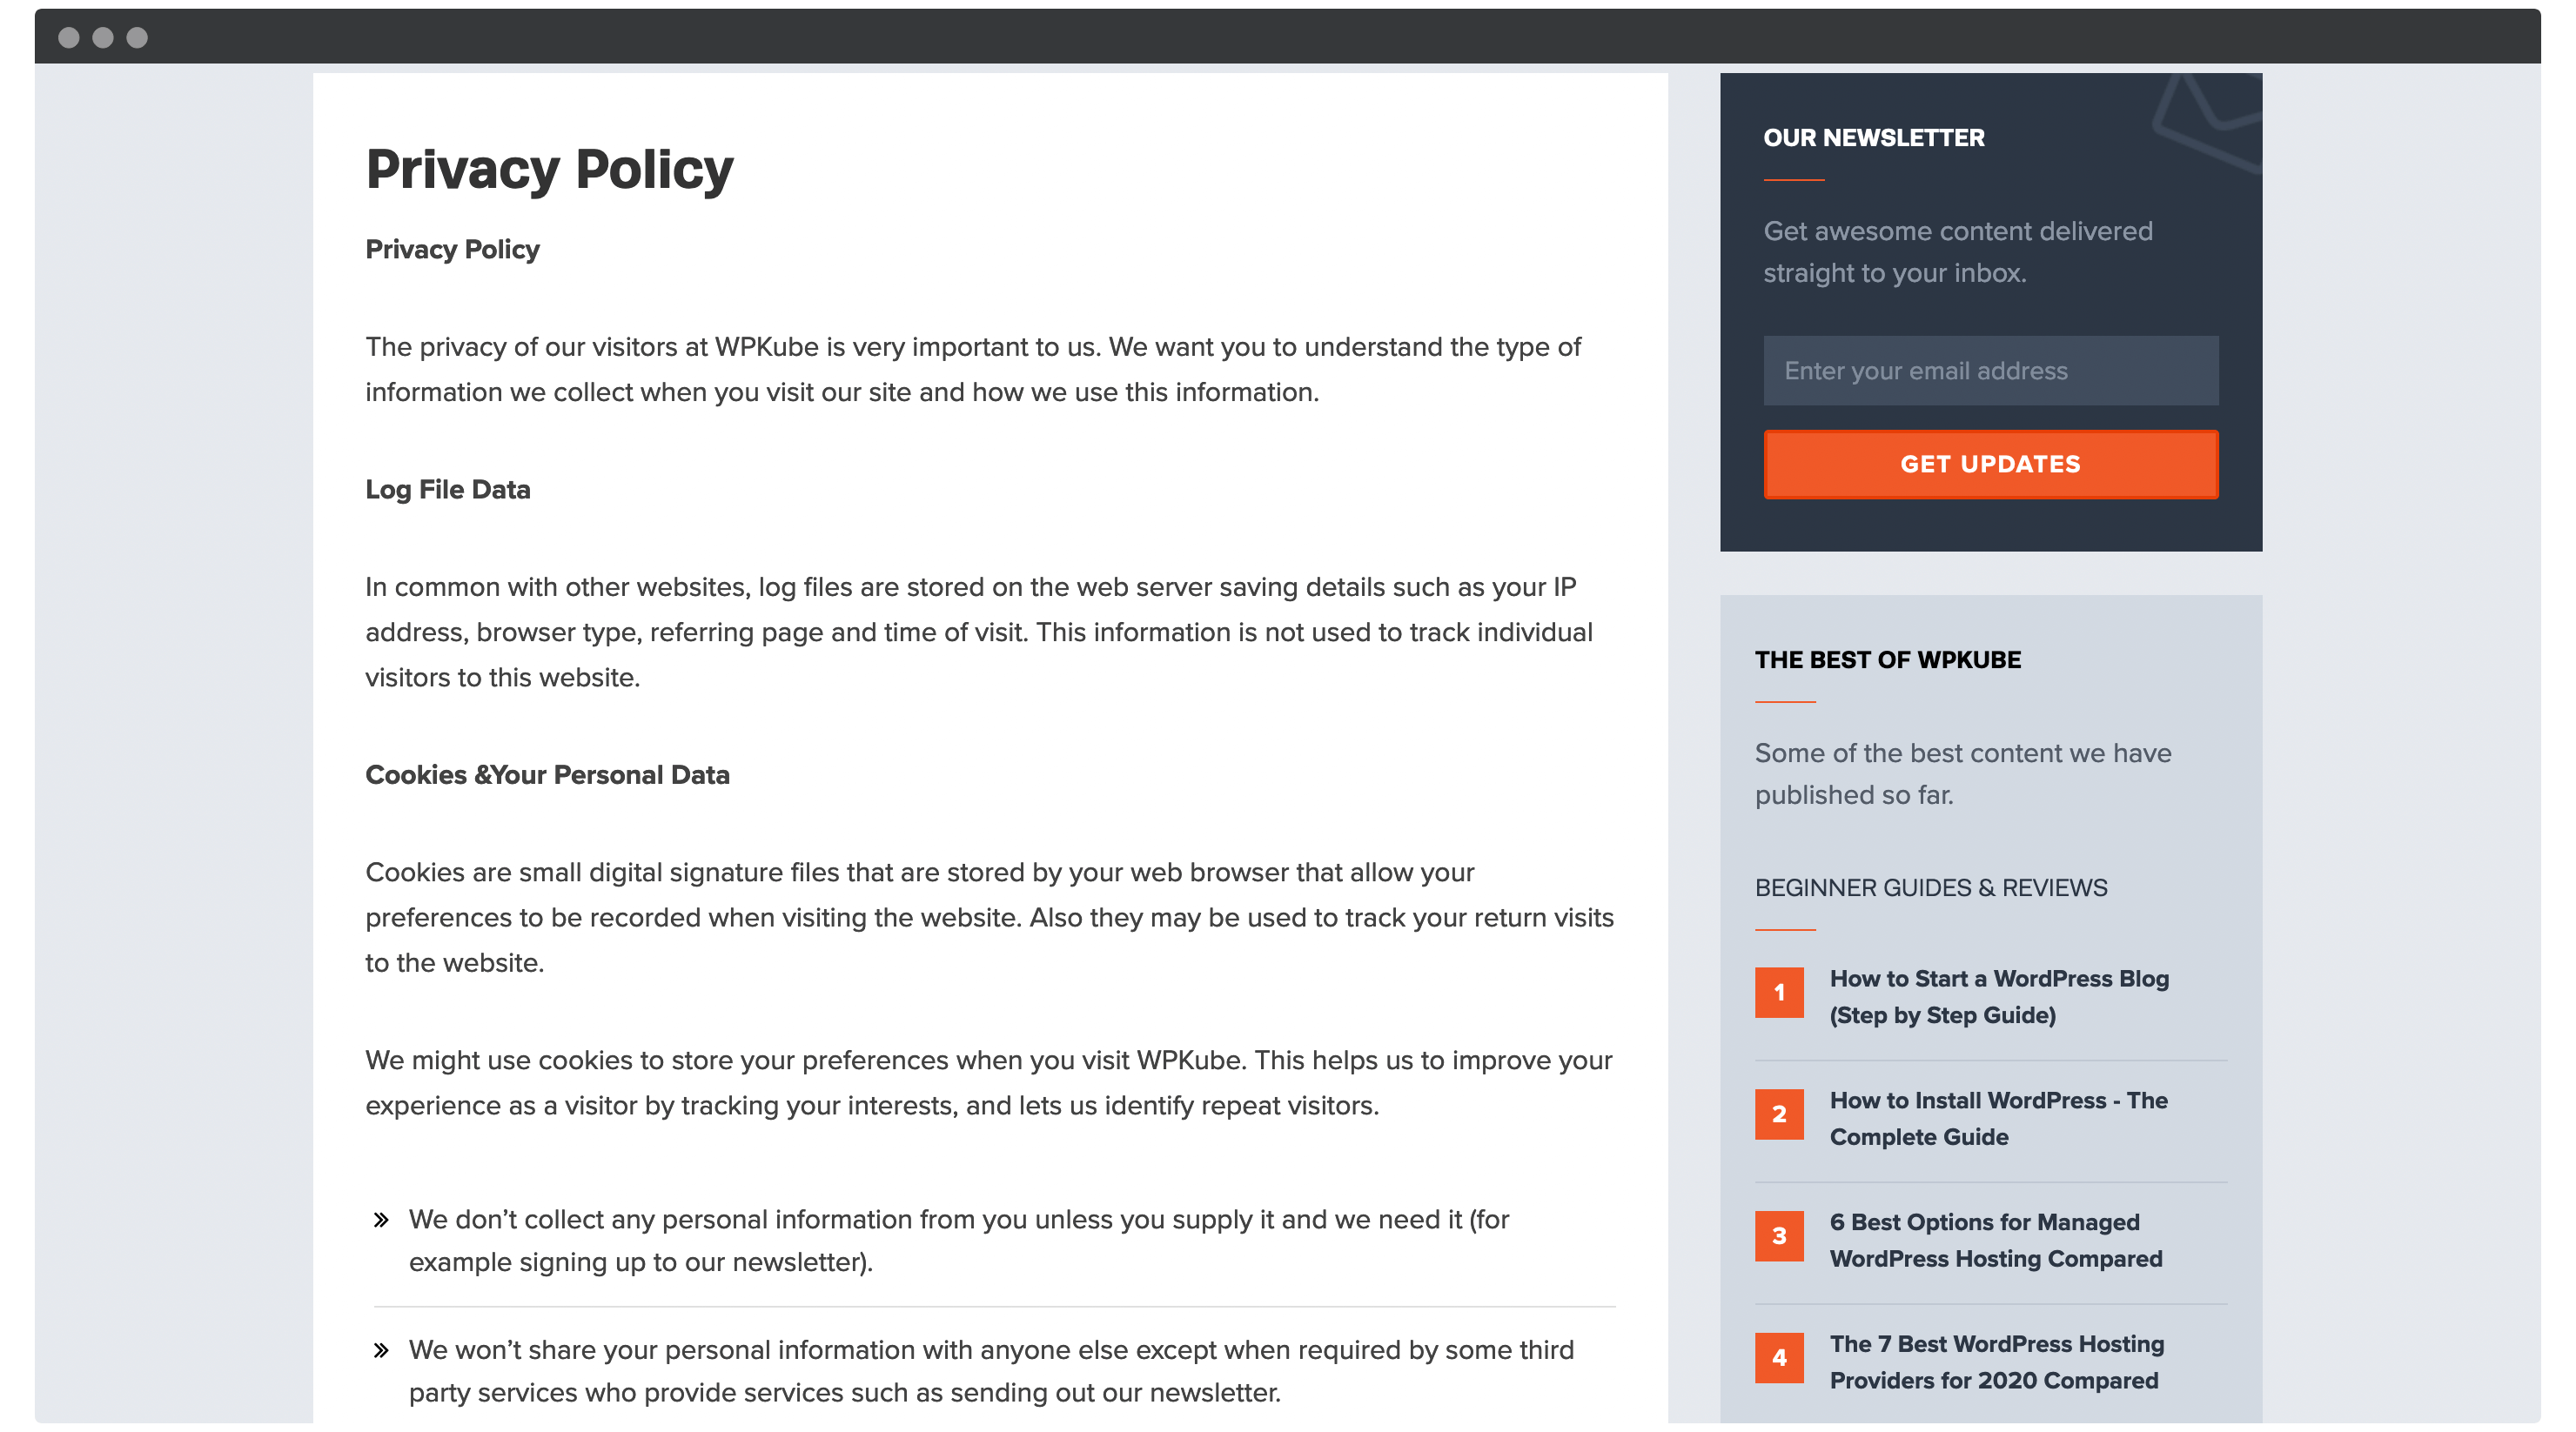
- Types of Data Collected: List every category of personal data you gather.
- Methods of Collection: Direct (forms, cookies, analytics).
- Purpose of Collection: Be specific about why you need the data (service delivery, marketing).
- Third-Party Sharing: Disclose every entity that receives user data (ad networks, payment processors).
Step-by-Step: Drafting Your Privacy Policy
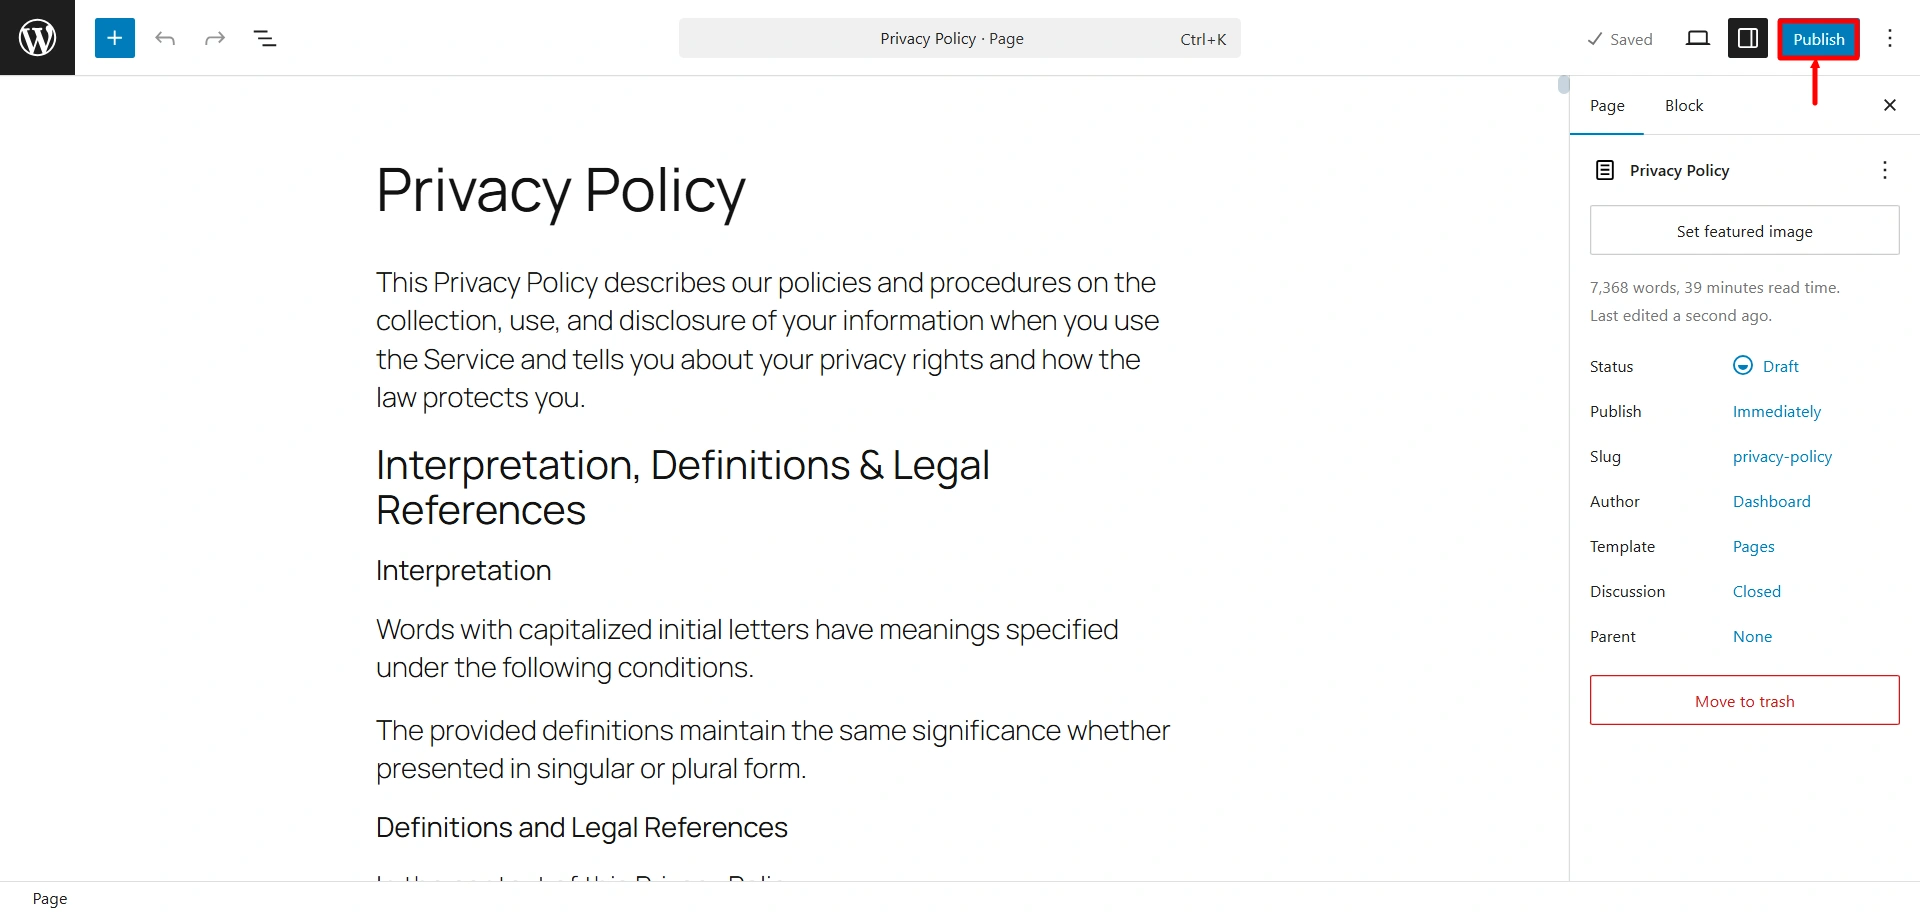
To effectively answer how do I create a privacy policy for my website, you need a structured approach. Don't just copy a template from another site; that path leads to legal gaps and missed fines. First, audit your data flows—map out every point where information enters and leaves your systems. Map your data collection points: forms, cookies, analytics, and logging. Second, choose a generator or a lawyer. For complex SaaS platforms or high-risk data, a lawyer is a must. Finally, draft the initial version, focusing on clarity. Use simple, direct legal English. Users should not need a law degree to understand your practices.
Choosing the Right Generator or Template
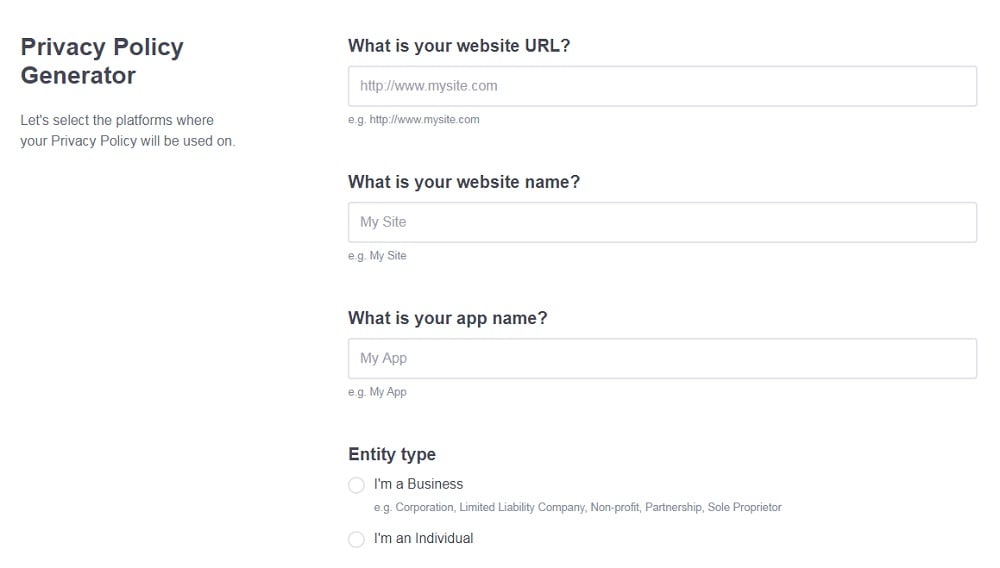
If you are wondering how do I create a privacy policy for my website without a budget for a lawyer, reputable generators can handle the boilerplate. Tools like Termly, Iubenda, or PrivacyPolicies.com allow you to answer a few questions and produce a solid base document. These tools stay updated with the law, saving you from maintaining legal text manually. However, these tools lack nuance. Always review the output with a legal eye before publishing.
| Method | Cost | Best For |
|---|---|---|
| Online Generator | Low/Free | Simple blogs, small sites |
| Lawyer | High ($$$) | SaaS, e-commerce, high-risk data |
Common Mistakes to Avoid
Most website owners fail not because they lack intent, but because they rely on outdated templates. If you are figuring out how to create a privacy policy for your website, never copy-paste from competitors. Their data flows differ from yours, leading to legal exposure. Another mistake is burying the policy in tiny font at the bottom of the page. Make it accessible and easy to find. If a regulator or user has to dig for your policy, you’ve already failed the transparency test. Remember, your policy is a living document. Every time you add a new tool, integrations, or third-party service, the document must reflect those changes.
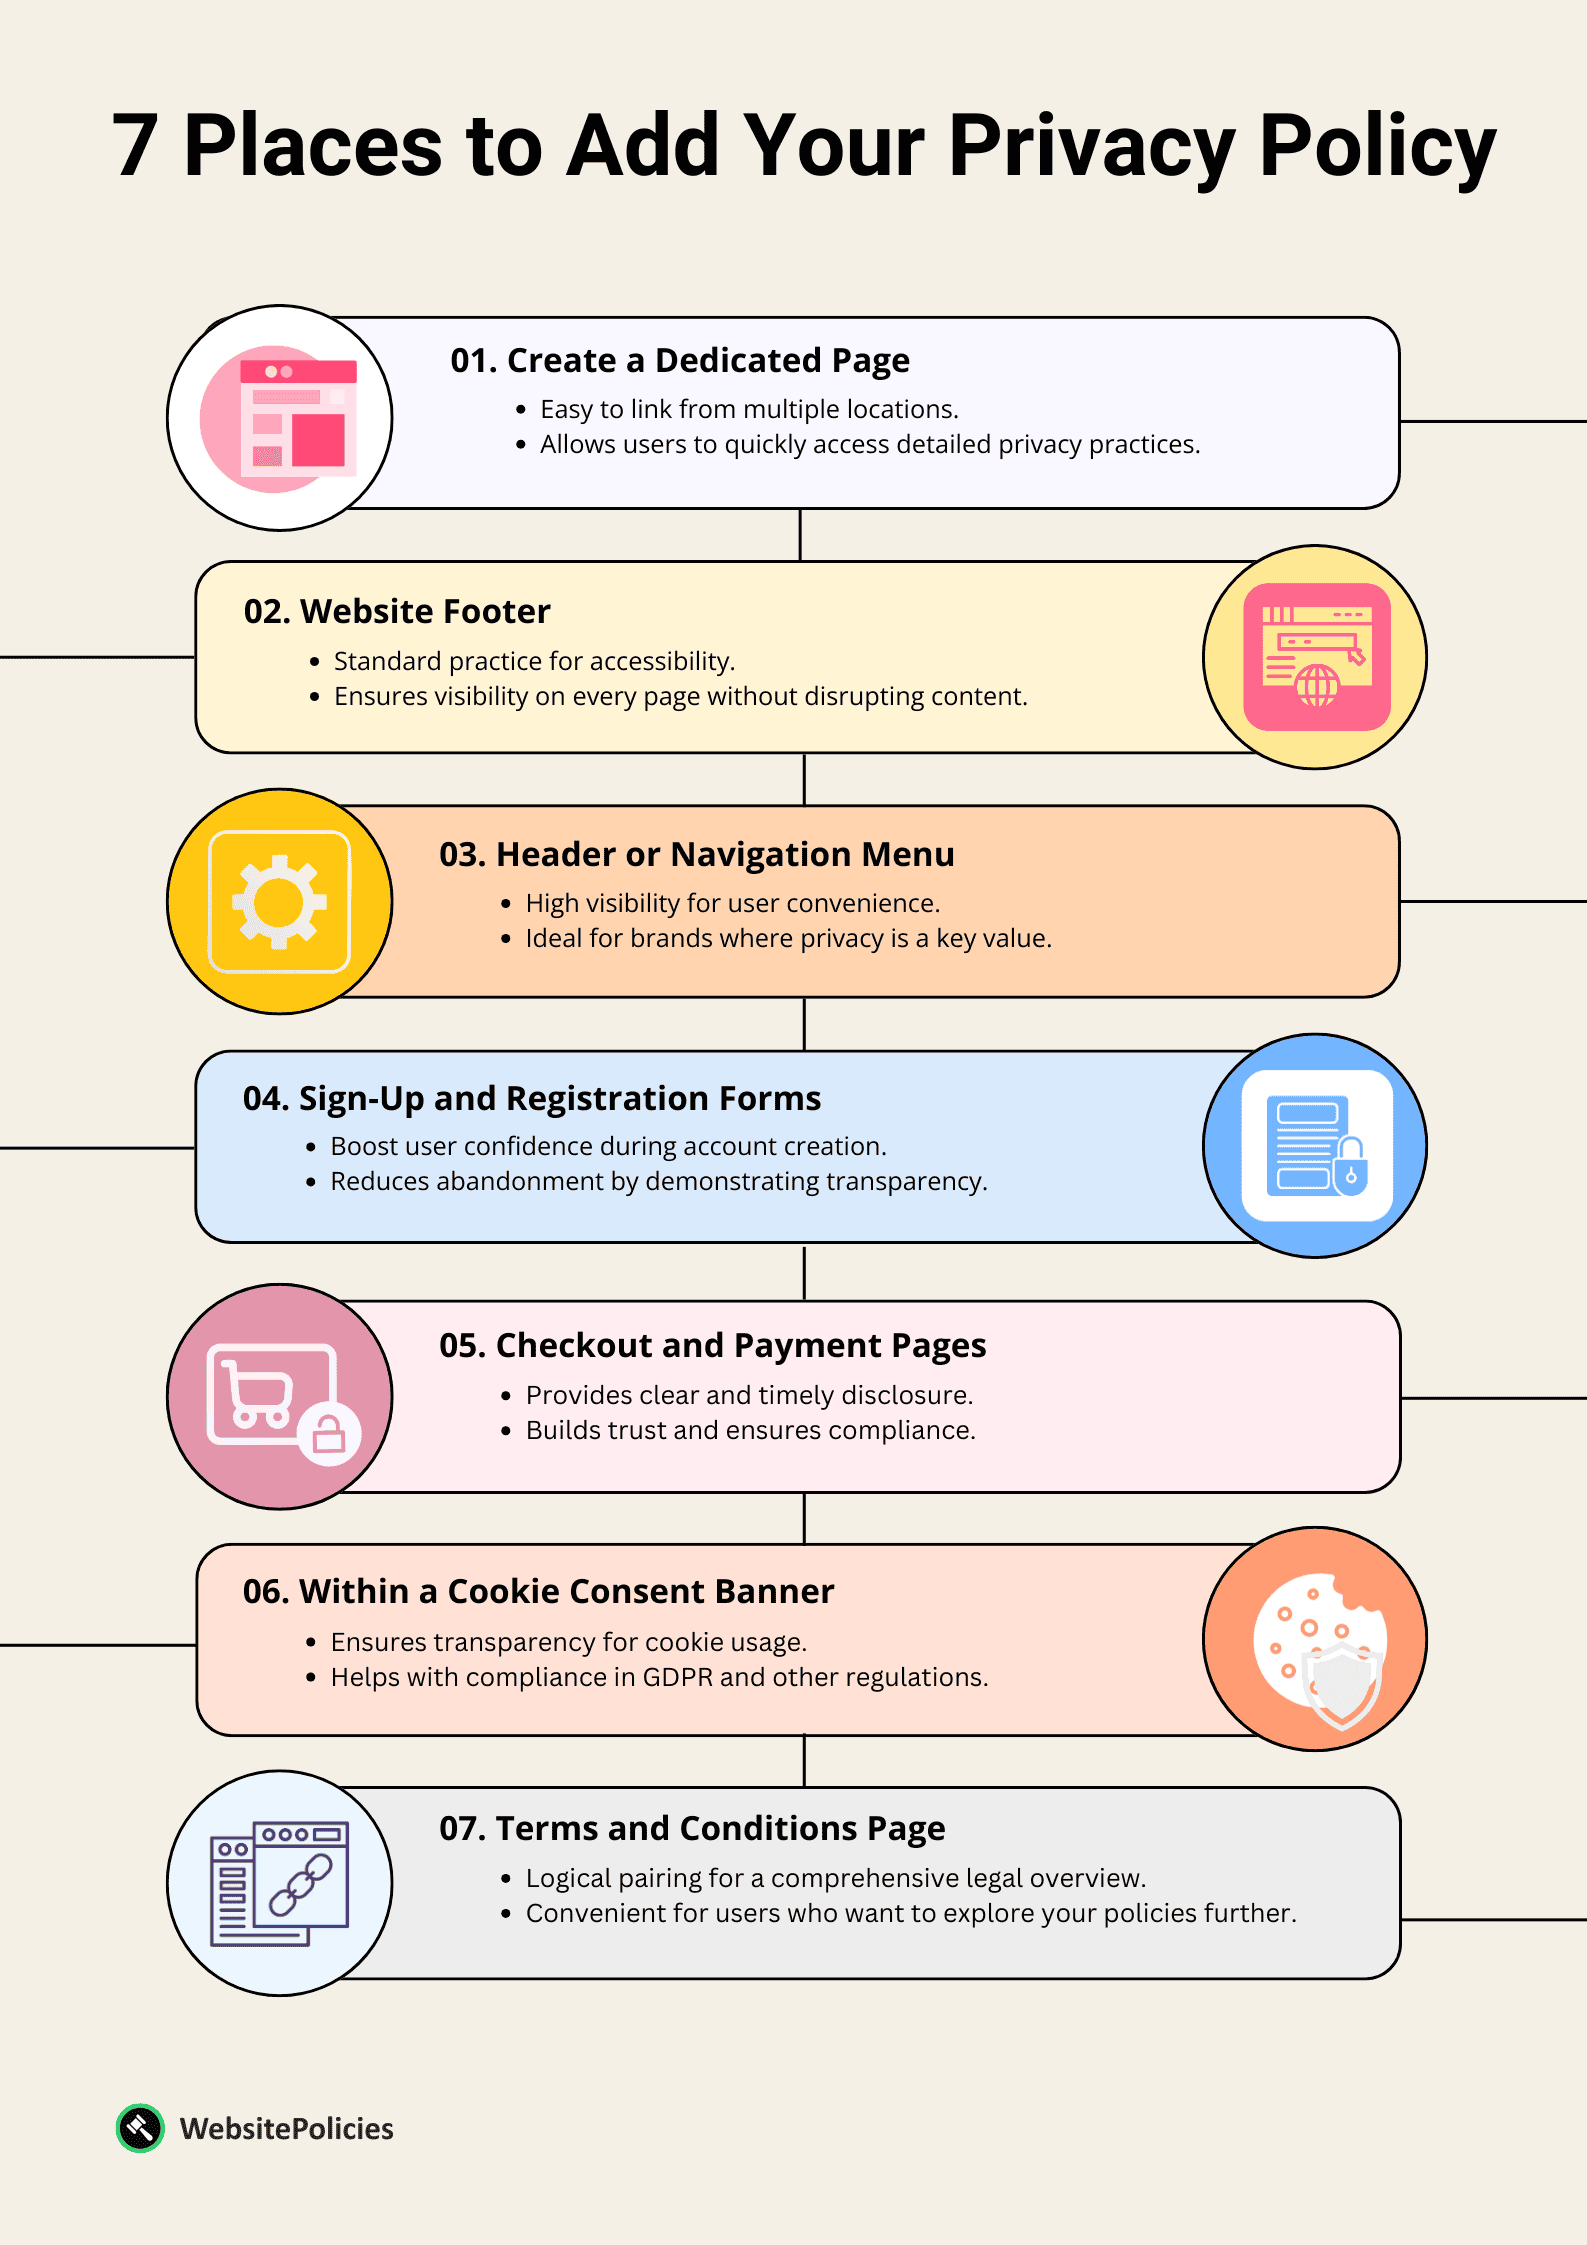
Ultimately, the goal is to balance legal bulletproofing with human readability while you create a privacy policy for your website. By following a structured approach, you build a foundation of trust and legal compliance. Start with a clear audit, use the right tools, and keep it updated. Users respect transparency, and the law demands nothing less.