Secure authentication is the backbone of modern applications, and JSON Web Tokens (JWT) have become a go-to solution for handling it. But here's the thing — the security of your entire JWT implementation hinges on one critical element: the secret key. If that key is weak or improperly generated, attackers can forge tokens and bypass your entire authentication layer. That's why understanding JWT secret key generation in Java isn't just a technical detail; it's a fundamental security practice every developer needs to master.
Understanding JWT Secret Keys
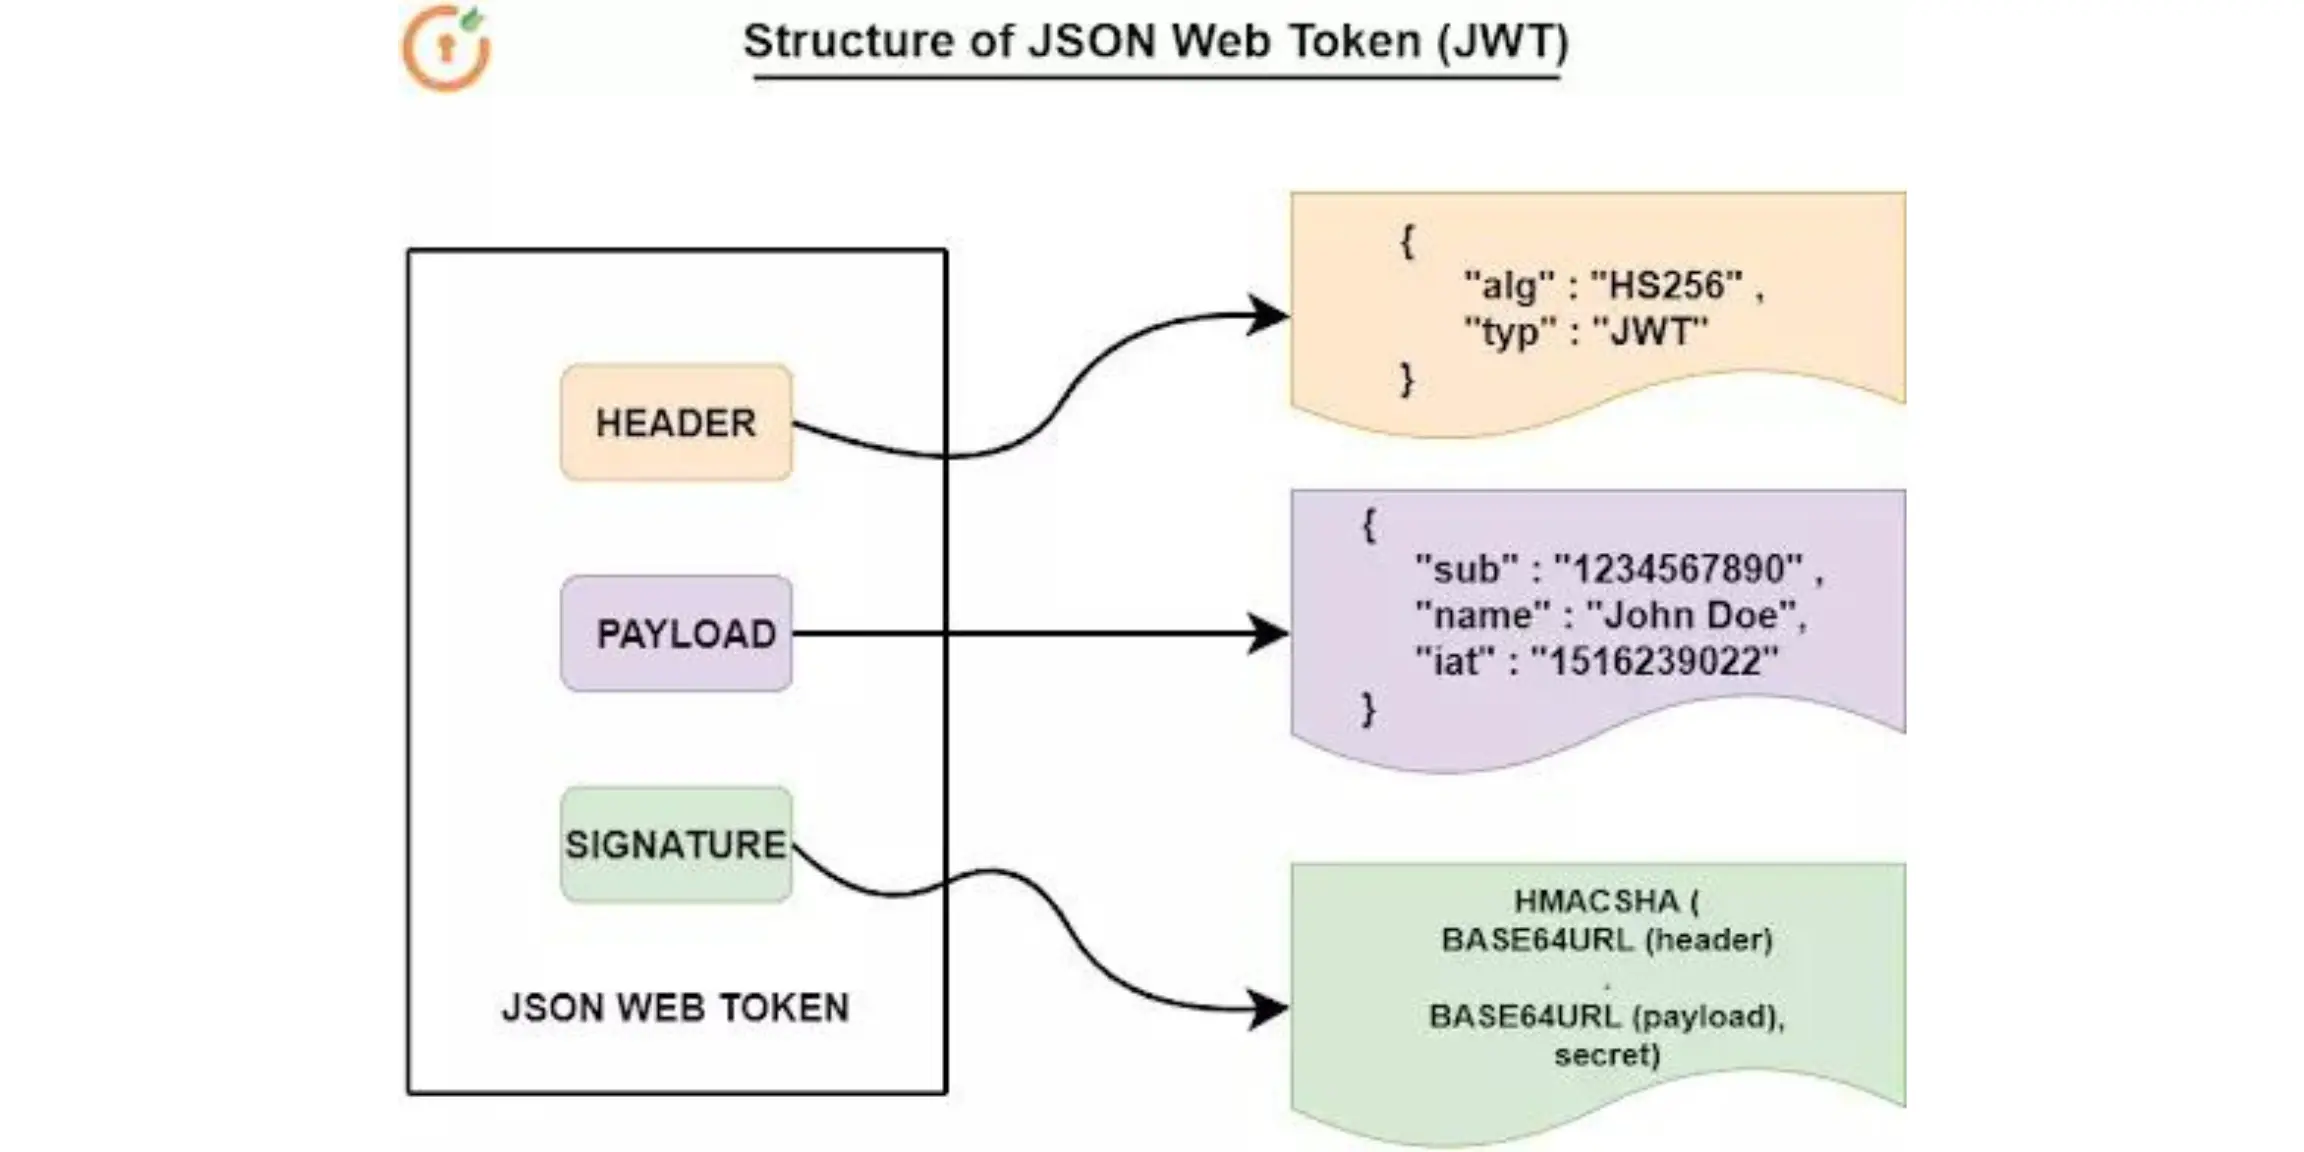
A JWT secret key is a cryptographic key used to sign and verify JWTs. When you create a JWT, the secret key generates a digital signature embedded within the token. When another service receives that JWT, it uses the same secret key to verify the signature's authenticity. In symmetric algorithms like HS256, the same key does both jobs — signing and verifying. The strength of your key directly determines how easy or difficult it is for an attacker to crack your security.
Your secret key should be random, long, and unpredictable. A short, static key (especially if hardcoded in source code) is vulnerable to brute-force attacks, even against simple JWT-cracking tools available on the internet. That makes generating strong keys essential from day one of development.

Generating a Secure Secret Key in Java using jjwt Library
The jjwt library for Java makes generating secure secret keys straightforward.
Here's a simple example for generating a secret key suitable for HS256:
SecretKey key = Jwts.SIG.HS256().key().build();This generates a cryptographically strong, random key.
Generating Keys for HS384, HS512, and Other Algorithms
For stronger algorithms, generating an appropriate-length key is important.
SecretKey key512 = Jwts.SIG.HS512().key().build();Using at least HS256 (256-bit key) is the minimum recommendation. HS512 is preferred for higher-security contexts, though it has marginal performance impact. The jjwt library handles key generation for each algorithm correctly, so developers don't need to manually handle key lengths.
Manually Generating a Secret Key with KeyGenerator
If you need a SecretKey directly, Java's KeyGenerator class can generate one.
KeyGenerator keyGen = KeyGenerator.getInstance("HmacSHA256");
keyGen.init(256);
SecretKey secretKey = keyGen.generateKey();
// SecureRandom can be explicitly specified for stronger randomness
SecureRandom secureRandom = SecureRandom.getInstanceStrong();
keyGen.init(256, secureRandom);
SecretKey secretKey = keyGen.generateKey();HmacSHA256 is the correct algorithm name for HS256 JWTs, despite the naming difference.
Key Length Best Practices
Key length minimums are crucial. The following table summarizes minimum key sizes for each algorithm.
| Algorithm | Minimum Key Size | Recommended |
|---|---|---|
| HS256 | 256 bits (32 bytes) | 256 bits |
| HS384 | 384 bits (48 bytes) | 384 bits |
| HS512 | 512 bits (64 bytes) | 512 bits |
Using a key shorter than the algorithm's requirement results in errors or weakened security. Always meet or exceed these minimums.
Loading a Secret from a String
Sometimes applications store secrets as strings and need conversion to SecretKey objects.
String secretString = "your-256-bit-secret-string-here-at-least-32-bytes!";
SecretKey key = Keys.hmacShaKeyFor(secretString.getBytes(StandardCharsets.UTF_8));
The Keys.hmacShaKeyFor method safely converts byte arrays into SecretKey objects. However, this approach depends on the provided string being strong enough.
Loading from Environment Variables or Configuration
For secure key management, external storage is recommended.
String jwtSecret = System.getenv("JWT_SECRET");
SecretKey key = Keys.hmacShaKeyFor(jwtSecret.getBytes(StandardCharsets.UTF_8));
This prevents hardcoded secrets in repositories and allows rotation without recompilation. The environment variable itself should be a base64-encoded random string or a sufficiently long, random passphrase.
Generating a Base64-Encoded Secret for Configuration
Generating a secure string for storage in environment variables or configuration files is sometimes needed.
SecureRandom random = new SecureRandom();
byte[] bytes = new byte[64]; // 64 bytes = 512 bits when decoded
random.nextBytes(bytes);
String base64Secret = Base64.getEncoder().encodeToString(bytes);
System.out.println(base64Secret);
64 bytes provide 512 bits — enough for HS512. Base64-encoded output is safe for storage in environment variables. Storing the raw bytes is also an option using key.getEncoded().
Important Considerations for Production
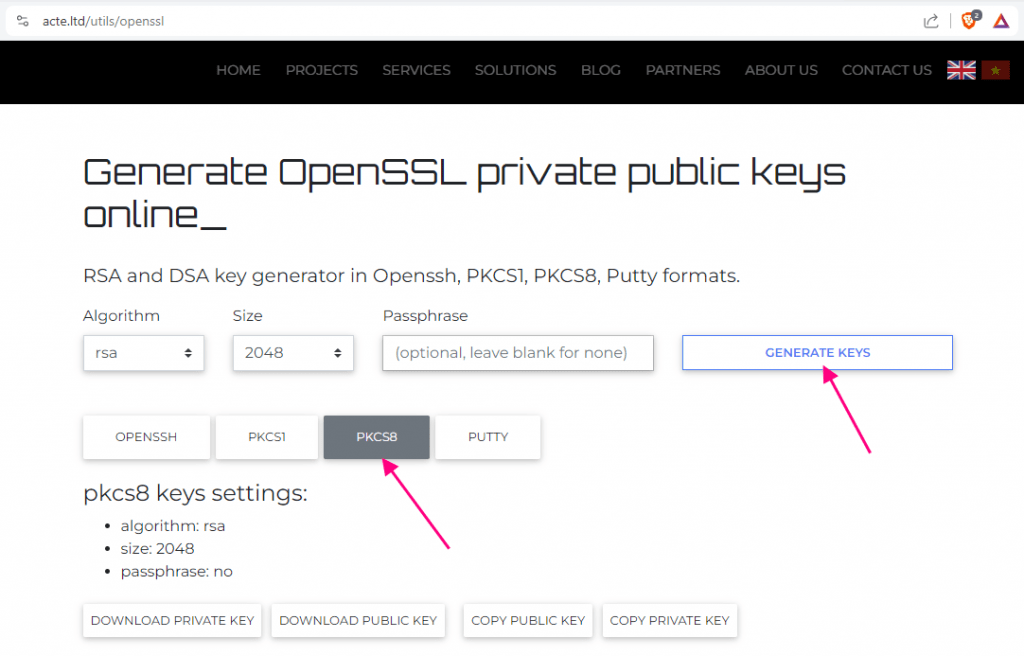
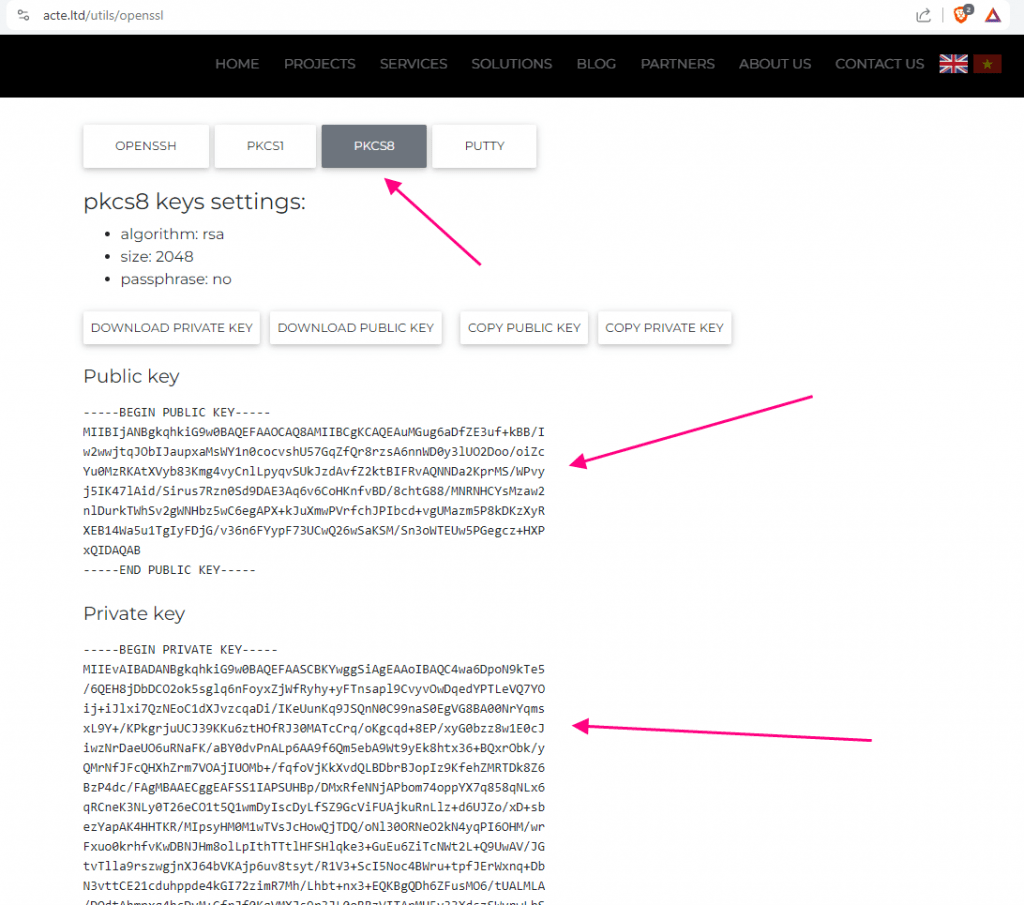
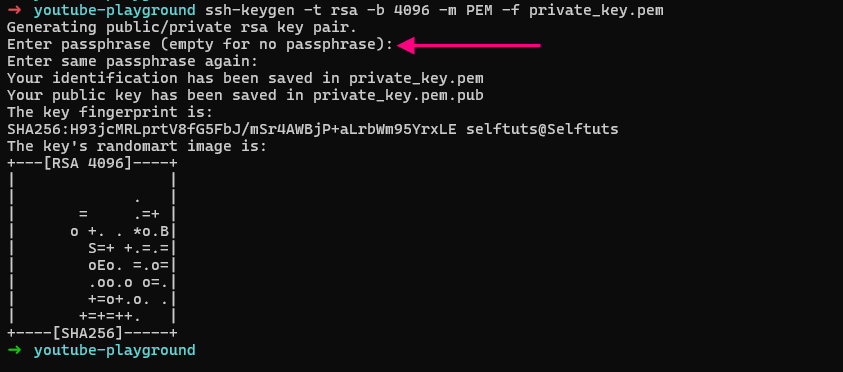
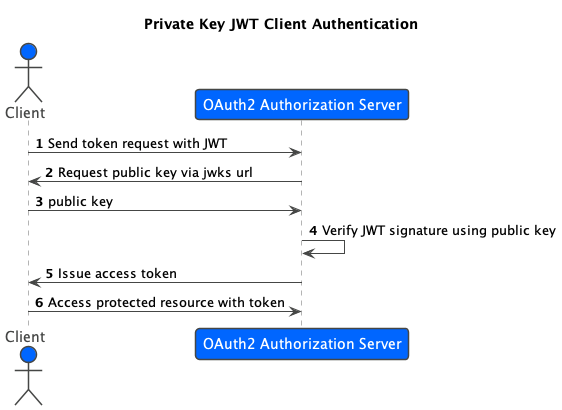
Beyond just generating keys securely, there are several things to keep in mind for production environments. Key rotation is a must — keys should be periodically changed without disrupting active sessions. This requires maintaining multiple keys during rotation periods. Asymmetric algorithms like RS256 are often preferred for distributed systems, where a private key signs tokens and a public key verifies them. Access to the signing key must be strictly limited — systems that only verify tokens should never have access to the signing key.
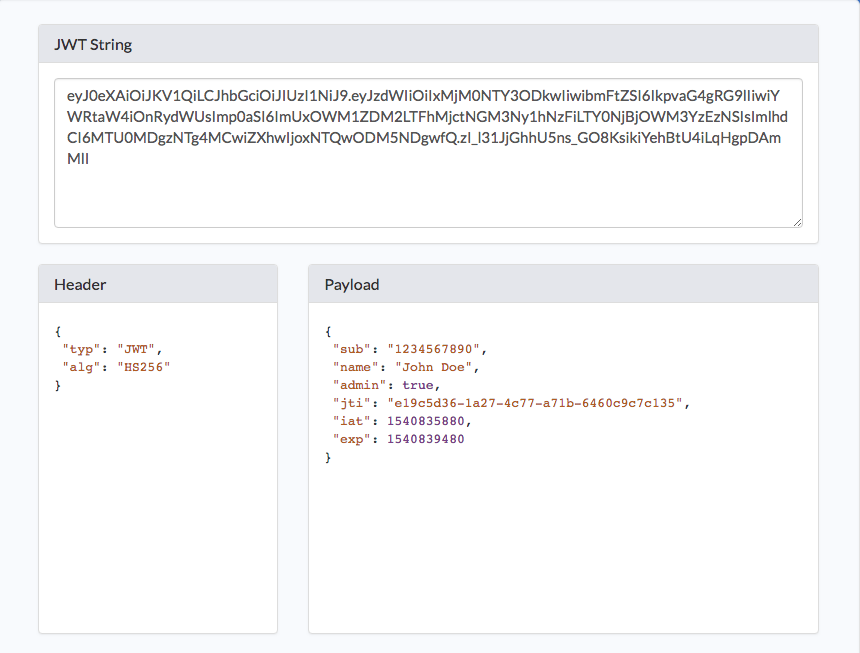
Aside from the jjwt example shown above, Spring Security, Nimbus JOSE + JWT, and Auth0's Java JWT library all provide similar key generation utilities. The critical difference lies in how secrets are managed across services, not necessarily in how they're generated. Regardless of the library, the principles of using sufficiently long, random keys and storing secrets securely outside of source code remain paramount. Test with jwt.io to verify tokens are correctly signed — paste a generated token and its secret to confirm the signature validates. This simple check catches mismatched keys or algorithm errors early in development.