In today's digital landscape, protecting sensitive data as it travels across networks is no longer optional—it's a fundamental requirement. Online string encryption serves as a critical defense mechanism, transforming readable text into unreadable ciphertext that only authorized parties can decipher. Whether you're handling API keys, user credentials, or personal messages, understanding how to implement robust encryption for strings is essential for any developer or security-conscious organization.
Understanding the Core Principles of String Encryption
At its heart, online string encryption relies on cryptographic algorithms to scramble data. The most common approach involves using symmetric encryption, where a single secret key both encrypts and decrypts the information. AES (Advanced Encryption Standard) remains the gold standard for this, offering various key lengths—128-bit, 192-bit, and 256-bit—to balance security needs with performance requirements. When a string is encrypted, it becomes a jumble of characters meaningless to anyone without the corresponding decryption key. This process ensures that even if data is intercepted during transmission, it remains protected from prying eyes.
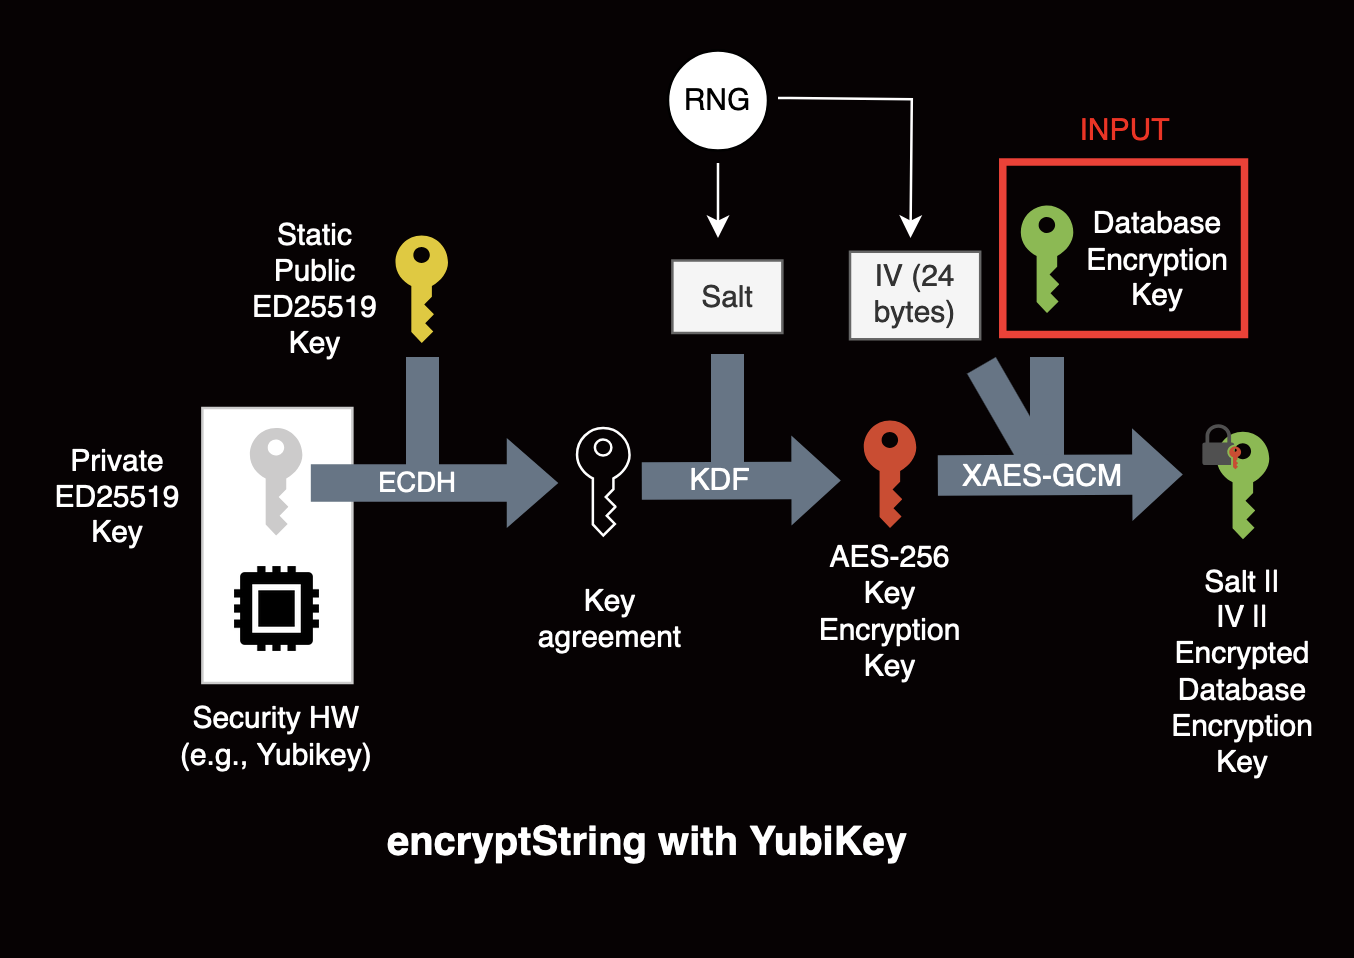
The process typically involves more than just the algorithm itself. Secure encryption requires proper key management and initialization vectors (IVs) to ensure that identical plaintext strings produce different ciphertext each time they're encrypted. This prevents pattern analysis attacks where an attacker might try to deduce the encryption key by observing repeated outputs. Libraries in various programming languages handle much of this complexity, but understanding what happens under the hood helps you make better security decisions and troubleshoot issues effectively.
Common Use Cases for Online String Encryption
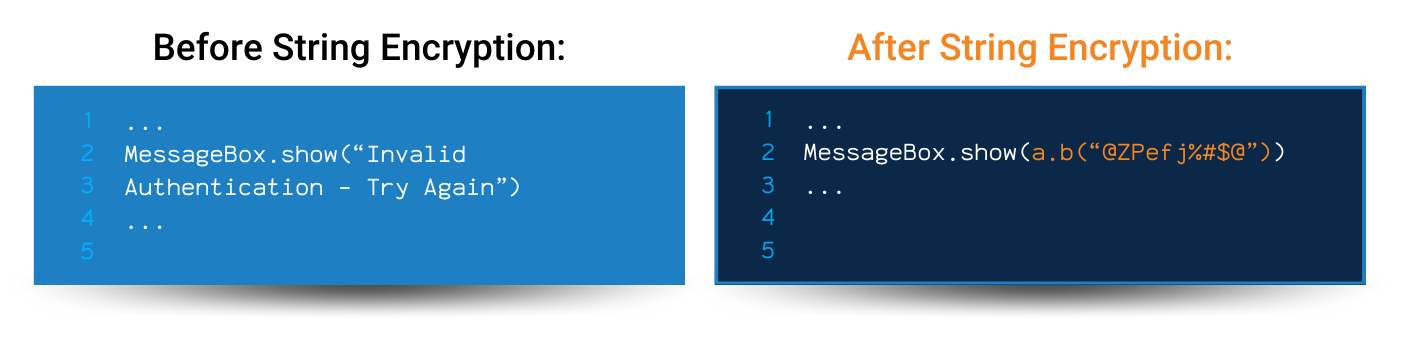
Developers frequently encounter scenarios where string encryption proves indispensable. Web applications routinely encrypt session tokens and API keys stored in environment variables or configuration files rather than hardcoding them directly in source code. This practice protects sensitive information from exposure if the codebase is ever publicly accessible. Similarly, database connections often involve encrypting credentials that travel over networks, preventing man-in-the-middle attacks that could intercept unencrypted login details.
Beyond web development, string encryption plays a vital role in secure messaging applications where end-to-end encryption ensures that only conversation participants can read messages. Password managers rely heavily on string encryption to protect stored credentials. Even simple tasks like encrypting URLs with sensitive query parameters prevent exposure of personal data embedded in web logs. As data privacy regulations like GDPR and CCPA become more stringent, properly encrypting strings becomes not just a best practice but a legal requirement for many organizations handling personal information.
Choosing the Right Encryption Tools
When selecting a tool for online string encryption, prioritize solutions that support strong, standardized cryptographic primitives. Avoid proprietary or obscure algorithms that haven't undergone peer review. Look for tools that handle key derivation securely, using functions like PBKDF2 or Argon2 with sufficient iteration counts to resist brute-force attacks. The tool should support authenticated encryption modes like AES-GCM, which provides both confidentiality and integrity verification through authentication tags.
| Feature | OpenSSL | Libsodium | Age |
|---|---|---|---|
| Algorithms | Wide variety of legacy and modern | Modern, opinionated defaults | Modern, focused on file/string |
| Ease of Use | Command line focused, moderate | Very easy, hard to misuse | Very easy, key management built-in |
| Performance | Highly optimized C | Highly optimized | Good, focused on simplicity |
| Best For | System-level tasks, legacy support | Web apps, modern applications | Simple file/string encryption |
OWASP maintains a comprehensive list of recommended cryptographic practices and tools that serve as excellent references when evaluating options. Remember that the most secure tool is one you can implement correctly—complexity often introduces vulnerabilities through misuse. Always prefer libraries that make the secure choice the default choice.
Implementation Pitfalls to Avoid
Even with the right tools, implementation mistakes can completely undermine your encryption efforts. One of the most common pitfalls is hardcoding encryption keys directly in your source code, which exposes them if the code is ever shared or leaked. Another frequent error is using weak key derivation functions with insufficient iteration counts, making encrypted strings vulnerable to offline brute-force attacks. Reusing initialization vectors or nonces with the same key compromises the security of your encryption entirely.
- Never hardcode keys in source code; use secure key management services or environment variables
- Always use cryptographically secure random number generators for generating IVs and nonces
- Ensure you're using authenticated encryption modes to detect tampering
- Keep your cryptographic libraries updated to patch vulnerabilities
- Be cautious with encoding—UTF-8 handling can sometimes cause issues if not consistent
Testing your encryption implementation with known test vectors helps catch logical errors early. Conduct regular security audits and penetration testing to identify potential vulnerabilities before attackers do. Remember that cryptography is notoriously difficult to implement correctly—subtle mistakes can have catastrophic consequences for data security.
The Future of String Encryption
The field of cryptography evolves continuously, with researchers developing new algorithms and attacking existing ones. Quantum computing poses a significant future threat to current public-key cryptosystems like RSA and ECC, prompting the development of post-quantum cryptography standards. NIST has been leading efforts to standardize algorithms that will resist quantum attacks, and these will eventually impact how we encrypt strings online.
Today, investing in properly implemented string encryption protects against current threats while establishing practices that will ease transitions to future standards. The fundamentals of using strong algorithms, managing keys securely, and implementing authenticated encryption remain constant even as specific algorithms evolve. Stay informed about developments in the cryptographic community, participate in security audits, and always prioritize defense in depth—never rely solely on encryption as your only security measure.
Online string encryption stands as a non-negotiable component of modern software development. By understanding the principles, choosing appropriate tools, avoiding common pitfalls, and keeping an eye on the future, you can ensure that sensitive data remains protected throughout its journey across the internet. Start implementing robust encryption practices today—your users' data security depends on it.