Managing open files is a routine task for Linux system administrators. When multiple users access files simultaneously, tracking who opened which file becomes essential for troubleshooting performance issues, resolving "too many open files" errors, and ensuring security compliance. Linux provides powerful built-in commands to monitor and analyze open files by user, helping maintain system stability and efficiency.
Understanding Open Files in Linux
Every time a process starts, it opens files—whether reading configuration files, writing logs, or handling network connections. Each open file consumes a file descriptor, and there's a limit on how many a single process or the entire system can have open at once. When that limit is exceeded, applications may crash or behave unexpectedly.
To investigate which user has which files open, the lsof command is your primary tool. It stands for "list open files," and it reveals detailed information about files opened by processes, including their associated users, process IDs, file types, and access modes.
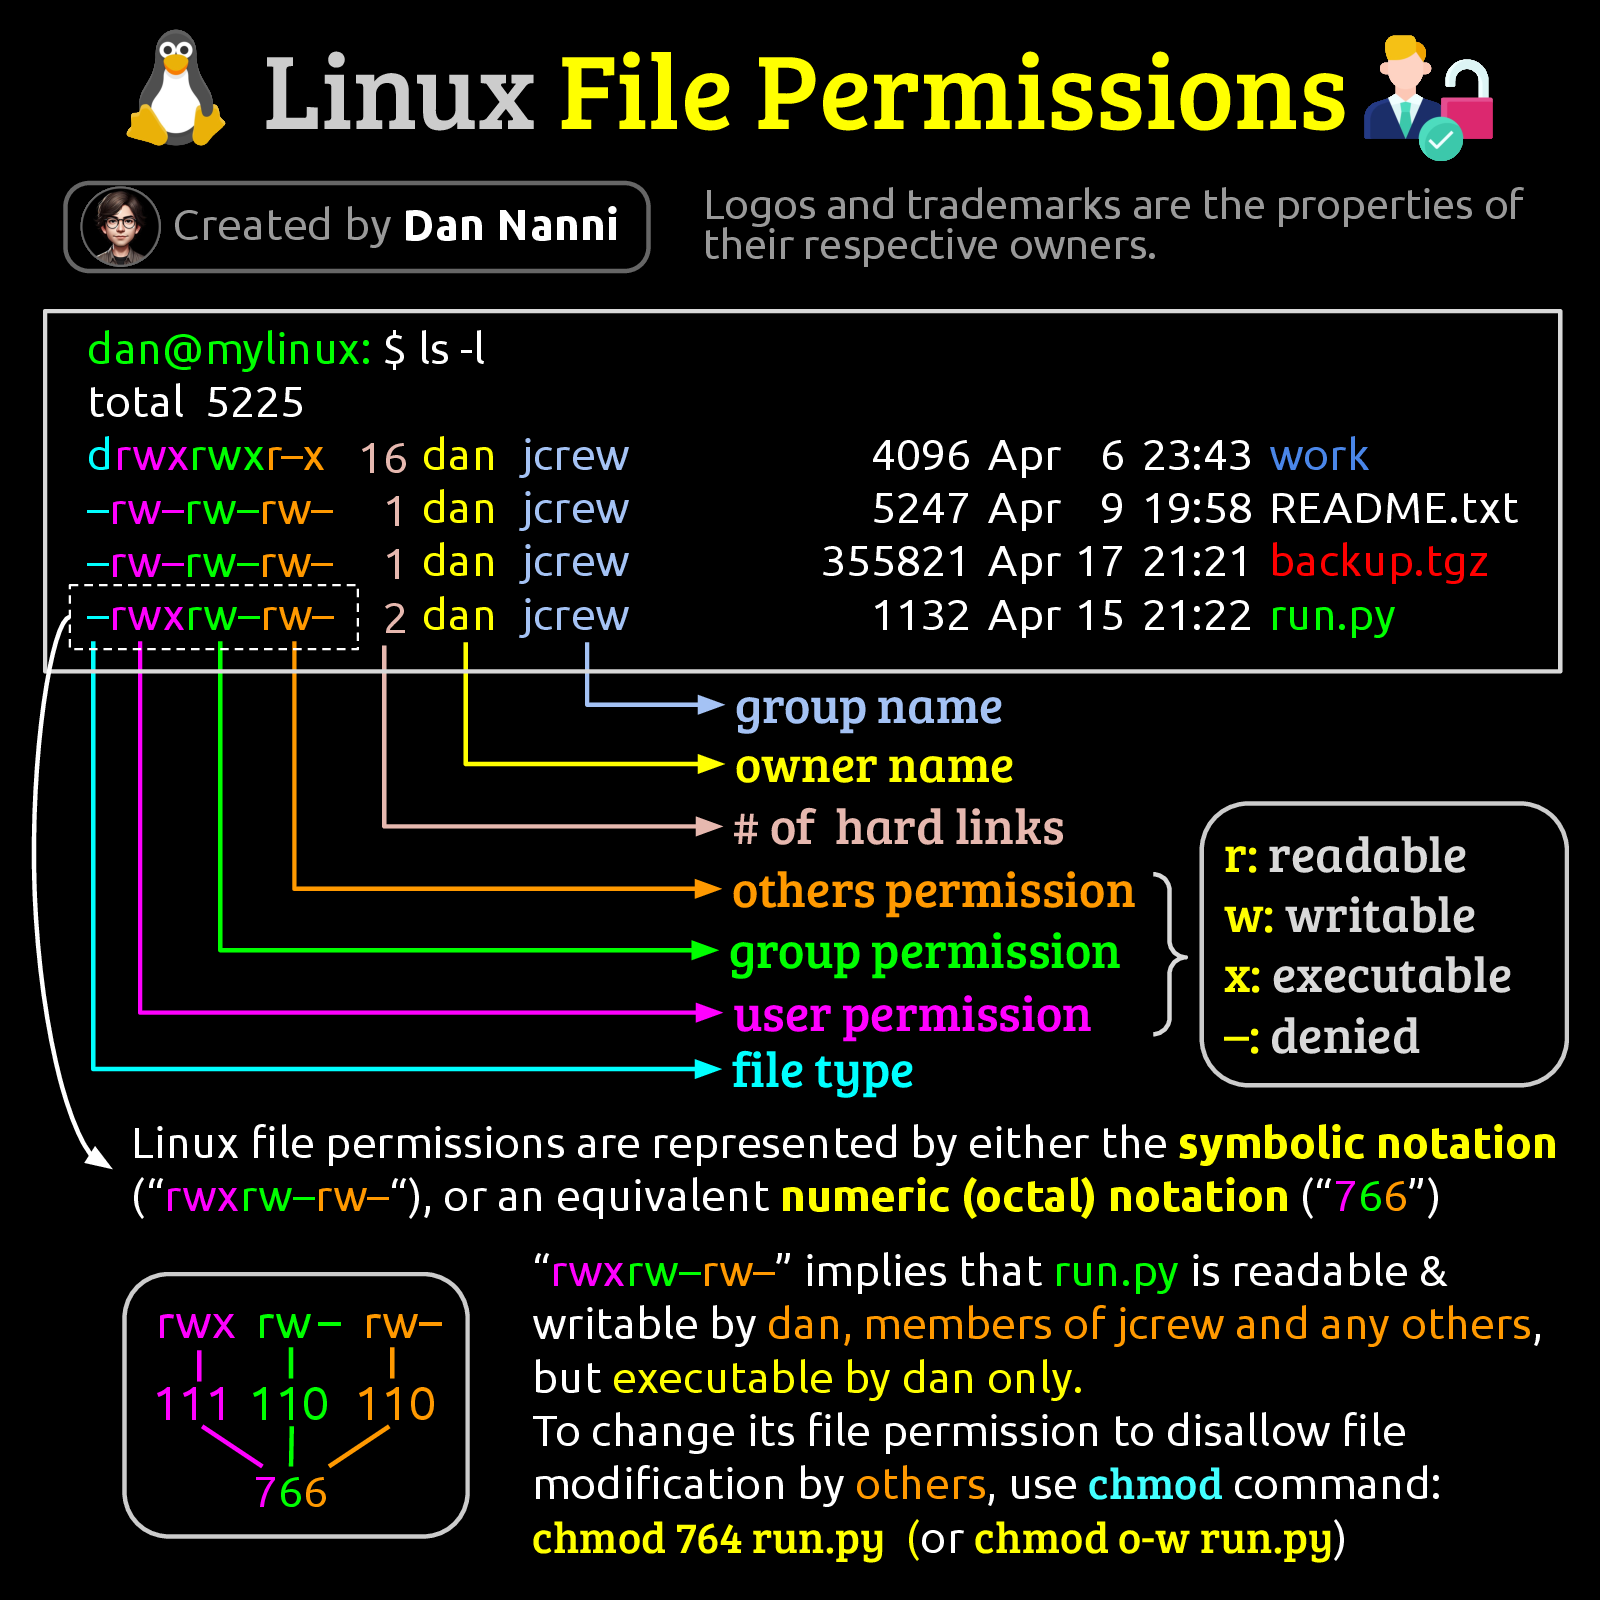
Basic Command Structure
The simplest way to list open files by user using lsof is:
lsof -u username– Shows all files opened by a specific user.lsof -u ^username– Shows files opened by everyone except a specific user.
Filtering by User with lsof
Beyond basic filtering, you can combine lsof with other flags to narrow your search:
lsof -u username +D /path– Shows open files by user within a specific directory tree.lsof -u username -t– Returns only process IDs for scripting purposes.
Combining with Other Tools
For deeper analysis, combine lsof with awk or grep to extract only relevant fields:

lsof -u username | awk '{print $2, $9}'Managing System-Wide Limits
System administrators often encounter "too many open files" errors. To check current limits per user, use:
ulimit -n– Shows the per-process limit for the current shell.cat /proc/sys/fs/file-max– Reveals the system-wide limit.lsof -u username | wc -l– Counts all open files by user.
Alternative Commands: fuser and /proc filesystem
Besides lsof, you can also use fuser:
fuser -v /path– Shows which users have a specific file open.
The /proc filesystem provides raw data about process details:
ls -l /proc/[PID]/fd/– Shows file descriptors for a process.
Security and Auditing Considerations
Monitoring open files by user is also crucial for security auditing. Suspicious files opened by unexpected users can indicate a breach. Use lsof in combination with auditd for comprehensive monitoring.
Summary Table: Common lsof flags for user-based queries
| Flag | Description |
|---|---|
-u username |
Show files opened by user |
-u ^username |
Show files opened by others |
+D /path |
Show files open in directory tree |
-t |
List only PIDs |
Conclusion
Mastering the tools described above—especially lsof, fuser, and the /proc filesystem—empowers administrators to efficiently monitor, troubleshoot, and secure Linux systems by user. Regular audits of open file usage contribute significantly to maintaining system health and robust security practices.