Caller ID spoofing is a deceptive practice where the identity displayed on a recipient's phone is deliberately falsified to appear as if it originates from a different number or location. This manipulation exploits the signaling protocols used in telephony, specifically the Session Initiation Protocol (SIP) and the legacy SS7 network, allowing attackers to inject fake caller ID information at the network level. While often associated with malicious intent, understanding the technical mechanics is crucial for both security professionals and the general public to recognize and mitigate potential threats.
The Technical Mechanics of Spoofing
At its core, caller ID spoofing works by exploiting the way telephone networks transmit origin information. Traditional landline calls traverse the SS7 network, a global system that directs calls based on signaling data separate from the audio channel. Because this system was designed decades ago with a focus on reliability rather than security, it inherently trusts the legitimacy of the number sent by the originating switch. An attacker with access to specific signaling tools or a compromised connection can inject a fraudulent "Calling Line Identification" (CLID) packet, replacing the true origin with a number of their choosing, such as a local bank or a government agency.
Voice over IP (VoIP) Exploitation
Modern spoofing has evolved significantly with the prevalence of Voice over IP (VoIP) technology. VoIP converts voice into data packets, which travel over the internet rather than dedicated telephone lines. This digital pathway introduces specific vulnerabilities that spoofers leverage using Session Initiation Protocol (SIP) headers. When a SIP request is sent to initiate a call, it contains a "From" field that dictates what the recipient sees. By using open-source software or commercial spoofing services, a user can easily configure this field to display any arbitrary number, bypassing the traditional carrier validation checks that exist for PSTN calls.
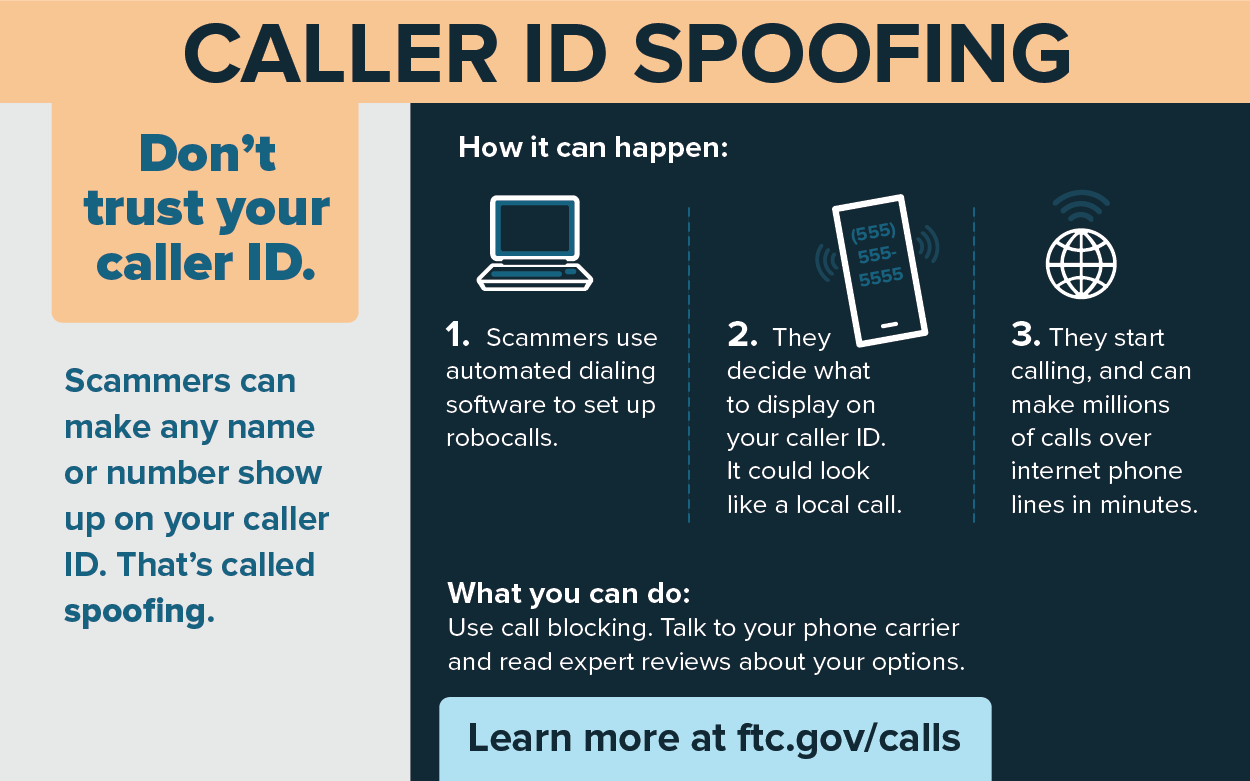
- Exploiting SIP INVITE messages to manipulate display names and numbers.
- Utilizing international premium rate numbers to generate high call volumes.
- Leveraging callback mechanisms that display the spoofed number on the recipient's screen.
- Abusing residential proxies to mask the true geographical origin of the call.
Motivations and Real-World Applications
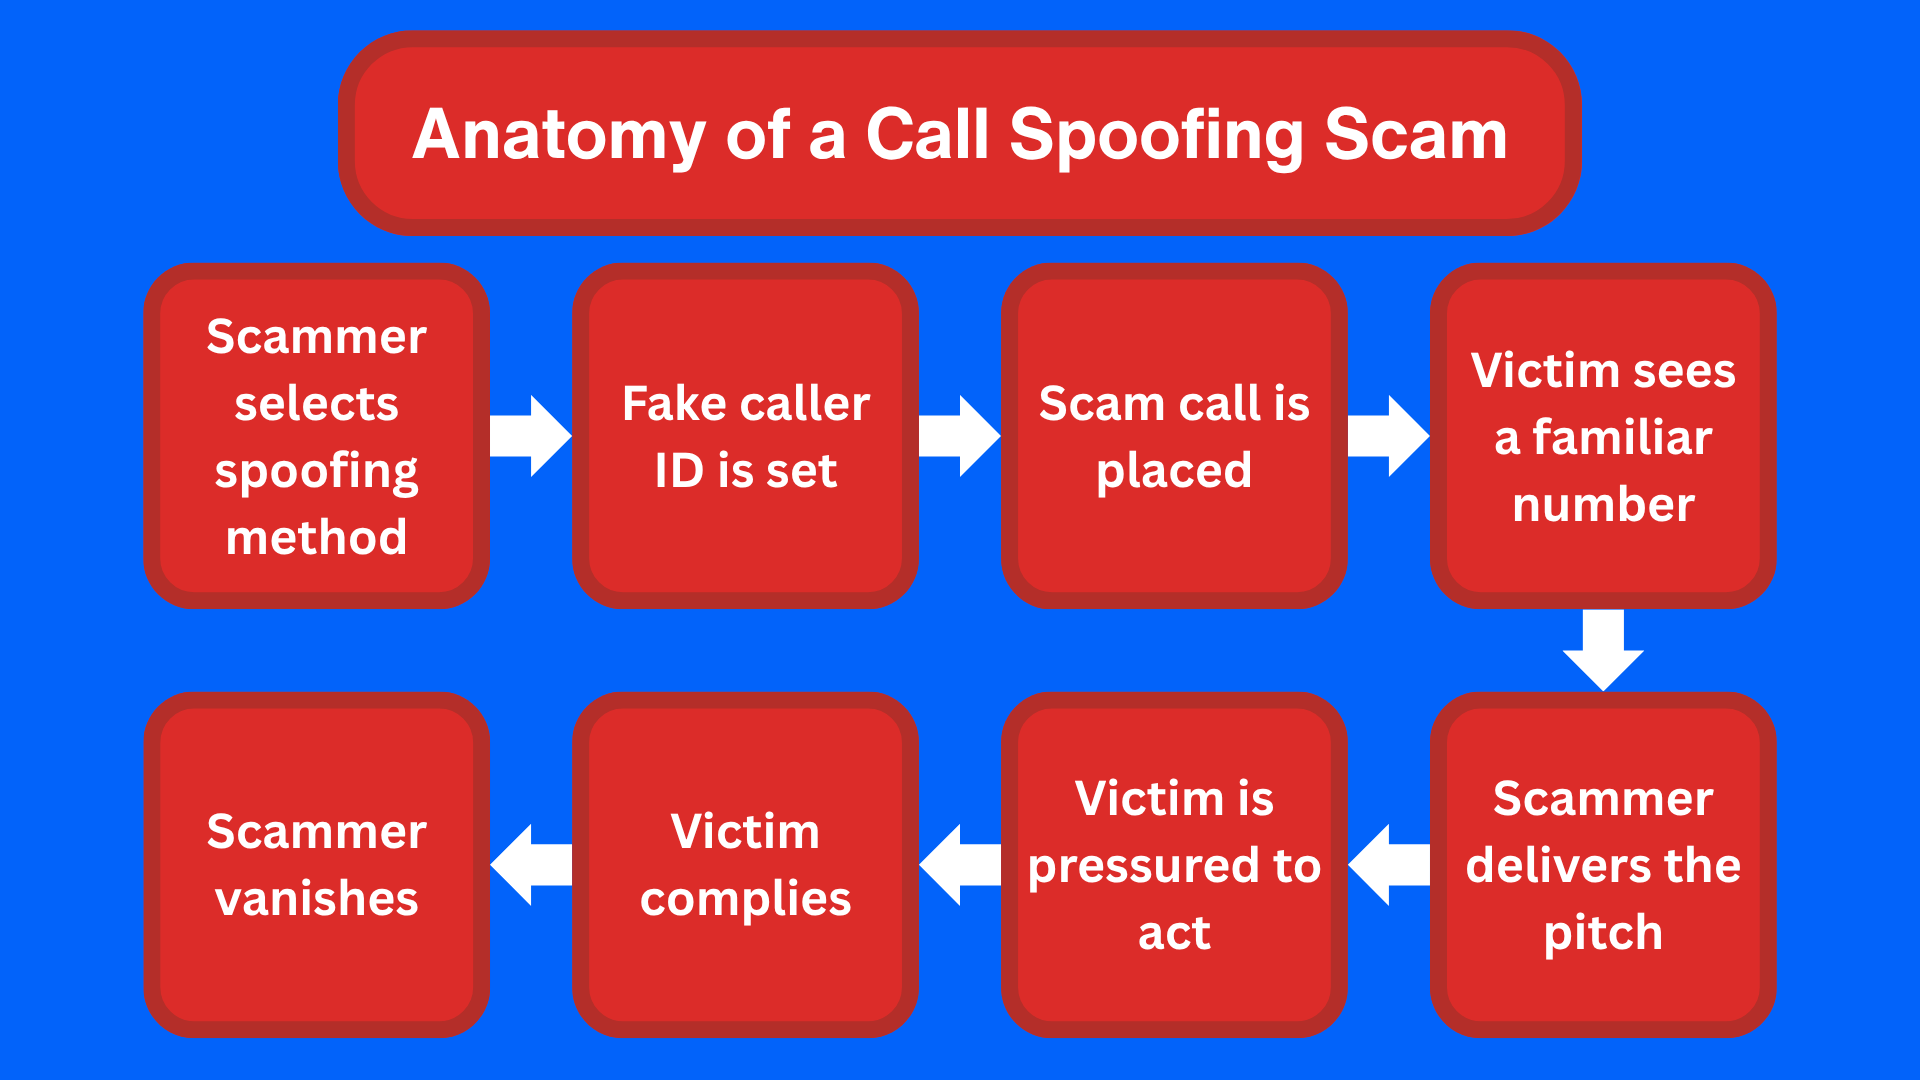
The reasons behind caller ID spoofing are varied, ranging from pranks to sophisticated financial fraud. Scammers frequently spoof local area codes to increase the likelihood of their targets answering the phone, as individuals are statistically more likely to respond to familiar numbers. In tech support scams, the displayed ID might mimic a major corporation like Microsoft or Apple, creating a false sense of legitimacy to trick victims into granting remote access to their computers or paying for non-existent services.
The Impact on Financial Institutions
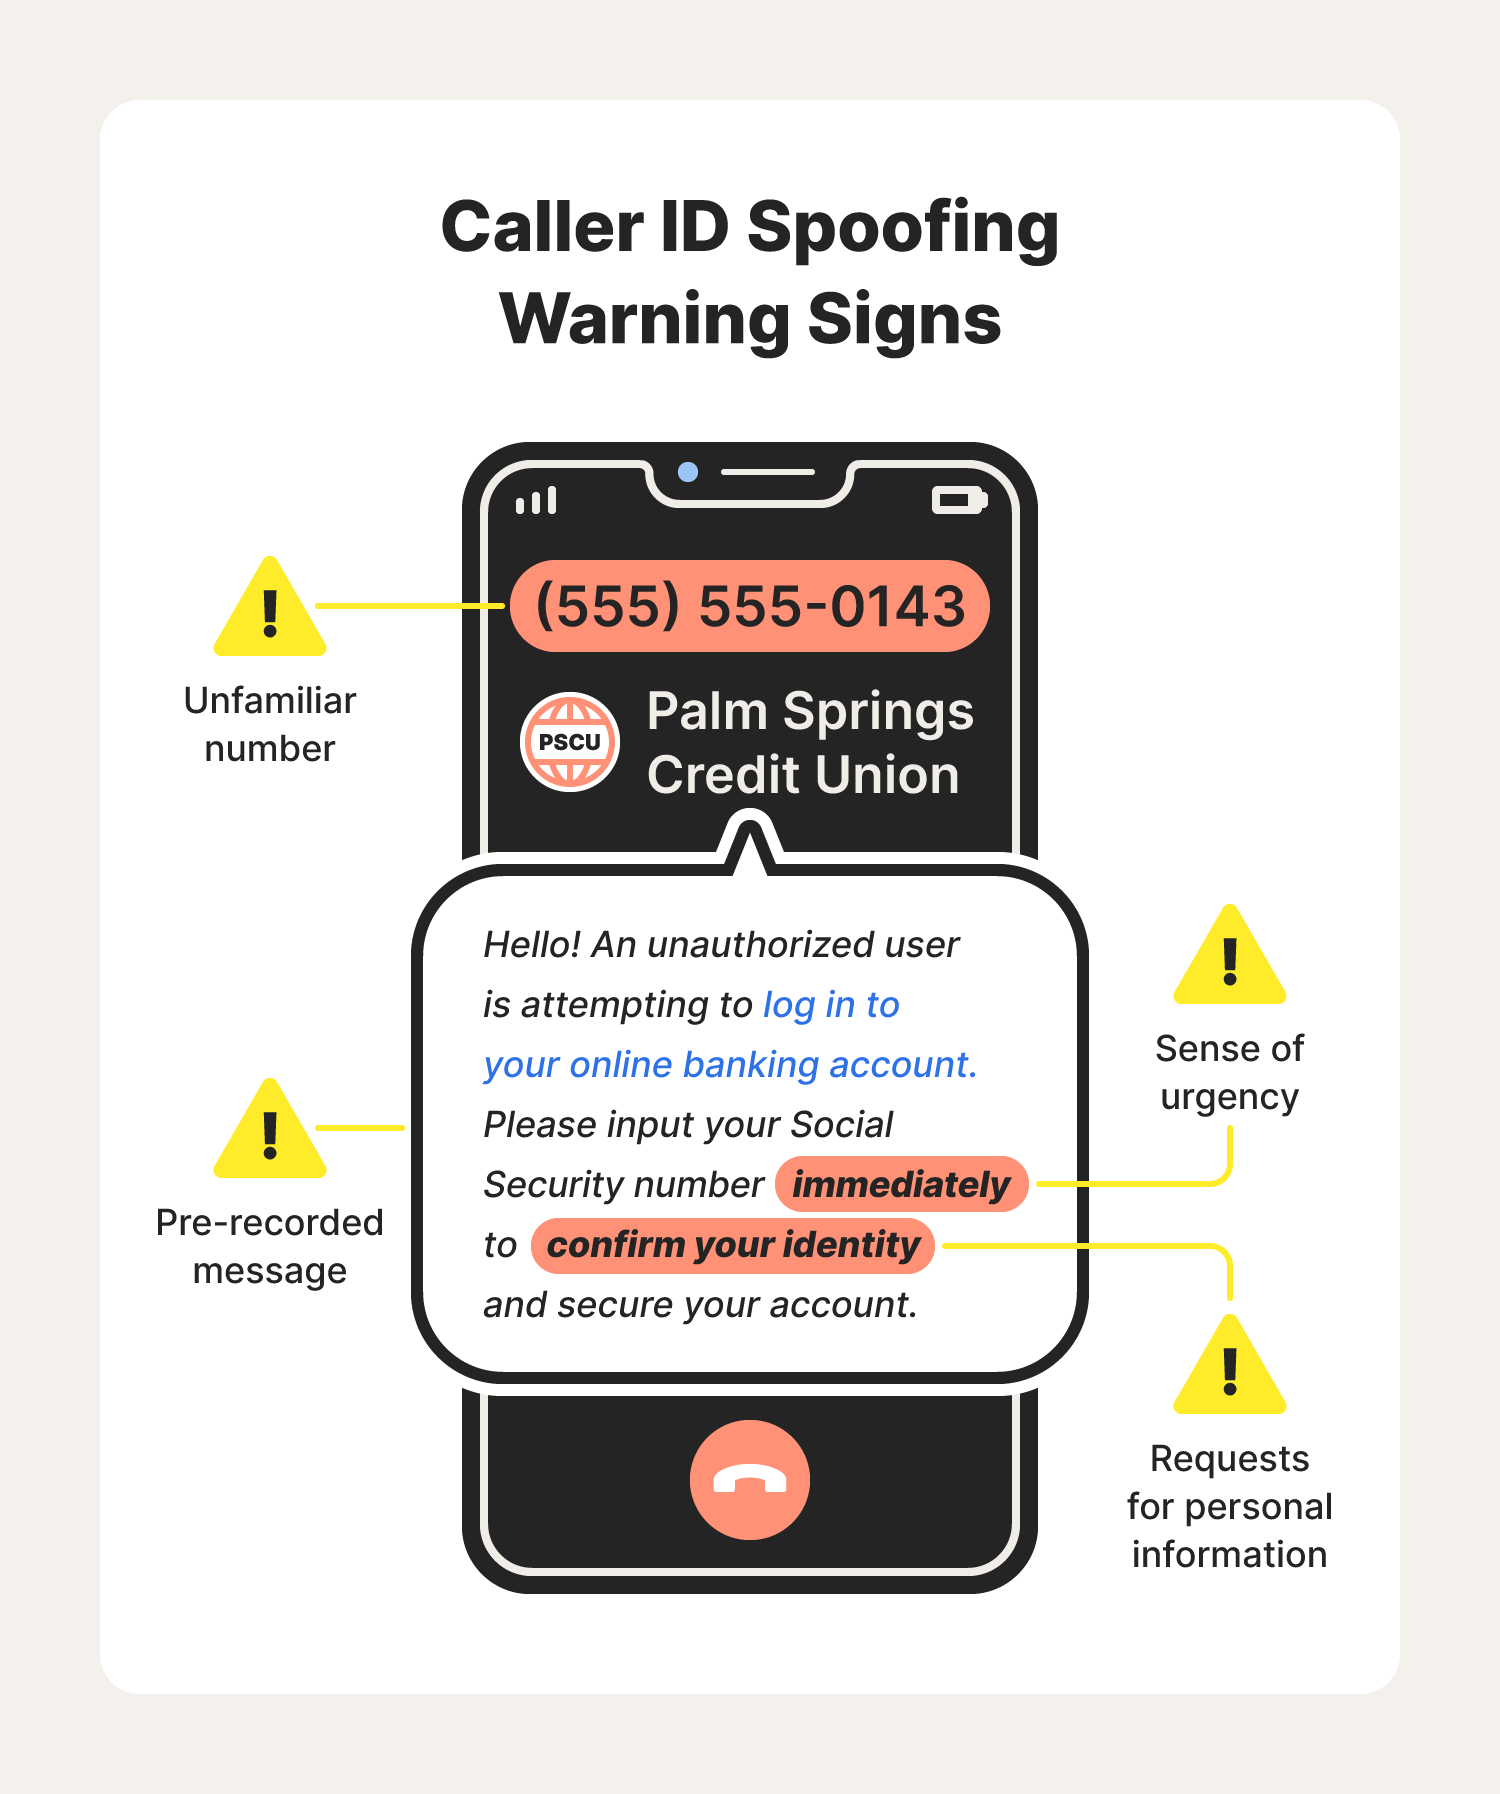
Financial institutions are particularly vulnerable to targeted spoofing attacks. Fraudsters may display the main number of a bank on the recipient's caller ID to create a sense of urgency regarding a compromised account. When the victim calls back the number they see, they are connected not to the bank, but to the criminal, who then "verifies" the information to gain access to accounts. This vishing (voice phishing) technique relies entirely on the perceived authenticity of the displayed caller ID to bypass skepticism.
Technically, the execution involves obtaining outbound calling trunks that support customized CLI. While legitimate businesses use this feature for legitimate purposes—such as displaying a main corporate number rather than an individual agent's direct line—malicious actors acquire these services from less regulated markets on the dark web. The process often involves minimal verification, allowing bad actors to purchase the ability to spoof any number they desire for a nominal fee per call.
Legal and Technical Countermeasures
Governments and telecommunications bodies have recognized the dangers of this technology, leading to legislative efforts to curb its abuse. In the United States, the Truth in Caller ID Act of 2009 makes it illegal to transmit misleading caller ID information with the intent to defraud, cause harm, or gain anything of value. However, enforcement remains challenging due to the global nature of the internet, as many spoofing services operate from jurisdictions with lax regulations.
On the technical front, the industry is moving toward a protocol framework known as "Secure Telephone Identity Revisited" (STIR) and "SHAKEN" (Secure Handling of Asserted information using toKENs). This system cryptographically signs caller ID information at the source, allowing downstream carriers to verify the authenticity of the number. As this digital certificate infrastructure rolls out, it will become significantly harder for spoobers to manipulate caller ID without being detected by the network.
Caller ID Spoofing Infographic | Consumer Advice
Call Spoofing: What It Is and How to Avoid It
What Is Caller ID Spoofing? Definition, Prevention & More!
What Is Spoofing? | Definition, examples & Prevention Tips

What Is Caller ID Spoofing and How Does It Work?
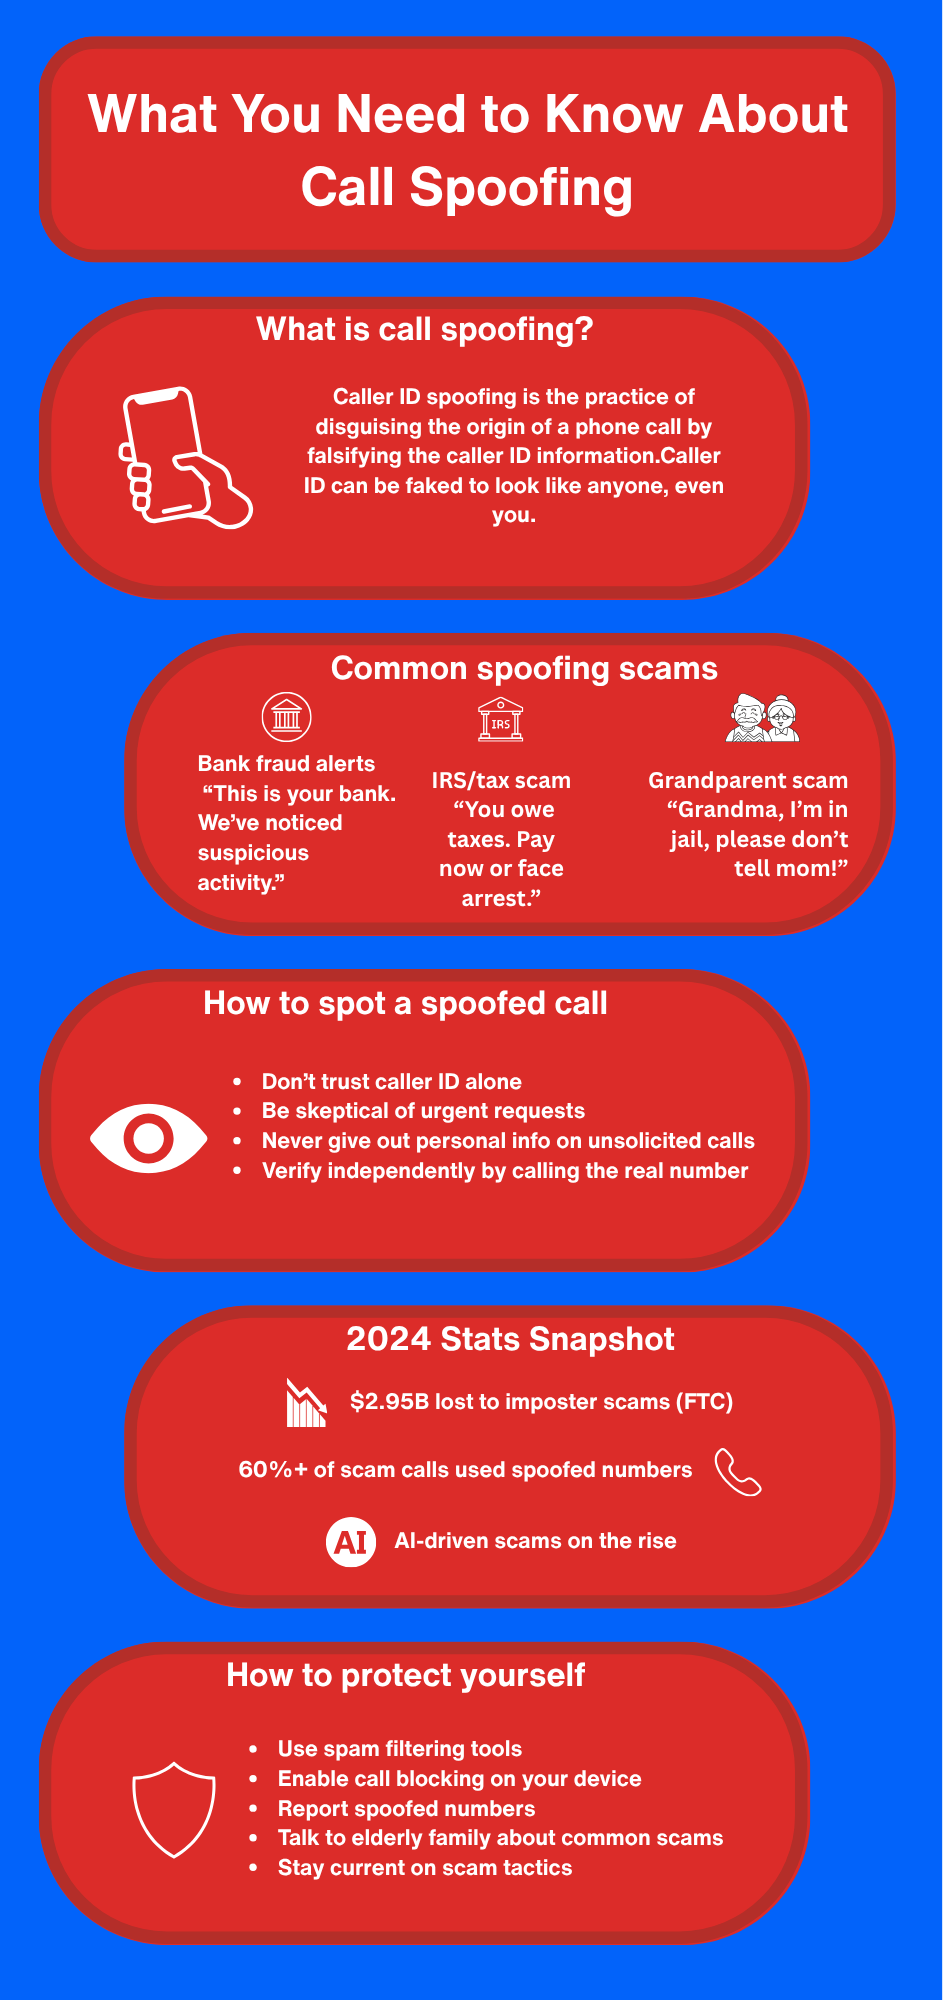
Call Spoofing: What It Is and How to Avoid It
What Is Caller ID Spoofing? How To Protect Yourself

Caller ID Spoofing: What It Is & How To Stop It
/img_01.png?width=1050&name=img_01.png)
What is Caller ID Spoofing? How to Prevent and Stop it?
/img_02.png?width=700&name=img_02.png)
What is Caller ID Spoofing? How to Prevent and Stop it?

How Does Caller ID Spoofing Work on Landlines, and How Can I Protect M.
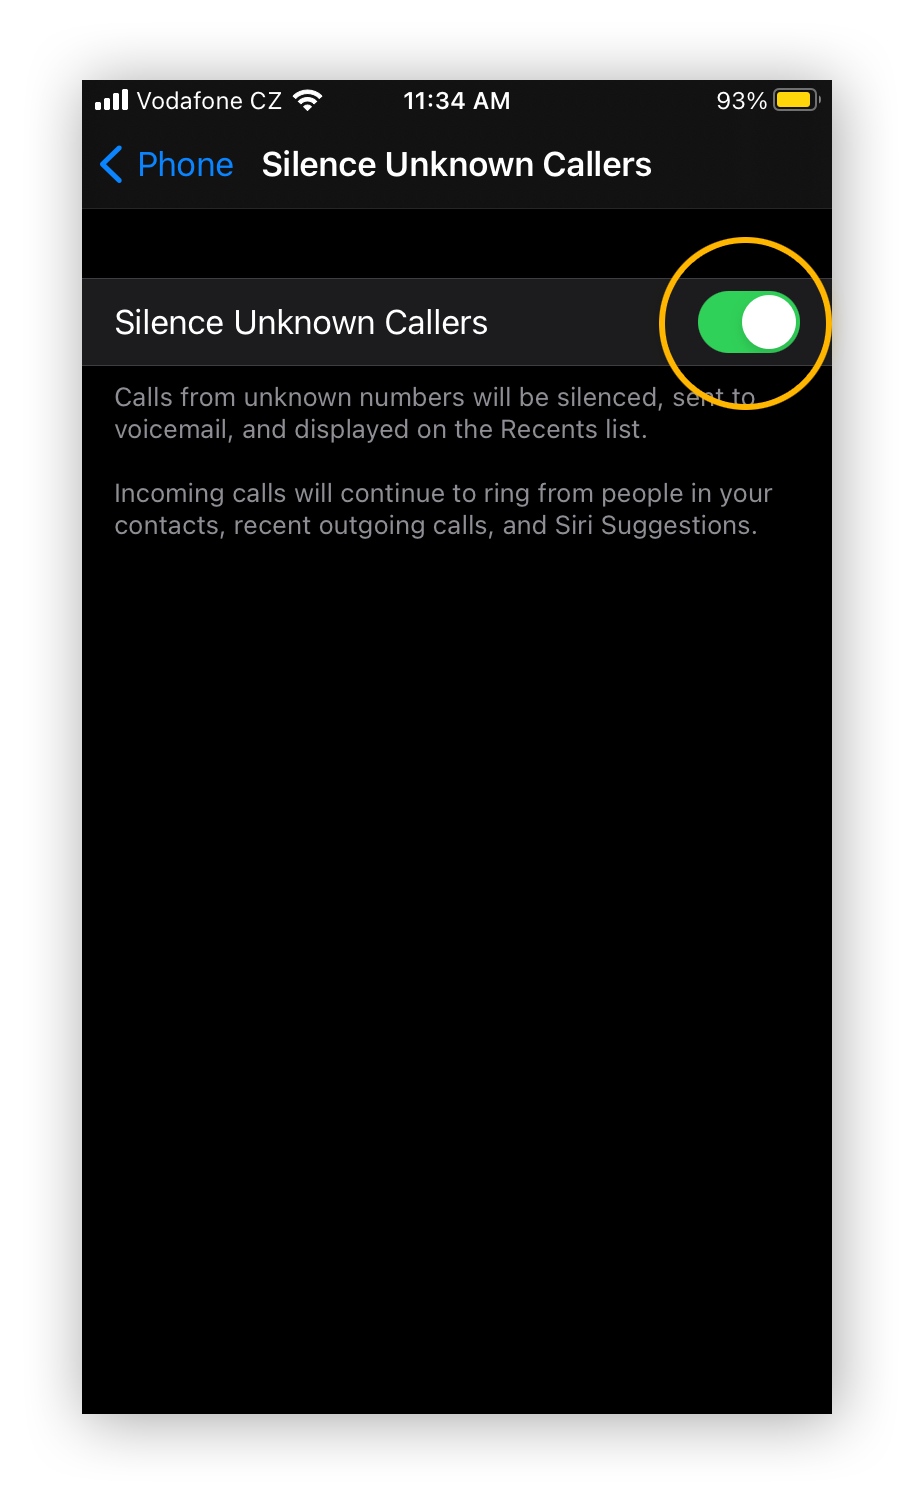
Caller ID Phone Spoofing: What Is It & How to Stop It
/img_06.png?width=875&name=img_06.png)
What is Caller ID Spoofing? How to Prevent and Stop it?
/img_07.png?width=875&name=img_07.png)
What is Caller ID Spoofing? How to Prevent and Stop it?
/img_04.png?width=1050&name=img_04.png)
What is Caller ID Spoofing? How to Prevent and Stop it?
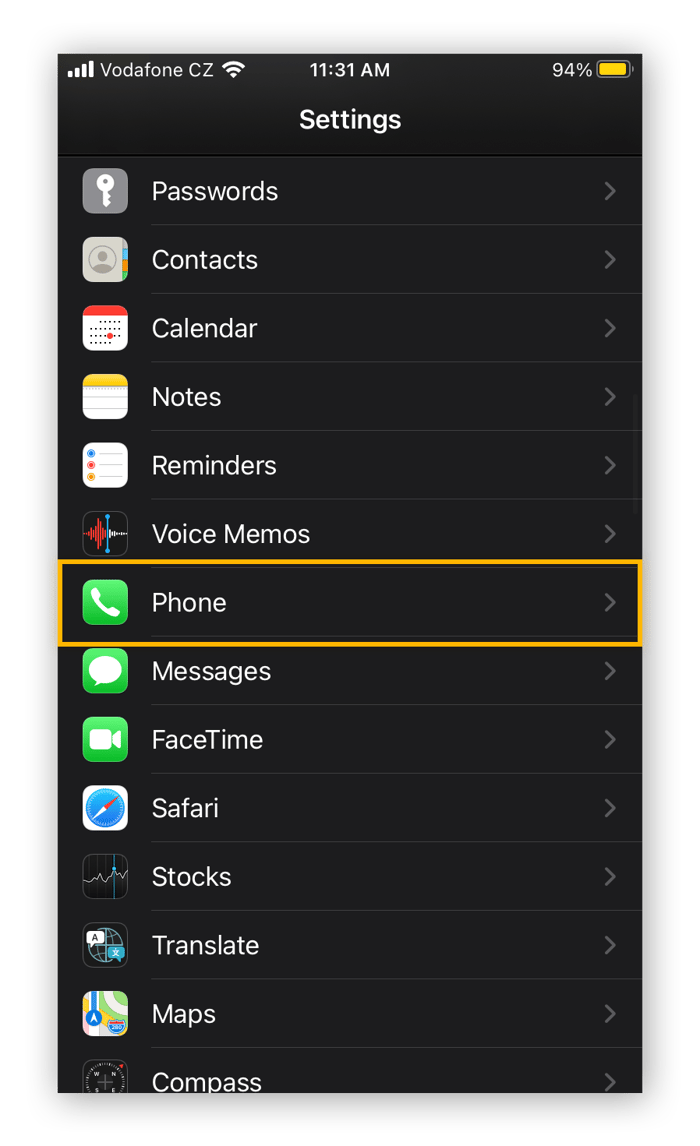
Caller ID Phone Spoofing: What Is It & How to Stop It
/img_03.png?width=1050&name=img_03.png)
What is Caller ID Spoofing? How to Prevent and Stop it?

Caller ID Spoofing - SwordSec

Caller ID Spoofing - SwordSec
The Dark Side of Caller ID: What You Need to Know About Spoofing and ...