6 Steps to an Effective Cyber Incident Response Plan ( Tips)
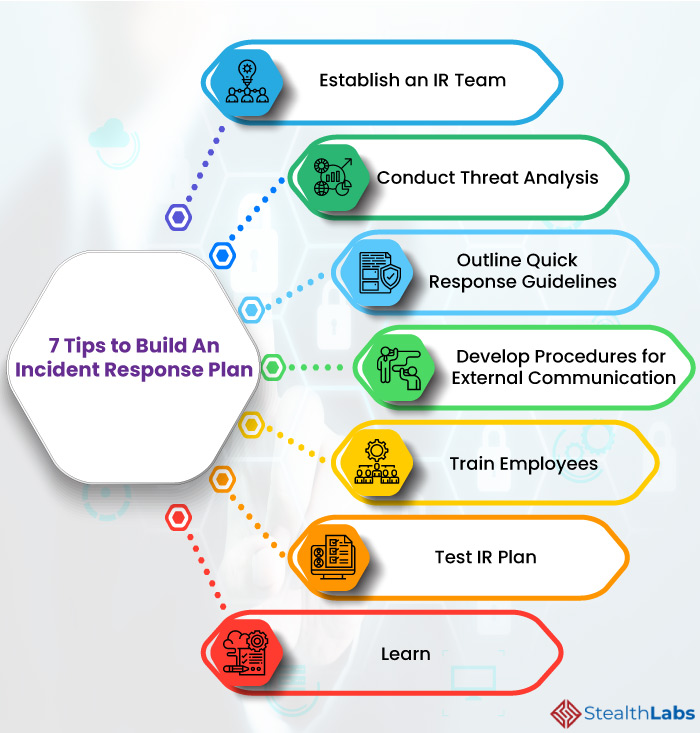
A crisis communication plan for cyber threats is essential. Here are 6 steps and 7 tips for an effective cyber incident response plan .

Learn essential steps for a robust incident response plan , including preparation, detection, containment, and recovery. Enhance security and minimize damage from cyber incidents .
6 Steps to Accelerate Cybersecurity Incident Response

Then the cycle returns to the preparation, where you can make necessary improvements like updating your incident response plan template, technology and processes, and providing your people with better training. 4 pro tips to stay secure Let's conclude with three final suggestions to bear in mind: The more you log, the easier investigation ...
What is an Incident Response Plan (IRP)? An Incident Response Plan (IRP) is a comprehensive, written blueprint of 6 distinct steps to aid IT professionals and your staff in recognizing and dealing with cybersecurity threats, such as data breaches or cyber -attacks. Continual updates and thorough training are the cornerstones of creating and managing an effective IRP.

SANS Incident Response
What Is SANS Incident Response Framework? The SANS incident response framework is a structured approach used by organizations to manage and mitigate cyber security incidents effectively. It incorporates actionable steps and guidelines that help responders identify, analyze, and contain security threats swiftly. This framework ensures a thorough and organized response to cyber incidents ...
Why is an incident response plan important? The Ponemon Institute's Cost of Cyber Crime Study showed that the typical organization experiences an average of 145 security incidents per year and spends $13 million annually year to defend itself. An effective response process can act to significantly reduce these costs. Incident response planning also protects your company's reputation. IDC ...
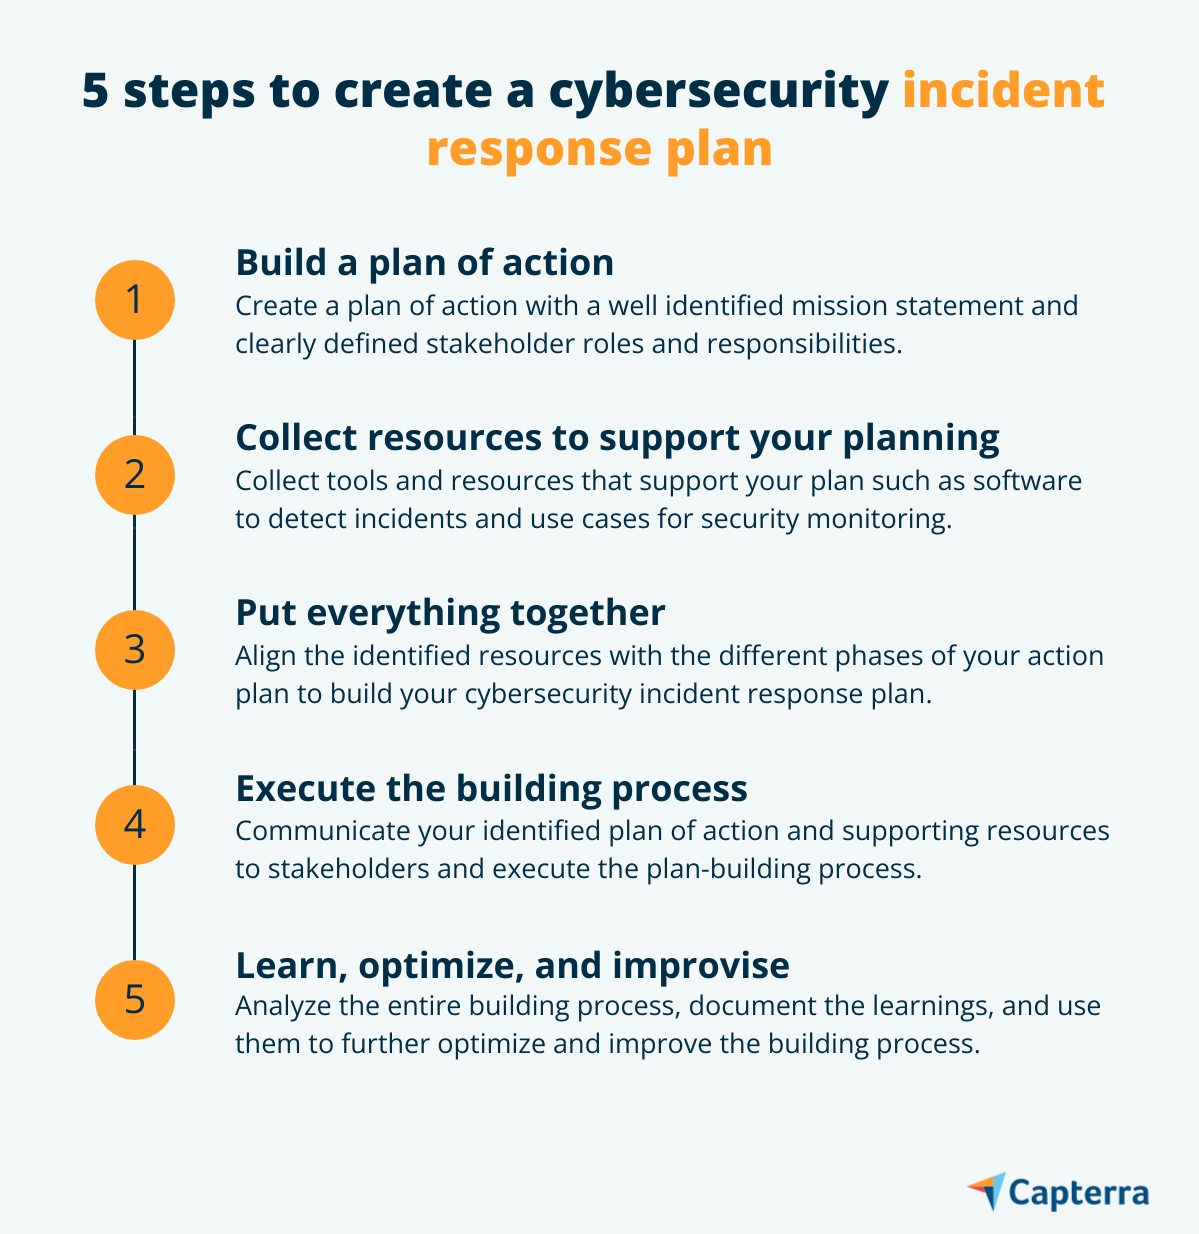
Cybersecurity Incident Response Plan
Build a cybersecurity incident response plan that actually works. Learn key phases, roles, and playbooks so your team can respond faster and limit damage.
Step -by- step CSIRP development guide covering incident detection, containment, and recovery. Based on CIS Critical Security Controls and real-world incident response experiences.

Cyber Incident Response & Recovery
Explore cyber incident response frameworks, recovery strategies, and best practices to detect, contain, and mitigate security threats effectively.


What Is Incident Response ? Incident response is a process that allows organizations to identify, prioritize, contain and eradicate cyberattacks. The goal of incident response is to ensure that organizations are aware of significant security incidents , and act quickly to stop the attacker, minimize damage caused, and prevent follow on attacks or similar incidents in the future.