Cybersecurity Incident Response Plan

Build a cybersecurity incident response plan that actually works. Learn key phases, roles, and playbooks so your team can respond faster and limit damage.
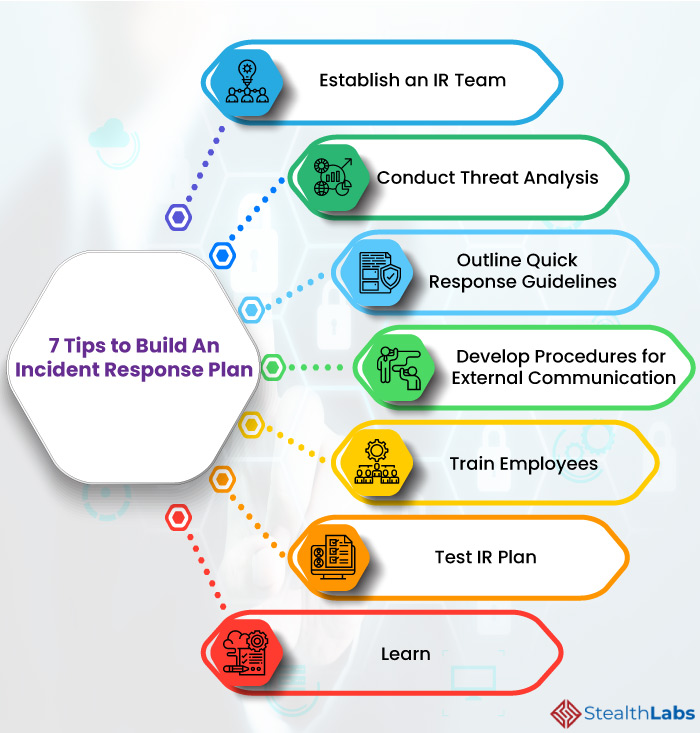
The threat of cyberattacks and ransomware assaults has increased significantly as technology continues to permeate more and more aspects of our daily life. Therefore, any organization must have a cyber - incident response plan to defend against and respond to cyber threats.
PDF Incident Response Plan (IRP) Basics

OVERVIEW An Incident Response Plan is a written document, formally approved by the senior leadership team, that helps your organization before, during, and after a confirmed or suspected security incident . Your IRP will clarify roles and responsibilities and will provide guidance on key activities. It should also include a cybersecurity list of key people who may be needed during a crisis.
Incident Response Plans : Key Take-Aways NIST Special Publication (SP) 800-61 Revision 2, "Computer Security Incident Handling Guide," outlines the principles and steps for developing an Incident Response Plan .

Incident Response
Overview Cyber incidents can harm U.S. national security interests, foreign relations, and the economy and can impact public confidence, civil liberties, and health and safety. Because of this risk, all organizations should have clear, executable cyber incident response plans and strategies to protect their own interests and prevent an incident from growing and causing greater harm.
You've built your digital infrastructure, implemented security controls, and trained your team on best practices. But what happens when - not if - a cyber incident occurs? Without a structured response plan , even minor security events can spiral into full-blown crises, leading to extended downtime, data loss, regulatory penalties, and reputational damage. In 2023 alone, the U.S. recorded over ...

A Guide to Incident Response Plans, Playbooks, and Policy
Get an overview of incident response documentation: the incident response plan , policy, and playbook along with guidance on the key components for an organization to manage a cyber -attack.
Step #1: Preparation No organization can spin up an effective incident response on a moment's notice. A plan must be in place to both prevent and respond to events. Define the CSIRT (Computer Security Incident Response Team) To act quickly and completely while an incident is unfolding, everyone on the CSIRT needs to know their responsibilities and the decisions that are theirs to make. The ...

Incident management vs. incident response explained
How effectively an enterprise handles a cybersecurity incident has a significant effect on how much damage occurs and how quickly the business can recover. Organizations need both incident management and incident response strategies. Although the two terms overlap -- and many security pros use them interchangeably -- they are technically distinct.




Learn what incident response is, its lifecycle, best practices, and when to outsource to protect your organization from cyber threats.