Ldapsearch Multiple Attributes: A Comprehensive Guide
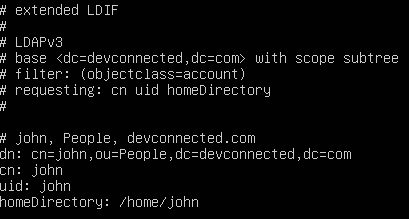
Ldapsearch is a command-line tool used to search and retrieve data from LDAP (Lightweight Directory Access Protocol) directories. One of the powerful features of ldapsearch is its ability to retrieve multiple attributes from the directory in a single query. In this article, we'll delve into the world of ldapsearch multiple attributes and explore its syntax, usage, and best practices.

Understanding LDAP Attributes
Before we dive into ldapsearch multiple attributes, it's essential to understand what LDAP attributes are. LDAP attributes are the individual pieces of data that make up an LDAP entry. For example, the commonName attribute stores the common name of an object, while the objectClass attribute stores the object class of the entry. LDAP attributes are used to store and retrieve information about directory objects.
ldapsearch Syntax for Multiple Attributes
The ldapsearch command uses the following syntax to retrieve multiple attributes:
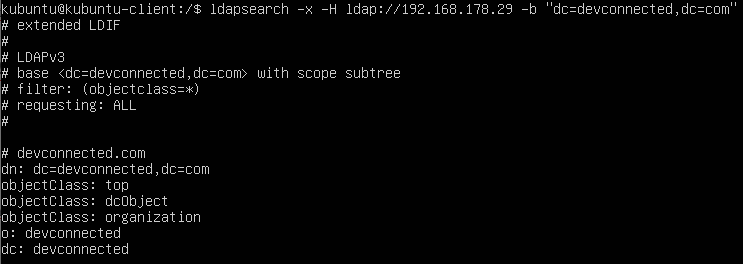
ldapsearch [-D binddn] [-W] [-b basedn] [-s scope] [-a attrs] [-o option] [filter] [attributes]
Where:
-D binddn: Specifies the bind DN (distinguished name) to use for the search.-W: Prompts for a password before performing the search.-b basedn: Specifies the base DN (distinguished name) for the search.-s scope: Specifies the search scope (base, one, or sub).-a attrs: Specifies the attributes to retrieve.-o option: Specifies an LDAP option (e.g., -o defaultSearchScope=one).filter: Specifies the search filter (optional).attributes: Specifies the attributes to retrieve (optional).

For example, to retrieve the commonName and email attributes for all entries in the dc=example,dc=com base DN, you would use the following command:
ldapsearch -D "cn=admin,dc=example,dc=com" -W -b dc=example,dc=com -s sub "(objectclass=*)" cn email
Using the -a Option with ldapsearch

The -a option is used to specify the attributes to retrieve. When using the -a option, you can specify multiple attributes separated by commas. For example:
ldapsearch -D "cn=admin,dc=example,dc=com" -W -b dc=example,dc=com -s sub "(objectclass=*)" -a cn,email,telephoneNumber


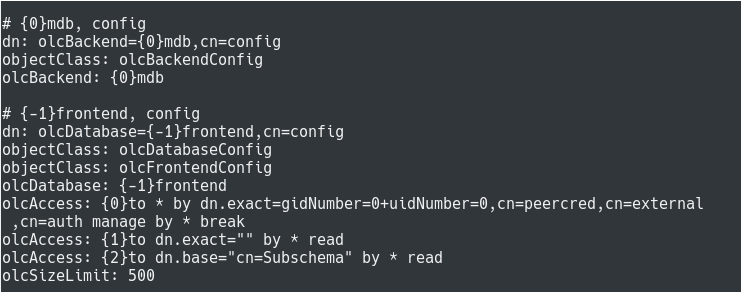


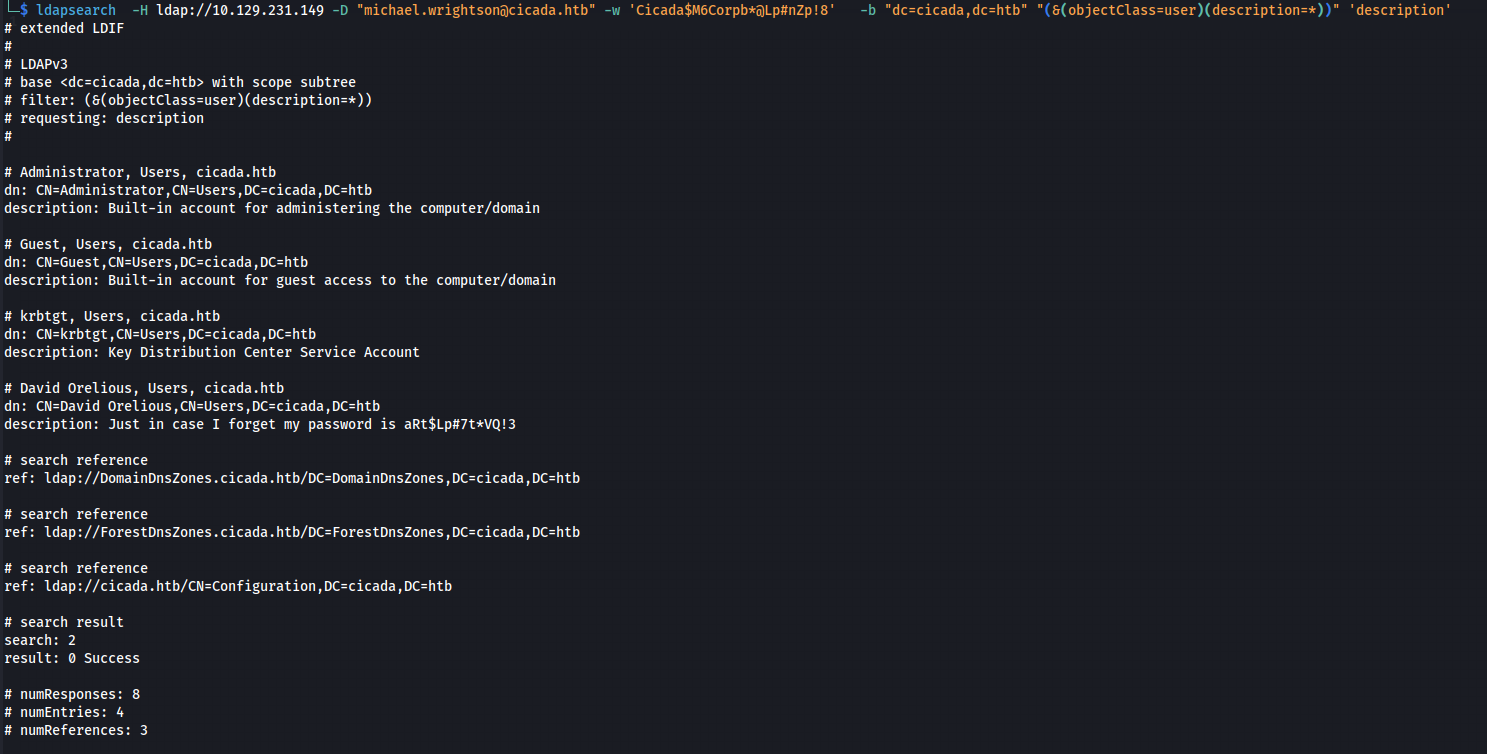


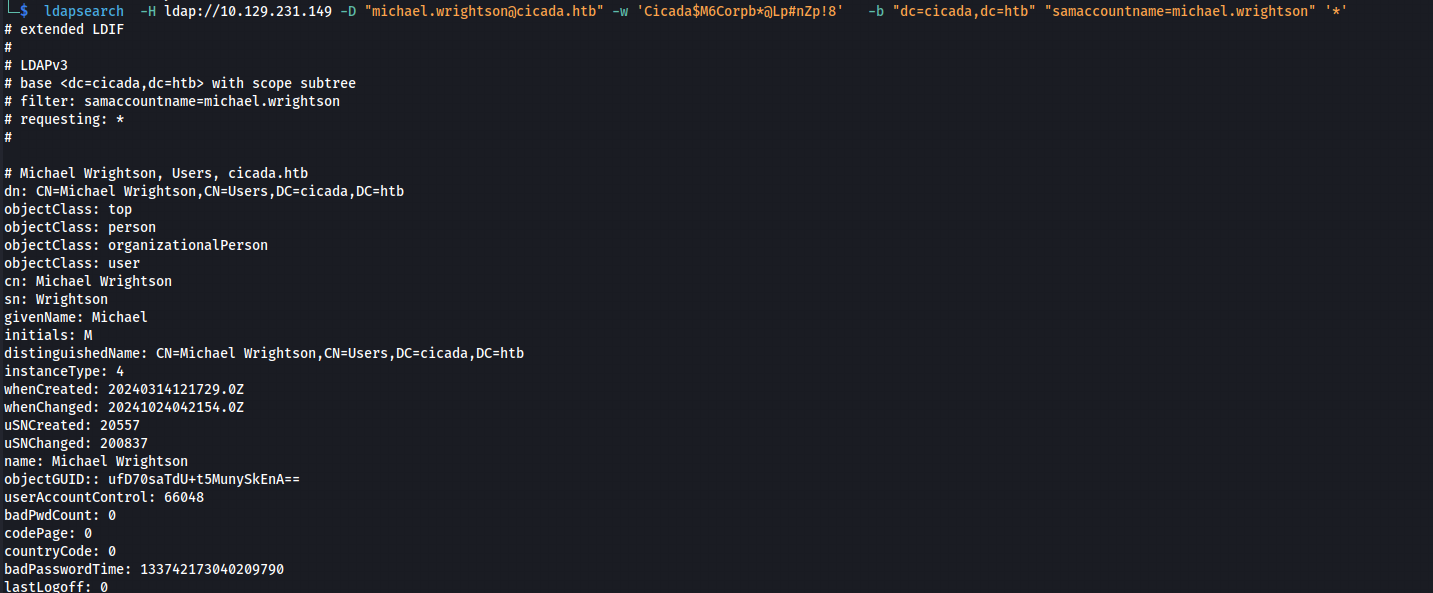
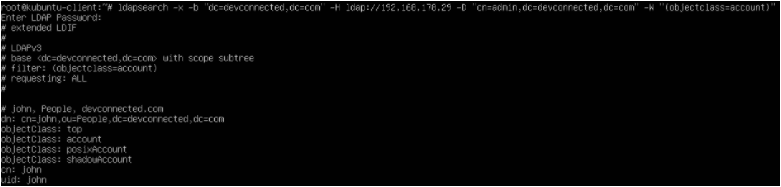
This command retrieves the commonName, email, and telephoneNumber attributes for all entries in the dc=example,dc=com base DN.
Using the -o Option with ldapsearch
The -o option is used to specify an LDAP option. When using the -o option, you can specify options such as defaultSearchScope, timeout, and referrals.
For example:
ldapsearch -D "cn=admin,dc=example,dc=com" -W -b dc=example,dc=com -s sub "(objectclass=*)" -o defaultSearchScope=one -a cn,email,telephoneNumber
This command retrieves the commonName, email, and telephoneNumber attributes for all entries in the dc=example,dc=com base DN with a search scope of one.
Best Practices for ldapsearch Multiple Attributes
When using ldapsearch to retrieve multiple attributes, it's essential to follow best practices to ensure optimal performance and security.
- Use the
-aoption to specify multiple attributes. - Use the
-ooption to specify LDAP options. - Use the
-Dand-Woptions to authenticate with the directory. - Use the
-boption to specify the base DN for the search. - Use the
-soption to specify the search scope. - Use the
filteroption to specify the search filter (optional). - Use the
attributesoption to specify the attributes to retrieve (optional).
Conclusion
ldapsearch is a powerful tool for searching and retrieving data from LDAP directories. By using the -a and -o options, you can retrieve multiple attributes and customize the search behavior. By following best practices and understanding the ldapsearch syntax, you can efficiently and securely search and retrieve data from your LDAP directory.